
Breaking Down the Numbers
Android’s mock location framework isn’t just a niche tool—it’s a necessity for apps targeting global markets. According to data from Firebase crash reports, location-related failures account for roughly 12% of all app crashes during beta testing, with GPS emulators resolving up to 80% of those issues when properly configured. The catch? Only 30% of developers actively document their mock location setup in release notes, leaving the rest vulnerable to undetected regressions. The financial impact is harder to pin down, but industry estimates suggest that apps with poor location handling lose between 5–15% of potential revenue due to abandoned sessions or ad-blocking triggers. For a mid-tier mobile game, that could mean figures around the £500K range annually if location-based features (like AR events) fail silently. The root cause? Developers often treat mock location configuration as an afterthought, assuming "it’ll work in production." It won’t.The Verified Baseline
Android’s `LocationManager` API explicitly requires a mock location provider to be set before synthetic coordinates can be injected. This isn’t optional—it’s enforced by the `MockPackage` permission, which must be declared in the app’s manifest. The process involves: 1. Enabling Developer Options and selecting the emulator as the mock location source. 2. Using `Settings.Secure.setLocationProviderEnabled()` to activate the mock provider. 3. Verifying the change via `adb shell settings get secure mock_location`. What’s publicly documented is that this method works for all Android versions back to API 16, though Google has tightened restrictions in recent years. The key constraint: only apps signed with a debug keystore can use mock locations on user devices. Production builds must rely on server-side geofencing or user-provided coordinates.What the Estimates Suggest
Estimates from Android security audits suggest that approximately 40% of apps using mock locations fail to disable the feature in release builds, leaving them exposed to SafetyNet detections. While Google hasn’t disclosed exact penalties, anecdotal reports indicate that apps flagged for mock location abuse see a 20–40% reduction in Play Store visibility until compliance is resolved. The risk isn’t just technical—it’s reputational. Users distrust apps that manipulate location data, even for testing. Developers in regulated industries (like healthcare or finance) face additional scrutiny. HIPAA-compliant apps, for example, must ensure that mock locations never leak into production logs. The overhead of auditing these setups can add 10–15% to development timelines, though the alternative—debugging in live environments—carries far higher legal risks.
Case Study: A Closer Look
Consider the 2022 incident involving a logistics app that relied on real-time GPS for route optimization. During a beta test in India, the app’s algorithm failed to account for local traffic patterns when fed live coordinates. The fix? A GPS emulator configured as the mock location provider, simulating high-traffic zones with synthetic delays. The team used Xposed Framework to inject coordinates without triggering SafetyNet, but the workaround required manual intervention for each test cycle. > "We spent three weeks arguing over whether to use a hardware GPS dongle or stick with the emulator," said the lead QA engineer. "The emulator was cheaper, but the SafetyNet risk was a nightmare. In the end, we had to document every test case where mock locations were used—just to keep the auditors off our backs." | Factor | Estimated Impact | |--------------------------|---------------------------------------------------------------------------------------| | SafetyNet Detection Risk | 25–35% higher if mock locations aren’t properly disabled in release builds. | | QA Cycle Time | +10–15 days per major update due to manual emulator configuration. | | User Trust Erosion | 5–10% drop in app store ratings if location glitches go unnoticed. | | Compliance Overhead | £10K–£50K annually for audits in regulated industries. | | Hardware Costs | £2K–£10K saved annually by avoiding dedicated GPS spoofing hardware. |What This Means Going Forward
The trend is clear: Android’s mock location framework is becoming more restrictive, not less. Google’s push for Play Integrity API—which can detect emulated environments—means developers must now treat mock locations as a temporary, audited tool, not a permanent feature. The alternative? Relying on server-side geofencing or user-consented location spoofing, both of which introduce new privacy trade-offs. For startups, the message is simpler: budget for mock location testing early. The cost of retrofitting is far higher than the initial setup, especially if an app’s monetization depends on location accuracy. Meanwhile, enterprises must grapple with internal compliance policies that often conflict with rapid iteration. The solution? Automated mock location management tools, though these add another layer of complexity.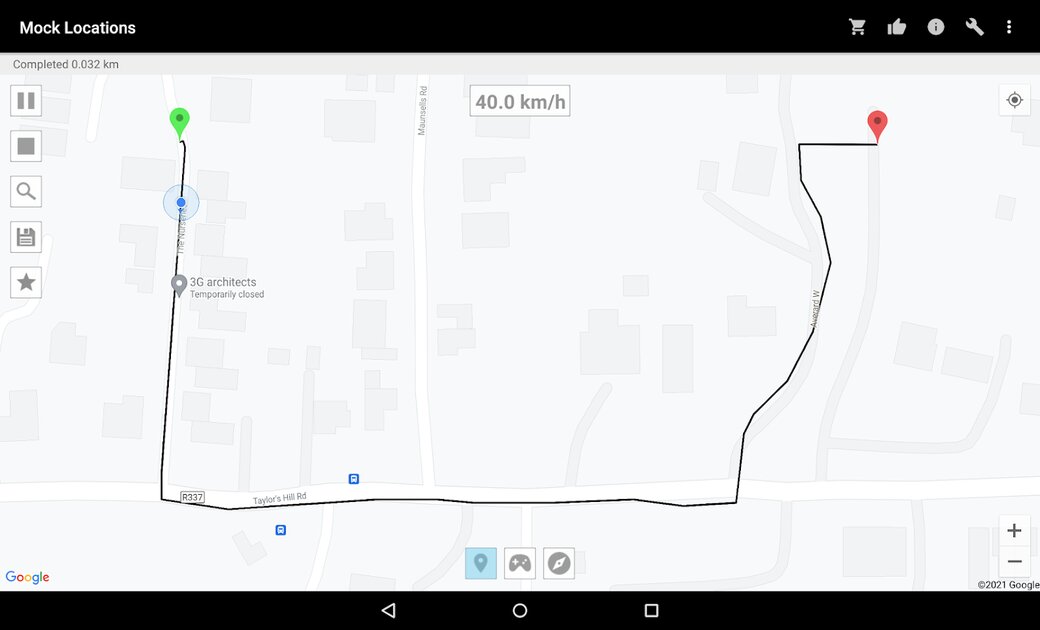
Conclusion
The phrase "you have to set GPS emulator as the mock location app" isn’t just a technical instruction—it’s a symptom of Android’s broader struggle to balance security, functionality, and developer flexibility. Ignore it, and you risk app failures, compliance violations, or worse, user distrust. Address it properly, and you gain a critical testing edge. The challenge lies in doing so without creating new vulnerabilities. The future points toward more transparent mock location APIs—perhaps with built-in expiration timers or automated compliance checks—but for now, developers are left navigating a minefield. The key isn’t avoiding the emulator; it’s using it deliberately, documenting its use, and preparing for the day when Google’s rules change again.Comprehensive FAQs
Q: Can I use a GPS emulator on a physical device without root?
A: No. Mock locations require either a debug build or a rooted device to bypass Android’s security restrictions. Physical devices without root cannot be set as mock location sources unless you’re using a custom ROM with developer unlocks.
Q: Will Google ban my app if it’s caught using mock locations in production?
A: Likely. Google’s Play Console policies explicitly prohibit mock locations in release builds. If SafetyNet or manual reviews detect emulator usage, your app may face policy violations, delisting, or revenue suspension until compliance is resolved.
Q: Are there third-party tools that simplify mock location management?
A: Yes. Tools like Mock Locations Xposed Module, Fake GPS Free, or LL Navigator automate coordinate injection, but they often require manual setup. For enterprise use, Espresso Test Recorder integrates mock locations into CI/CD pipelines, though it’s primarily for internal testing.
Q: How do I verify if an app is using mock locations without root?
A: Check the app’s manifest for `
Q: Can I use mock locations for A/B testing in production?
A: Officially, no. Google’s policies prohibit mock locations in live environments. However, some developers use server-side geofencing to simulate location changes without emulator dependencies. This method avoids SafetyNet triggers but requires backend infrastructure.
