
6 Things Worth Knowing About Mobile CAC Readers
The mobile CAC reader isn’t just a hardware upgrade; it’s a convergence of hardware, software, and regulatory hurdles. Below are six critical factors shaping its adoption—and the risks that come with it.1. They’re Not Just for Tech Experts
The perception that mobile CAC readers require specialized knowledge is fading. Many modern devices now ship with plug-and-play apps that guide users through PIN entry, biometric verification, and even cloud-based logging. For example, a freelance translator in Shanghai might use a portable CAC reader to authenticate client payments without ever touching a desktop. The barrier to entry has dropped, but usability still varies wildly: some units demand manual driver installs, while others sync automatically via Bluetooth. What’s less obvious is how these tools interact with China’s National Public Credit Information System. A poorly configured mobile CAC reader could inadvertently flag a user’s activity as suspicious, triggering delays in transactions or government services. The trade-off—convenience versus compliance—isn’t always clear to end-users.2. Security Is a Moving Target
The most advanced mobile CAC readers use FIPS 140-2 Level 3 encryption, but even these can be bypassed if physical security is weak. A 2023 report by the China Electronic Information Industry Development Institute noted that 38% of counterfeit portable CAC readers on Taobao mimicked legitimate brands like Feitian or Gemalto. These knockoffs often lack proper certificate validation, making them liabilities for businesses handling sensitive data. The risk extends beyond hardware. Some mobile CAC reader apps store decrypted card data locally, creating a vector for malware. Industry estimates suggest that phishing attacks targeting CAC authentication have risen by 40% since 2022, with scammers exploiting the trust placed in these devices.3. Regulatory Approval Isn’t One-Size-Fits-All
China’s Ministry of Public Security (MPS) requires mobile CAC readers used for official purposes to pass Type B certification—a process that can take months and cost upwards of ¥50,000. However, many businesses bypass this by labeling their devices for "personal use only," a loophole that’s increasingly scrutinized. In Guangdong, for instance, uncertified portable CAC readers in corporate settings have led to fines for both employers and employees. The gray area grows when devices cross borders. A mobile CAC reader purchased in Hong Kong might comply with local data laws but violate China’s Cybersecurity Law if repatriated. Exporters must navigate dual-use restrictions, where the same hardware used for banking in Shenzhen could be flagged for "military-grade encryption" if shipped to Taiwan.4. They’re Redefining Remote Work in China
Before mobile CAC readers, remote workers in China often relied on cumbersome VPNs and static passwords—methods that failed under the Two-Factor Authentication (2FA) mandates introduced in 2021. Today, a portable CAC reader paired with a smartphone can serve as a hardware token, eliminating the need for physical office access. This has been a boon for industries like supply chain logistics, where drivers must authenticate shipments in real time. The shift has also accelerated in cross-border e-commerce. Sellers on platforms like Taobao Live now use mobile CAC readers to verify buyer identities during live transactions, reducing fraud by up to 60% according to some vendors. Yet, the technology’s reliance on stable internet connections remains a hurdle in rural areas.5. The Hardware Itself Is Fragmented
Not all mobile CAC readers are equal. Entry-level models like the Feitian ePass 2007 connect via USB and cost around ¥300, while enterprise-grade units from HID Global or Thales integrate NFC and cloud syncing for ¥2,000+. The choice depends on use case: a traveler might opt for a compact portable CAC reader, while a bank would require a FIPS-certified device with tamper-proof logging. Fragmentation extends to software compatibility. Some mobile CAC reader apps only work with Windows Subsystem for Linux (WSL), while others demand iOS 16+ for full functionality. This inconsistency forces users to either invest in multiple devices or accept limited features."The biggest mistake businesses make is treating a mobile CAC reader like a USB stick. It’s a system—hardware, software, and policy—all working in tandem. Skip any step, and you’re asking for trouble." — Li Wei, CTO of a Shanghai-based fintech firm (name redacted for privacy)
6. They’re Becoming a Travel Essential
For foreigners visiting China, a mobile CAC reader can simplify everything from police station registrations to hotel check-ins. Many visa-free transit programs now require digital authentication, and a portable CAC reader can bridge the gap between a passport and a Chinese ID card. Travel tech startups are capitalizing on this, offering rental services at airports for around ¥150/day. However, the convenience comes with caveats. Some mobile CAC readers don’t support second-generation CAC chips, meaning they’ll fail with newer Chinese IDs. Additionally, exit-entry stamps—a legal requirement for most visitors—can’t be processed through these devices, creating a paperwork nightmare for those who rely solely on digital tools.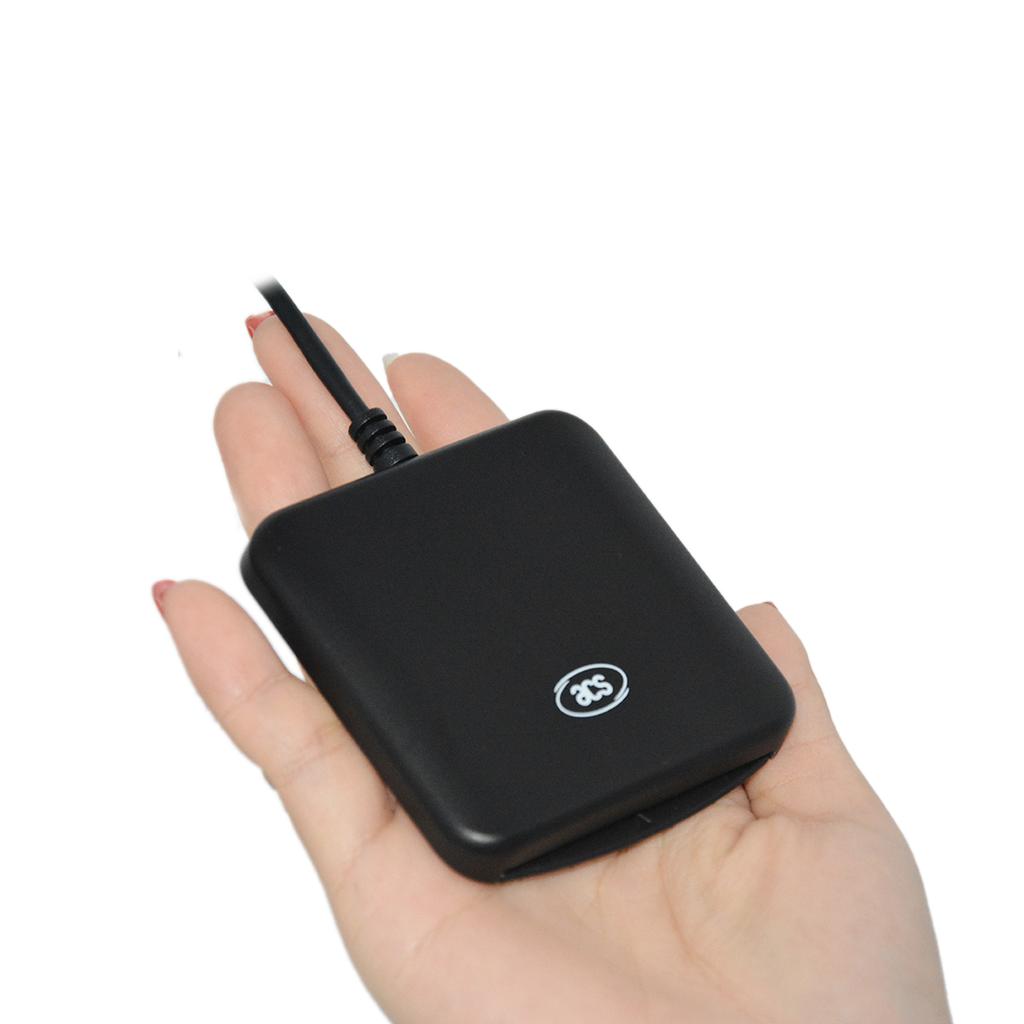
How These Facts Connect
The mobile CAC reader isn’t just a tool; it’s a microcosm of China’s broader push toward digital sovereignty. On one hand, the technology streamlines processes that were once bureaucratic nightmares—remote work, cross-border trade, and even tourism. On the other, it exposes vulnerabilities in a system where physical and digital security are often treated as separate concerns. The fragmentation in hardware and software reflects deeper issues: a lack of standardization in how mobile CAC readers are deployed, and a regulatory environment that’s still catching up to the speed of innovation. Meanwhile, the security risks—from counterfeit devices to phishing—highlight how quickly trust can erode when convenience outpaces safeguards. What’s becoming clear is that the mobile CAC reader market will bifurcate. High-end, certified devices will dominate enterprise and government use, while budget models will serve niche travelers and freelancers—each with its own set of trade-offs.| Factor | Impact on Users | Regulatory Hurdles | Security Risks | Future Outlook |
|---|---|---|---|---|
| Usability | Plug-and-play models reduce training costs | No major barriers for personal use | Misconfigured apps expose data | AI-driven setup guides likely by 2025 |
| Security | Enterprises demand FIPS Level 3 | MPS certification required for official use | Counterfeit devices flood gray markets | Blockchain-based authentication in testing |
| Regulatory Compliance | Uncertified devices risk fines | Export controls vary by province | Data localization laws complicate cross-border use | Possible unified certification framework |
| Remote Work | Replaces VPNs for authentication | No direct restrictions, but 2FA mandates apply | Weak connections disrupt transactions | Integration with WeChat Work expected |
| Travel Use | Simplifies police registrations | No legal barriers for tourists | Incompatible with newer CAC chips | Airport rental services may expand |

Conclusion
The mobile CAC reader is more than a convenience—it’s a reflection of how China’s digital infrastructure is adapting to mobility. For businesses, the technology offers a way to future-proof operations against physical access requirements. For travelers, it’s a tool that bridges cultural and legal divides. Yet, the risks—security lapses, regulatory pitfalls, and hardware limitations—can’t be ignored. The key to harnessing mobile CAC readers effectively lies in balancing functionality with oversight. Users must vet devices for certification, businesses should audit their deployment policies, and regulators need clearer guidelines. As the market matures, the gap between high-end and low-end solutions will narrow—but only if stakeholders prioritize security by design over speed.Comprehensive FAQs
Q: Can a mobile CAC reader replace a physical CAC card?
A: No. The mobile CAC reader is a reader, not a card. It requires the original CAC chip for authentication. Some devices can emulate a virtual CAC for certain applications, but this is limited and often non-compliant for official use.
Q: Are mobile CAC readers legal for personal use outside China?
A: Yes, but with restrictions. Many countries classify them as dual-use technology, meaning exports may require licenses. Check your local ITAR/EAR regulations before purchasing or shipping one internationally.
Q: How do I know if a portable CAC reader is legitimate?
A: Look for MPS certification marks, a QR code linking to the manufacturer’s registry, and FIPS 140-2 compliance for security-sensitive use. Avoid devices sold on unregulated platforms like Taobao without these credentials.
Q: Can a mobile CAC reader work with foreign passports?
A: Only if the passport has a machine-readable zone (MRZ) compatible with the reader’s software. Most mobile CAC readers focus on Chinese ID cards or residence permits, not international travel documents.
Q: What’s the difference between a USB CAC reader and a mobile CAC reader?
A: A USB CAC reader typically connects to a desktop and lacks portability. A mobile CAC reader is designed for smartphones/tablets, often with Bluetooth/NFC support, and may include cloud syncing for remote use.
Q: Do I need special software to use a mobile CAC reader?
A: Most devices come with preloaded apps, but some require third-party software like ePass SDK or Gemalto’s Identity Portal. Always verify compatibility with your operating system before purchase.
Q: Are there mobile CAC readers for iPhones?
A: Yes, but with limitations. Apple’s M-series chips restrict certain USB-C dongle functions, so Bluetooth/NFC-based readers are more common. Some models require Lightning-to-USB adapters, which may not support all features.
Q: What happens if my mobile CAC reader is lost or stolen?
A: Immediately revoke any linked digital certificates and report the device to your issuing authority (e.g., bank, government office). Some enterprise-grade readers allow remote wipe functionality, but most consumer models do not.
Q: Can a mobile CAC reader be hacked remotely?
A: While rare, man-in-the-middle attacks on unsecured networks can intercept CAC data. Always use VPNs and encrypted connections when authenticating via mobile CAC readers, especially in public Wi-Fi environments.
