
Where It All Began
The concept of caller ID faker software emerged in the late 1990s, when early VoIP (Voice over Internet Protocol) systems allowed users to manipulate call metadata. Hackers quickly realized they could override the default caller ID fields, displaying anything from fake names to entirely fabricated numbers. The first documented cases involved college students pranking each other, but the technology’s potential for harm was evident from the start. Law enforcement noted that spoofed calls could mask illegal activities, from drug deals to harassment. The tools themselves were rudimentary at first—often requiring technical knowledge to bypass carrier protocols. Early versions of caller ID faker software relied on open-source libraries and manual configuration, limiting their reach. However, the foundation was set: a method to deceive call recipients without leaving a trace. As the internet democratized access to programming tools, so too did the ability to create and distribute these applications. By the mid-2000s, underground forums began trading scripts for "number cloning," where users could mimic an entire phone’s identity.The Early Signs
The first red flags appeared in 2003, when telemarketers in India used spoofed numbers to bypass "do not call" registries. The FCC later confirmed that caller ID faker software was being employed to evade regulations, marking the first major regulatory concern. Around the same time, cybersecurity researchers identified a surge in "vishing" (voice phishing) attacks, where scammers used spoofed IDs to lure victims into revealing personal details. The tools were still clunky, but the pattern was clear: fraudsters were adapting faster than laws could respond. What made the early iterations dangerous wasn’t just their functionality, but their accessibility. Unlike traditional hacking tools, caller ID faker software required minimal technical skill. Tutorials on YouTube and dark web marketplaces broke down the process into simple steps, from purchasing a VoIP account to configuring the spoofing script. The barrier to entry dropped to near zero, turning a niche exploit into a mainstream threat. By 2010, even non-technical users could deploy these tools with a few clicks.The Turning Point
The shift from novelty to weapon occurred when caller ID faker software became a staple in organized crime. No longer confined to pranks or small-scale scams, it was now a critical component of large-scale fraud operations. The FBI’s 2016 report on BEC scams highlighted how spoofed numbers were used to impersonate CEOs, instructing employees to transfer funds under false pretenses. The attacks were sophisticated: callers would mimic executive voices, cite urgent (but fake) legal issues, and exploit the victim’s trust before the money vanished. The turning point wasn’t just the scale—it was the speed. Where traditional fraud required weeks of planning, caller ID faker software enabled attacks in minutes. A single spoofed call could bypass multi-factor authentication if the recipient assumed the number was legitimate. The software’s ability to generate disposable, untraceable numbers made it ideal for extortion, where victims were pressured to pay ransoms before the caller moved on to the next target."By the time we realized the calls were spoofed, the fraudsters had already drained accounts totaling millions. The software wasn’t just faking IDs—it was rewriting the rules of trust." — Federal Communications Commission investigator (2017)
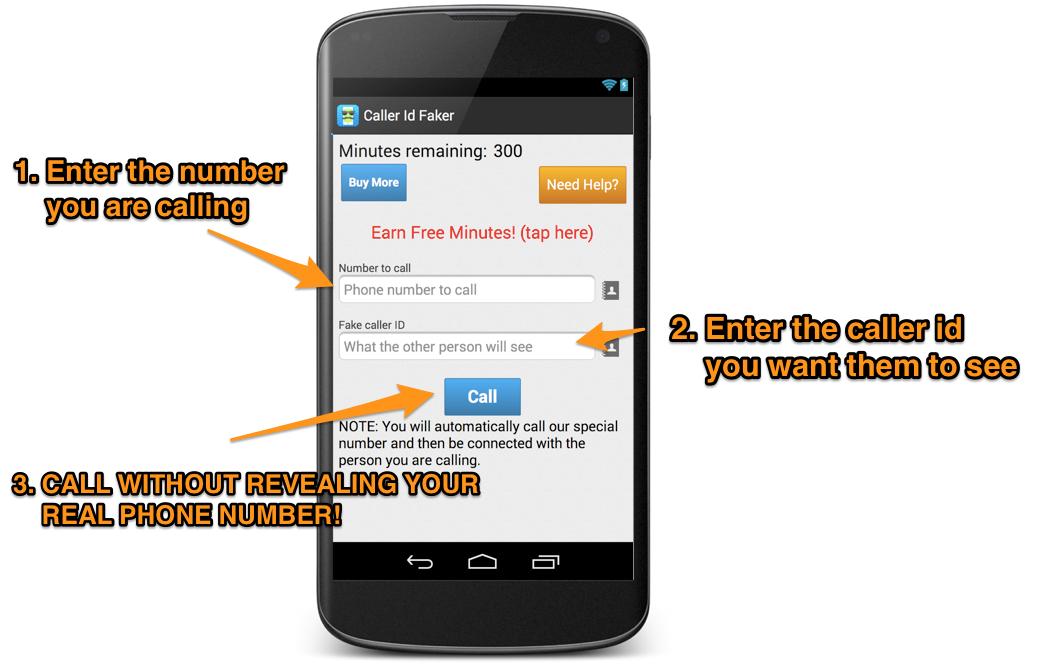
The Build-Up, Year by Year
| Period | Key Developments |
|---|---|
| 2003–2006 | First regulatory alerts on telemarketing spoofing; FCC identifies caller ID faker software as a compliance risk. |
| 2007–2010 | Underground markets emerge for VoIP-based spoofing tools; tutorials appear on public forums. |
| 2011–2014 | Rise of "SIM swapping" attacks, where fraudsters use spoofed numbers to hijack accounts via carrier vulnerabilities. |
| 2015–Present | AI voice cloning integrates with caller ID faker software, enabling hyper-realistic impersonations; global fraud losses exceed $50 billion annually. |
Lessons From the Journey
- Accessibility bred abuse: The lower the technical barrier, the faster the tools spread. What started as a hacker’s trick became a crime syndicate’s toolkit.
- Regulation lagged: Laws focused on blocking spoofed calls, but the software evolved to bypass those measures—often before enforcement caught up.
- Trust erosion: Victims of spoofed calls now distrust even legitimate numbers, creating a feedback loop of paranoia.
- Cross-industry impact: From healthcare (fake doctor calls) to finance (executive impersonation), no sector was immune.
- Dark web economies: Vendors selling caller ID faker software operate in jurisdictions with weak extradition laws, making prosecution difficult.
- AI amplification: The fusion of spoofing tools with voice synthesis has made detection nearly impossible without advanced forensics.
Where Things Stand Today
The current landscape is defined by two opposing forces: the relentless innovation of fraudsters and the piecemeal efforts of regulators. Carriers like AT&T and Verizon have implemented "SHAKEN/STIR" protocols to verify call authenticity, but the measures are easily circumvented by determined attackers. Meanwhile, caller ID faker software has fragmented into specialized variants—some designed for mass phishing campaigns, others tailored for targeted extortion. The tools are now sold as "subscription services," with features like "caller ID rotation" to evade detection algorithms. What’s changed is the stakes. High-profile cases, such as the 2022 impersonation of a UK energy executive (resulting in a £22 million transfer), have forced governments to reconsider penalties. Some jurisdictions now classify caller ID faker software as a felony-level offense, but enforcement remains inconsistent. The software’s creators, often operating from countries with minimal cybercrime laws, continue to refine their products, adding layers of encryption and disposable infrastructure to stay ahead of law enforcement.
Conclusion
The story of caller ID faker software is one of unintended consequences. What began as a curiosity for tech enthusiasts became a vector for some of the most damaging financial crimes of the digital age. The tools themselves are neither good nor evil—they’re neutral, shaped by the hands that wield them. Yet the damage persists, not just in stolen funds or ruined reputations, but in the erosion of a fundamental trust: the assumption that a phone call is from whom it claims to be. The solution isn’t just better technology—it’s a global consensus on accountability. Until vendors face consequences for enabling fraud, and until regulators can keep pace with innovation, the cycle will continue. The question isn’t whether caller ID faker software will disappear; it’s whether society can adapt before the next wave of abuse redefines the threat.Comprehensive FAQs
Q: Is caller ID faker software legal?
Legality varies by country. In the U.S., the Truth in Caller ID Act (2009) prohibits intentional spoofing for fraudulent purposes, but enforcement is inconsistent. Many vendors operate in jurisdictions with lax cybercrime laws, making prosecution difficult.
Q: Can I be prosecuted for using caller ID faker software?
Yes, if the software is used for fraud, harassment, or illegal activities. Authorities have charged individuals under wire fraud and identity theft statutes, but cases often hinge on proving intent and jurisdiction.
Q: How do fraudsters bypass carrier protections?
Attackers exploit weaknesses in VoIP protocols, use disposable SIMs, or route calls through international gateways to evade local restrictions. Some caller ID faker software includes "number masking" to hide the origin of the call.
Q: Are there legitimate uses for caller ID faker software?
Some businesses use it for internal testing (e.g., simulating customer calls), but ethical concerns outweigh the benefits. Most vendors disclaim responsibility for misuse, leaving users in legal gray areas.
Q: How can I protect myself from spoofed calls?
Never trust caller ID alone—verify the caller’s identity through a separate channel. Enable call-blocking features, avoid sharing personal details over the phone, and report suspicious activity to your carrier and authorities.
Q: What’s the future of caller ID faker software?
Expect further integration with AI voice cloning and deepfake technology, making impersonations nearly indistinguishable. Regulators may introduce blockchain-based call verification, but fraudsters will likely adapt with new evasion tactics.
Q: Where can I report caller ID faker software abuse?
In the U.S., file complaints with the FCC or IC3. For international incidents, contact your local cybercrime unit or consumer protection agency.
