Breaking Down the Numbers
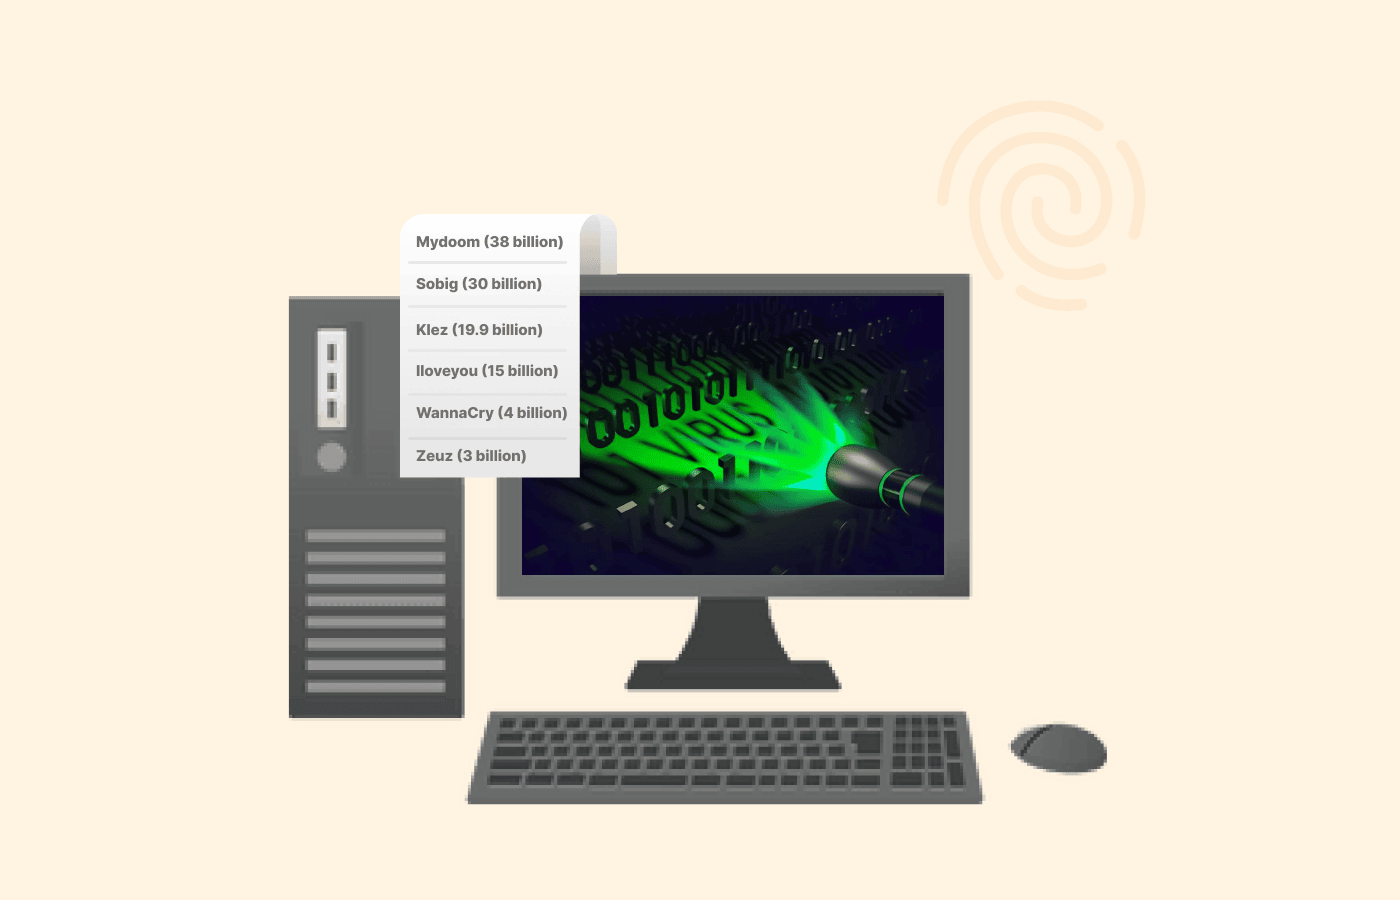
To determine what is the worst computer virus in the world, we must dissect three metrics: direct financial loss, operational disruption, and long-term geopolitical consequences. Stuxnet’s estimated cost to Iran’s nuclear program ranges from $1 billion to $10 billion, according to declassified U.S. intelligence reports, though Iran’s official figures remain classified. The worm delayed the program by at least two years, forcing Tehran to rebuild its centrifuges from scratch—a setback with no parallel in modern cyber history. Meanwhile, ransomware attacks in 2023 alone generated what is the worst computer virus in the world in revenue terms: LockBit’s affiliates reportedly extorted over $90 million in the first half of the year, while DarkSide’s Colonial Pipeline attack in 2021 cost the U.S. fuel industry $4.4 million in ransom plus an additional $4.5 million in operational recovery. The true damage, however, extends beyond balance sheets. What is the worst computer virus in the world isn’t just the one that drains bank accounts—it’s the one that forces governments to confront vulnerabilities in their most critical systems. When WannaCry exploited the EternalBlue flaw (originally stolen from the NSA), it exposed how easily cyber weapons could be weaponized against civilian infrastructure. The attack grounded flights at Heathrow, halted German train networks, and forced Spain’s Telefonica to shut down 90% of its call centers. These weren’t isolated incidents; they were proof that what is the worst computer virus in the world could emerge from either a state actor’s playbook or a hacker’s garage. The line between sabotage and crime had blurred—and the world was ill-prepared.The Verified Baseline
Publicly available data confirms Stuxnet as the most what is the worst computer virus in the world in terms of physical destruction. The worm, discovered in 2010, was designed to target Siemens SCADA systems controlling Iran’s uranium enrichment centrifuges. It achieved this through a multi-stage attack: first infecting a Windows machine, then spreading to the industrial control systems via a zero-day exploit in Windows XP. Once inside, Stuxnet altered the frequency of the centrifuges’ rotations, causing them to spin out of control and self-destruct. Symantec’s 2011 analysis of the malware’s code revealed it had been in development since at least 2005, with components written in five different programming languages—a level of sophistication unseen in civilian malware at the time. The U.S. government’s confirmation in 2021 that American and Israeli operatives had developed Stuxnet removed any doubt about its origins. What is the worst computer virus in the world in this context isn’t a question of intent but of execution: Stuxnet didn’t just steal data or encrypt files—it physically damaged machinery. Iran’s nuclear program was set back years, and the country’s cyber defenses were forced to evolve overnight. Unlike financial malware, which can be traced to a single actor, Stuxnet represented a new class of cyber weapon, one that could be deployed with surgical precision against a specific target. This made it not just a virus, but a strategic tool—and one that would inspire future attacks, from NotPetya to the 2022 HermeticWiper strikes in Ukraine.What the Estimates Suggest
Industry estimates place Stuxnet’s total cost to Iran at between $1 billion and $10 billion, though these figures are speculative. The worm’s impact wasn’t just financial; it forced Iran to abandon its original centrifuges and adopt more resilient models, delaying the program by at least two years. Security firm CrowdStrike has suggested that Stuxnet’s development cost the U.S. around $50 million to $100 million, a fraction of the damage it inflicted—a ratio that underscores its efficiency as a weapon. In contrast, ransomware’s financial toll is easier to quantify: what is the worst computer virus in the world in terms of direct extortion payments is LockBit, which has reportedly earned its operators hundreds of millions annually. Yet ransomware’s indirect costs—downtime, regulatory fines, and reputational damage—often dwarf the ransom itself. The most damaging aspect of what is the worst computer virus in the world may be its replicability. Stuxnet’s code was leaked online in 2012, allowing cybercriminals and state actors alike to study its techniques. This led to the rise of copycat malware, including Duqu and Flame, which borrowed Stuxnet’s stealth and persistence. Meanwhile, ransomware-as-a-service (RaaS) models have democratized cyber extortion, enabling even low-skilled attackers to deploy what is the worst computer virus in the world with minimal effort. The shift from nation-state sabotage to globalized crime means the answer to what is the worst computer virus in the world is no longer static—it’s a moving target, shaped by both geopolitical tensions and the dark economy of cybercrime.
Case Study: A Closer Look
No single attack encapsulates the dual threat of what is the worst computer virus in the world better than NotPetya in 2017. Disguised as ransomware, NotPetya was actually a wiper malware—a destructive tool designed to erase data rather than extort money. Its origins trace back to EternalPetya, a variant of EternalBlue (the same flaw exploited by WannaCry), but NotPetya’s true purpose was sabotage. The attack began with a compromised Ukrainian accounting software update, then spread globally, infecting over 2,000 companies in 65 countries. Among the victims: Maersk, which suffered $300 million in losses; Merck, with $870 million in damages; and FedEx, which saw $400 million in disruptions. What is the worst computer virus in the world in this case wasn’t just its financial impact—it was its indiscriminate destruction, targeting businesses regardless of their connection to Ukraine. Security researchers later attributed NotPetya to Russian military intelligence (GRU), linking it to tensions over Crimea. Unlike Stuxnet, which had a specific target, NotPetya was designed to cause maximum chaos. Its ransom note was a fake—no decryption keys were ever provided. The attack proved that what is the worst computer virus in the world could now be both a weapon and a wildfire, spreading uncontrollably while achieving its destructive goals. The lesson for cybersecurity professionals was clear: what is the worst computer virus in the world was no longer limited to nation-state actors with deep pockets—it could emerge from opportunistic sabotage with global consequences."NotPetya wasn’t just ransomware—it was digital terrorism. It didn’t care about money; it cared about erasing data. That’s the new frontier of cyber warfare." — Johannes B. Ullrich, Dean of Research at SANS Technology Institute
| Factor | Estimated Impact |
|---|---|
| Financial Loss (Global) | $10 billion+ (industry estimates, including Maersk, Merck, FedEx) |
| Geopolitical Escalation | Confirmed as GRU operation; raised cyber warfare tensions between NATO and Russia |
| Replicability | Led to copycat wiper attacks (e.g., HermeticWiper in 2022) |
What This Means Going Forward
The evolution of what is the worst computer virus in the world reflects a fundamental shift in cyber warfare. Stuxnet proved that malware could be a precision tool; NotPetya demonstrated that it could also be a weapon of mass disruption. Today, the threat landscape is fragmented: state actors develop zero-day exploits for espionage, while cybercrime syndicates deploy ransomware-as-a-service to maximize profits. The answer to what is the worst computer virus in the world is no longer a single malware family but a convergence of tactics—where sabotage, extortion, and espionage blur into a single, adaptive threat. Governments and corporations are responding with defensive strategies that were unthinkable a decade ago. Zero-trust architecture, AI-driven threat detection, and quantum-resistant encryption are now priorities. Yet the asymmetry of cyber warfare remains: while defenders must secure every possible entry point, attackers need only one unpatched vulnerability. The question of what is the worst computer virus in the world is less about identifying a specific strain and more about preparing for the next iteration—one that could combine Stuxnet’s precision with NotPetya’s chaos, or leverage emerging technologies like AI-generated malware. The battle for cyber dominance has only just begun.
Conclusion
If what is the worst computer virus in the world must be named, Stuxnet remains the gold standard for destructive capability, while NotPetya redefined systemic risk. Yet the true danger lies in what comes next. As cyber weapons proliferate—from state-sponsored wipers to autonomous ransomware—the distinction between sabotage and crime continues to dissolve. The lesson is clear: what is the worst computer virus in the world is no longer a fixed answer but a moving target, shaped by geopolitical tensions, technological advances, and the dark economy of cybercrime. The only certainty is that the next what is the worst computer virus in the world will be more sophisticated, more adaptive, and more dangerous than its predecessors. The challenge for defenders is not just to contain the known threats but to anticipate the unknown. The era of digital Armageddon has arrived—and the only way to survive it is to study the past, prepare for the worst, and accept that the next attack may not come from where we expect.Comprehensive FAQs
Q: Can Stuxnet still infect systems today?
A: Yes, but with significant modifications. Stuxnet was designed for Windows XP and Siemens Step 7, which are now obsolete. However, researchers have recreated its functionality using modern tools, proving that its core techniques remain viable. The real risk lies in copycat malware that borrows Stuxnet’s methods—such as Trisis (2017), which targeted industrial control systems in the U.S. and Middle East.
Q: How do ransomware attacks like LockBit compare to Stuxnet in terms of damage?
A: LockBit and similar ransomware strains excel in financial impact—with what is the worst computer virus in the world in revenue terms—but Stuxnet’s damage was irreversible. Ransomware can be mitigated (via backups or payments), while Stuxnet physically destroyed machinery. The choice of what is the worst computer virus in the world depends on the metric: economic bleeding (ransomware) vs. physical sabotage (Stuxnet).
Q: Has any country successfully countered a cyber attack like Stuxnet?
A: No country has fully neutralized a Stuxnet-level attack, but defensive measures have evolved. Israel reportedly patched vulnerabilities in its own nuclear facilities after Stuxnet, while Iran developed air-gapped networks to isolate critical systems. However, NotPetya (2017) and HermeticWiper (2022) proved that no defense is foolproof—especially when attacks exploit supply-chain weaknesses (e.g., compromised software updates).
Q: What is the most likely scenario for the next "worst computer virus"?
A: The next what is the worst computer virus in the world will likely combine AI, supply-chain attacks, and quantum computing. Researchers warn of autonomous malware that self-replicates and adapts in real-time, or quantum-resistant encryption being bypassed by new attack vectors. State actors will continue developing precision wipers, while cybercrime groups will automate ransomware using machine learning to maximize extortion. The biggest risk? A hybrid attack—where sabotage and crime merge under a single malicious campaign.
Q: Are there any industries more vulnerable to cyber attacks than others?
A: Critical infrastructure (energy, healthcare, finance) remains the top target, but supply chains are now the weakest link. The 2021 Colonial Pipeline attack (DarkSide ransomware) showed how disrupting a single pipeline could paralyze a nation’s fuel supply. Meanwhile, manufacturing (e.g., Stuxnet’s impact on centrifuges) and government agencies (e.g., NotPetya’s effect on Ukrainian systems) are high-value targets for both state actors and criminals. The most vulnerable? Organizations that rely on legacy systems (e.g., unpatched Windows XP machines) or third-party vendors with poor cybersecurity.
