
Common Myths About Cloud App Security APIs
The assumption that cloud app security APIs are inherently more secure than on-premises systems persists, despite evidence to the contrary. Cloud providers offer robust infrastructure, but security hinges on how APIs are implemented. Many teams assume built-in protections suffice, only to discover gaps when under attack. Another myth is that API security frameworks like OAuth 2.0 or OpenID Connect are foolproof. While these standards reduce risks, they’re often misconfigured or combined with weak secrets. A 2022 study found that 70% of API-related breaches involved flawed authentication flows—proving that standards alone don’t guarantee safety.Myth 1: Encryption Alone Secures APIs
Organizations frequently believe that TLS encryption renders cloud app security API traffic unassailable. While TLS prevents eavesdropping, it doesn’t protect against injection attacks, broken authentication, or misconfigured endpoints. A poorly designed API can leak data even with encryption in place. The reality is that encryption is a baseline, not a finish line. APIs must also enforce strict input validation, rate-limiting, and least-privilege access. Without these, encryption becomes a false sense of security—like locking a door while leaving the window open.Myth 2: Zero Trust Is Only for Enterprises
Many SMEs dismiss cloud app security API zero-trust models as overkill, assuming their scale makes them immune to targeted attacks. Yet small businesses are prime targets because they often lack layered defenses. A single compromised API can expose entire customer databases. Zero trust isn’t about budget—it’s about verifying every request, regardless of source. Even modest deployments, like API gateways with strict identity checks, can drastically reduce risk. The barrier isn’t complexity; it’s mindset.Myth 3: Compliance Equals Security
Meeting GDPR, HIPAA, or SOC 2 requirements doesn’t mean an API is secure. Compliance frameworks set minimum standards, but attackers exploit gaps between policies and execution. A cloud app security API might pass audits while still leaking data through unmonitored endpoints. True security requires continuous testing—penetration scans, runtime analysis, and anomaly detection. Compliance is a checkpoint; security is an ongoing process.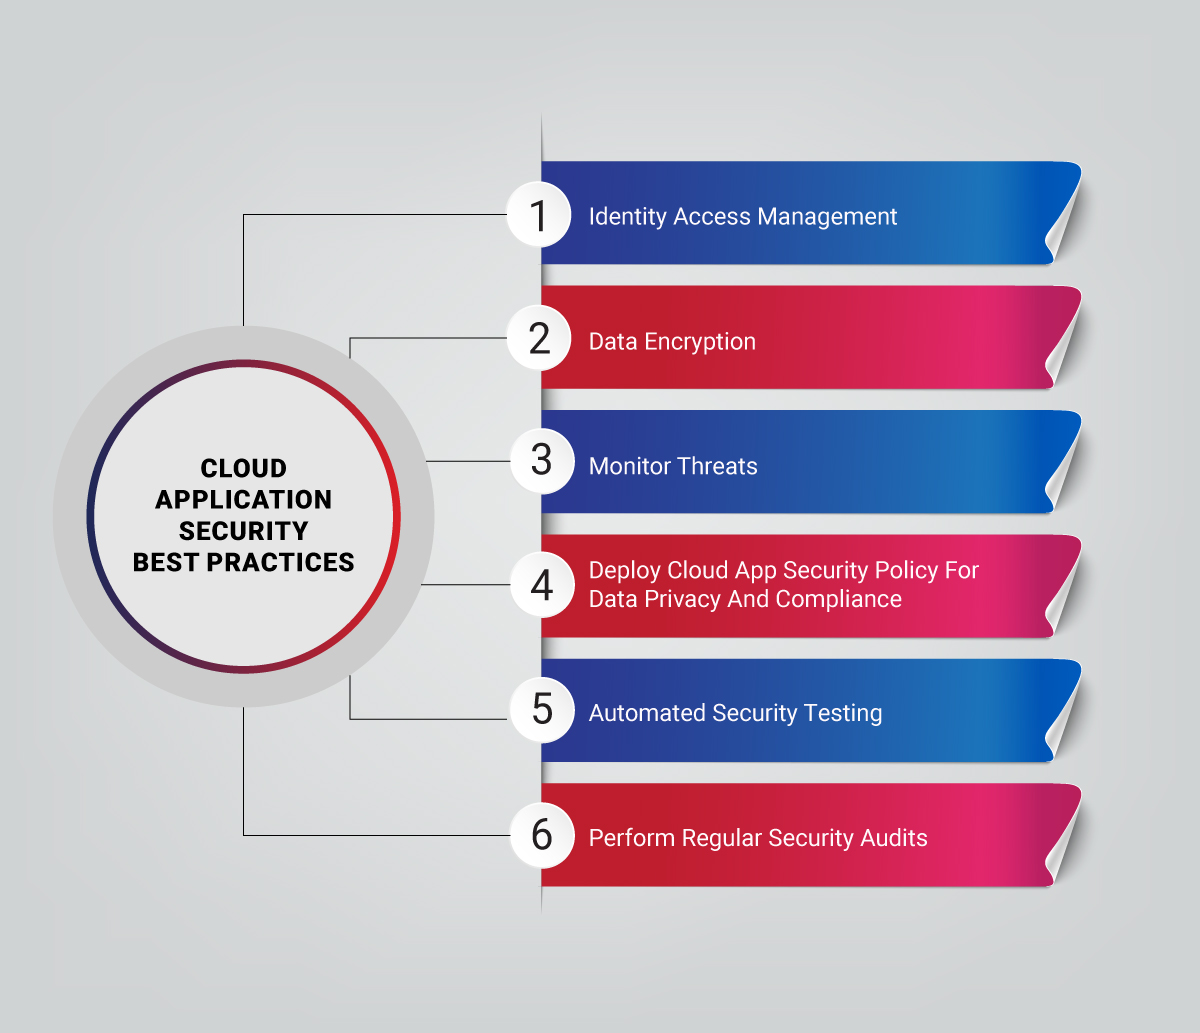
What Holds Up to Scrutiny
At its core, cloud app security API resilience depends on three verified principles: 1. Defense in depth: No single layer should be the sole protector. Combine API gateways, WAFs, and runtime monitoring. 2. Least privilege: APIs should request only the minimum permissions needed, not broad access. 3. Observability: Logs and alerts must track every API call, not just failures. These aren’t theoretical—they’re battle-tested. Organizations using these principles report fewer breaches, even when targeted. The key is implementation discipline, not just tooling.“API security isn’t about perfect tools—it’s about perfect processes. A misconfigured API with a $100,000 firewall is still vulnerable.” — Security architect at a Fortune 500 firm
| Common Belief | What the Evidence Says |
|---|---|
| APIs are secure if they’re behind a firewall. | Firewalls block network attacks, but APIs can still be exploited via logic flaws or misconfigurations. |
| Open-source APIs are inherently risky. | Risk depends on maintenance, not origin. Poorly managed proprietary APIs can be just as vulnerable. |
| API keys are sufficient for authentication. | Keys are easily stolen or leaked. Multi-factor authentication and short-lived tokens reduce exposure. |
Why the Confusion Persists
The gap between theory and practice stems from two factors. First, cloud app security API ecosystems evolve faster than security teams can adapt. New protocols emerge, old ones become obsolete, and misconfigurations multiply. Second, vendors often oversell solutions, framing tools as silver bullets rather than components of a larger strategy. Add to this the skills gap: developers prioritize speed over security, while security teams lack API-specific expertise. The result is a fragmented approach where risks accumulate silently—until they don’t.
Conclusion
Cloud app security APIs are neither inherently secure nor hopelessly flawed—they’re what you make them. The difference between a breach and a breach avoided often comes down to basic hygiene: validating inputs, monitoring traffic, and treating APIs as attack surfaces, not afterthoughts. The good news? The tools exist. The challenge is cultural—shifting from reactive fixes to proactive design. Organizations that treat cloud app security APIs as a continuous process, not a checkbox, will outlast those who don’t.Comprehensive FAQs
Q: How do API keys differ from OAuth tokens in security?
API keys are static and long-lived, making them prime targets for theft. OAuth tokens are short-lived, scoped, and tied to user sessions—significantly harder to exploit. Keys are better for machine-to-machine auth; tokens for user flows.
Q: Can a WAF protect against API-specific attacks?
WAFs help block common threats like SQL injection, but they’re not API-aware by default. Dedicated API security gateways (e.g., Kong, Apigee) offer deeper inspection of request/response patterns, including schema validation and rate-limiting.
Q: What’s the most critical misconfiguration in APIs?
Excessive permissions. APIs granted admin-level access by default create blast radii. Enforcing least privilege—limiting actions to only what’s necessary—reduces attack surfaces dramatically.
Q: Do cloud providers secure APIs for their customers?
Providers secure the infrastructure (e.g., network, storage), but cloud app security API responsibility lies with the customer. Shared models mean customers must configure authentication, encryption, and access controls themselves.
Q: How often should APIs be audited for security?
At minimum, quarterly for critical APIs and annually for low-risk ones. Continuous monitoring (via tools like Twistlock or Prisma Cloud) is ideal, as misconfigurations can appear between audits.
Q: Are there open-source tools for API security?
Yes, but with caveats. Tools like OWASP API Security Top 10 provide guidelines, while Argo Security and Kratos offer open-core solutions. However, open-source lacks vendor support—critical for incident response.
Q: What’s the biggest API security trend in 2024?
Shift-left security—baking API protections into the development pipeline (e.g., static analysis for vulnerabilities, automated policy enforcement). DevSecOps is no longer optional; it’s a necessity.
Q: Can a breach be traced back to a specific API?
Yes, but it requires observability. Tools like Datadog API Monitoring or AWS API Gateway Logs track requests, while SIEMs (e.g., Splunk) correlate API activity with breaches. Without logs, attribution is guesswork.
