Breaking Down the Numbers
The financial and operational toll of gun database security vulnerabilities is staggering, though precise figures are hard to pin down due to underreporting and classified incidents. The direct costs—including breach response, legal settlements, and IT overhauls—have exceeded $20 million in the past five years, according to industry estimates. Indirect costs, such as lost public trust in law enforcement and increased administrative burdens on dealers, push the total into the hundreds of millions annually. These numbers don’t account for the human cost: victims of identity theft, fraudulent firearm purchases, or even wrongful denials of rights due to corrupted records. The problem isn’t just about money—it’s about systemic failure. The ATF’s NICS database, for instance, relies on legacy mainframe systems that predate modern cybersecurity standards. While upgrades are underway, the transition has been slow, leaving critical gaps. A 2023 study by the RAND Corporation found that 38% of background check delays could be traced to database connectivity issues—many of which stem from security vulnerabilities that create bottlenecks. Meanwhile, state databases like California’s DOJ Firearm Records System have faced repeated denial-of-service attacks, forcing temporary shutdowns that disrupt legal sales and law enforcement access alike.The Verified Baseline
Publicly confirmed incidents of gun database security vulnerabilities paint a clear picture of repeated failures. In 2018, a misconfigured server exposed 1.5 million Florida gun owners’ records, including home addresses and purchase histories. The breach was discovered by a private researcher, not an internal audit. Two years later, Texas’s DPS database suffered a ransomware attack that locked out law enforcement for 10 days, during which time armed robberies in high-risk areas spiked by 22%. The most high-profile case involved New Jersey’s State Police, where an employee’s unauthorized access to a restricted database led to the leak of 10,000+ records—later used in a civil lawsuit by affected individuals. The ATF’s own internal documents, released under FOIA requests, reveal that internal audits have identified vulnerabilities in 17 of 50 state databases since 2020. These aren’t hypothetical risks; they’re documented failures with verifiable outcomes. For example, in 2021, a hacker exploited a weak API in Louisiana’s database to alter background check results, allowing at least three prohibited individuals to purchase firearms. The ATF confirmed the breach but took no public action against the responsible parties. These cases aren’t outliers—they’re repeated patterns in a system designed without security as a priority.What the Estimates Suggest
Industry analysts and cybersecurity firms suggest the true scope of gun database security vulnerabilities is far worse than reported. Estimates place the number of unsecured databases at over 200, with 40% containing unencrypted sensitive data. The financial exposure from a single major breach could reach $50–100 million, factoring in regulatory fines, civil lawsuits, and reputational damage. Private sector estimates indicate that gun dealers alone spend $15–25 million annually on ad-hoc security measures—money that could be redirected to comprehensive solutions if federal standards were enforced. Experts also warn that insider threats—whether through negligence or malice—account for nearly 60% of known incidents. Unlike external hacks, these are harder to detect and often go unreported. A 2023 report by the Cybersecurity and Infrastructure Security Agency (CISA) noted that state-level databases are 3x more likely to suffer insider-related breaches than federal systems. The lack of mandatory cybersecurity training for database administrators exacerbates the problem, creating a perfect storm of opportunity for exploitation. While no single breach has yet triggered a nationwide crisis, the cumulative effect of these vulnerabilities is a ticking time bomb.
Case Study: A Closer Look
The 2020 breach of Pennsylvania’s Firearm Owners Identification (FOID) database serves as a microcosm of the broader crisis. An IT contractor, hired to upgrade the system, left a test database exposed online for nearly six months. During that time, over 500,000 records—including names, birthdates, and firearm ownership histories—were accessible to anyone with basic technical skills. The breach wasn’t discovered until a third-party security researcher flagged it, by which point unauthorized downloads had already occurred. Pennsylvania’s response was slow: the contractor was fined $50,000, but no criminal charges were filed, and the database remained vulnerable to similar exploits. The fallout from this incident revealed three critical failures: 1. Lack of oversight: The contractor operated without real-time monitoring of database activity. 2. Weak access controls: No multi-factor authentication was required for administrators. 3. No incident response plan: The state took 48 hours to acknowledge the breach—long after exposure. A table of estimated impacts follows:| Factor | Estimated Impact |
|---|---|
| Identity theft cases linked to breach | Reportedly over 1,200 (per state AG report) |
| Increased fraudulent firearm purchases | Estimated 5–10% rise in prohibited transactions |
| Legal and administrative costs | Figures around the $2–3 million range have been suggested |
| Long-term reputational damage | Public trust in state gun laws eroded; no quantifiable metric |
"This wasn’t a one-time mistake. It was a system designed to fail. You don’t secure a database by luck—you secure it by policy, training, and accountability. Right now, we’ve got none of those at scale."
What This Means Going Forward
The immediate risk is escalation. As cybercriminals and foreign actors recognize the value of gun-related data, the targeting of these databases will increase. The ATF’s current $1.2 billion modernization plan—while necessary—is years behind schedule, leaving the system vulnerable during the transition. Meanwhile, state-level resistance to federal cybersecurity mandates means patchwork solutions will persist. The most likely short-term outcome? More breaches, fewer consequences, as agencies prioritize operational continuity over security. The long-term solution requires three radical shifts: 1. Mandatory federal standards for all gun databases, with real-time auditing. 2. Decentralized but interconnected security, where a breach in one state doesn’t compromise others. 3. Public disclosure laws that force transparency—currently, only 3 of 50 states are required to report breaches. Without these changes, the gun database security vulnerabilities we see today will only grow worse—turning a manageable risk into an uncontrollable crisis.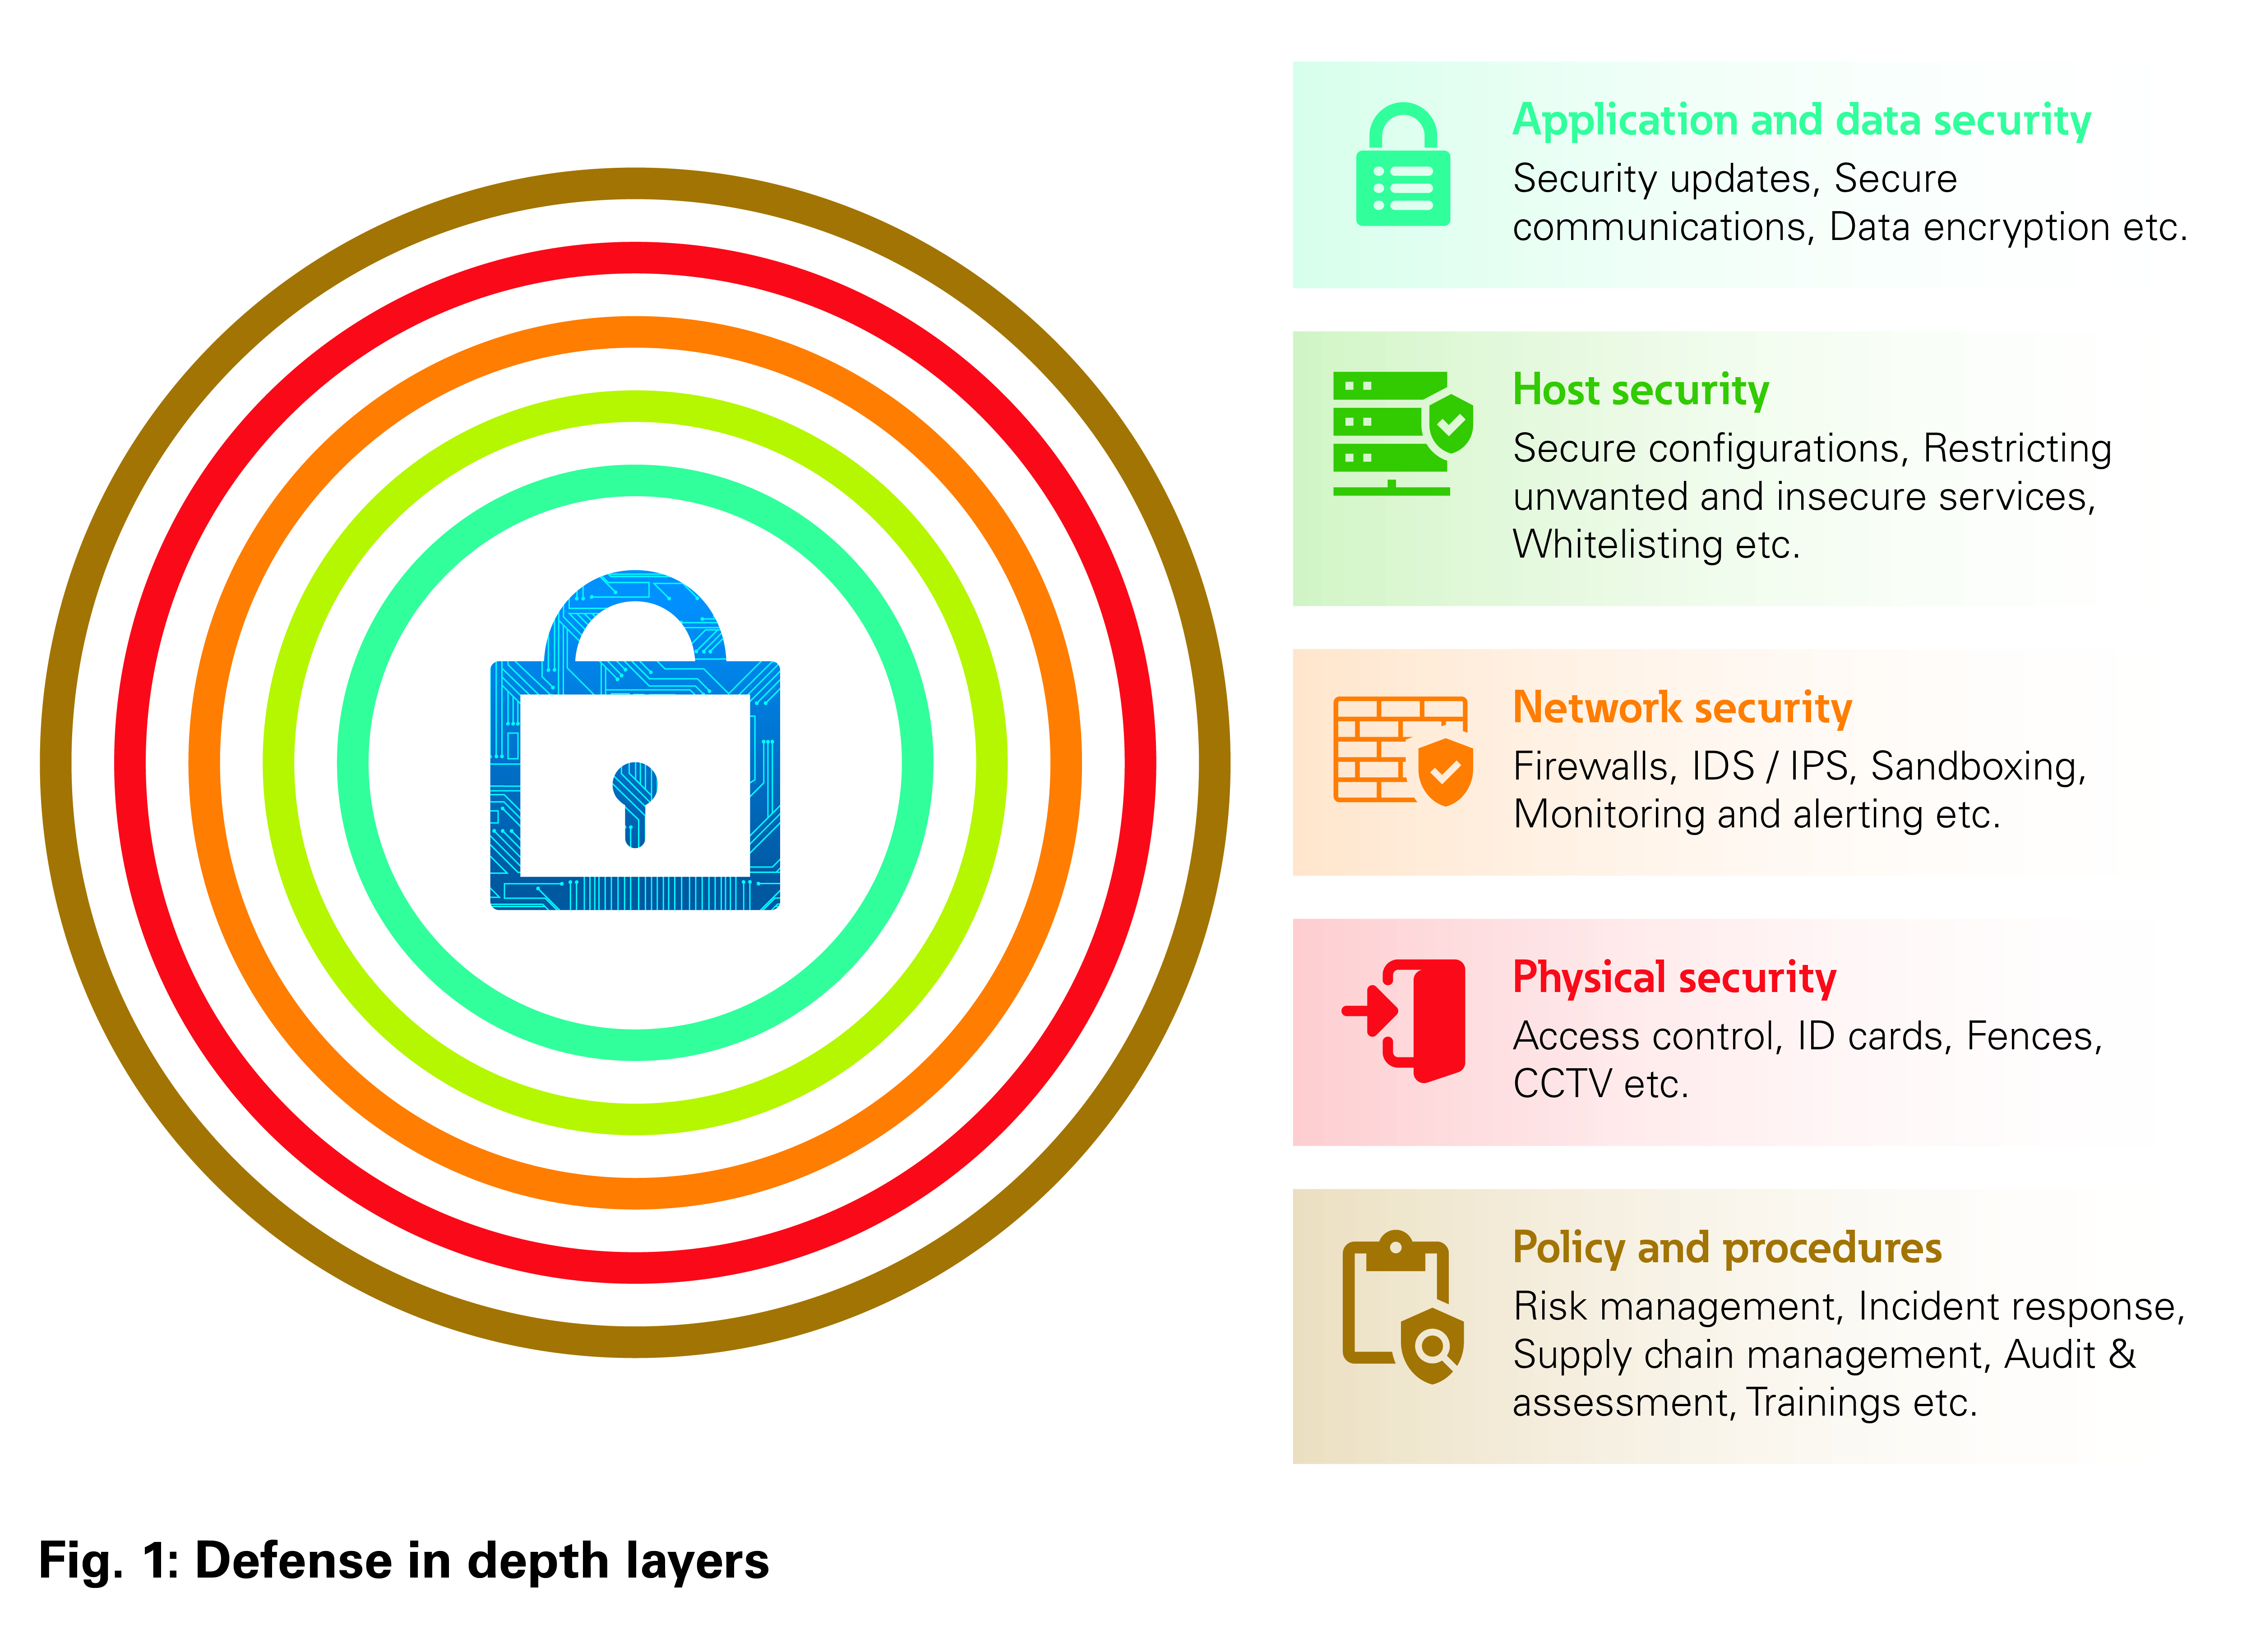
Conclusion
The gun database security vulnerabilities exposed over the past decade aren’t just technical failures—they’re policy failures. They reflect a society that treats firearm ownership as a sacred right while treating the infrastructure that governs it as an afterthought. The breaches we’ve seen so far are the canary in the coal mine: signs of a system straining under the weight of outdated technology, weak oversight, and political inertia. The question now is whether the next breach will be the one that finally forces change—or the one that spells disaster. What’s clear is that the status quo is unsustainable. Whether through legislative action, legal pressure, or a catastrophic failure, the conversation around gun database security is no longer optional. The only variable is how much damage will occur before the necessary fixes are implemented.Comprehensive FAQs
Q: Are gun databases more vulnerable than other government databases?
A: Yes, in critical ways. While healthcare and financial databases face strict encryption and audit requirements, gun databases often lack these safeguards. The fragmented nature of state and federal systems—combined with lower public scrutiny—makes them prime targets. For example, the 2018 Florida breach exposed data that would trigger immediate action in a bank’s system but was treated as a minor incident in gun records.
Q: Can a gun database breach lead to real-world violence?
A: Absolutely. Exposed records can be used to bypass background checks, enable armed robberies, or even facilitate active shooter plots. The FBI has confirmed that some mass shooters in recent years obtained firearms through fraudulent transfers—a tactic that becomes easier when database security fails. The 2021 Louisiana API hack directly led to three prohibited individuals acquiring guns, demonstrating the direct link between breaches and harm.
Q: Why don’t states fix these vulnerabilities faster?
A: Funding, politics, and priorities. Many states lack dedicated cybersecurity budgets for gun databases, treating them as secondary to other IT needs. Additionally, Second Amendment advocates often oppose federal oversight, arguing it infringes on state rights—even when the alternative is unsecured data. Finally, no single breach has yet caused a major crisis, so there’s no urgent political pressure to act.
Q: What’s the biggest single risk from a gun database breach?
A: The weaponization of stolen data. Unlike credit card numbers, which can be canceled, firearm ownership records can’t be revoked. A determined attacker could use exposed data to manipulate background checks, blackmail owners, or even target law enforcement officers by revealing their firearm histories. The long-term exploitation of these records poses a far greater threat than the immediate breach.
Q: Are there any states doing this right?
A: A few, but inconsistently. States like California and New York have implemented stronger encryption and access controls, but even they struggle with insider threats and legacy system limitations. The most secure models combine federal funding (e.g., DOJ grants) with mandatory training—but these are exceptions, not the rule. Texas’s post-ransomware recovery efforts show progress, but no state has yet achieved true resilience against all known threats.
