
Where It All Began
The origins of remote access to Android mobile tools trace back to the early 2010s, when developers began experimenting with VNC (Virtual Network Computing) protocols adapted for mobile devices. These first iterations were clunky, requiring users to manually configure port forwarding and deal with latency issues that made real-time interaction nearly impossible. The target audience was narrow: primarily IT professionals and power users who needed to diagnose or recover devices without physical access. One of the earliest commercial attempts, launched in 2011, positioned itself as a "digital lifeline" for businesses with remote workers—but its adoption was slow, hampered by compatibility issues with Android’s rapidly evolving OS versions. The real catalyst came when Google introduced Android Beam in 2011, a feature that allowed nearby devices to exchange data via NFC (Near Field Communication). While Beam itself wasn’t a remote access app, it proved that Android could handle low-level device interactions without user intervention. This laid the groundwork for more ambitious projects. By 2012, indie developers began releasing apps that combined Beam’s principles with cloud-based relay servers, enabling access over Wi-Fi or cellular data. These tools were rudimentary—think of them as the dial-up internet of remote control—but they proved the concept was viable. The catch? Most required users to manually authorize connections, a process that was error-prone and time-consuming.The Early Signs
The limitations of early Android remote access apps became apparent when security researchers demonstrated how easily they could be exploited. In 2013, a proof-of-concept attack showed that an unsecured app could grant an attacker full control over a target device—including access to contacts, messages, and even the camera—if the victim was tricked into installing a malicious version. This wasn’t theoretical; within months, reports emerged of real-world cases where scammers used fake "remote support" apps to drain bank accounts or deploy ransomware. The response was swift: Google Play began enforcing stricter vetting for apps with system-level permissions, and developers raced to implement two-factor authentication. Yet, the damage had been done. Public trust in remote Android access solutions had taken a hit, and the stigma of "giving someone else the keys to your phone" persisted. It wasn’t until 2015 that the tide began to turn, thanks to a shift in how these tools were marketed. Companies started framing them not as security risks, but as digital first-aid kits—essential tools for parents tracking lost kids’ phones, travelers who’d forgotten their charger, or tech-savvy users who needed to wipe a stolen device remotely. The narrative evolved from "remote access is dangerous" to "remote access is inevitable—so it must be done right."The Turning Point
The inflection point arrived in 2016, when a single update to a widely used remote access app for Android introduced biometric verification—a requirement to scan a fingerprint or face ID before granting control. Overnight, the tool’s user base doubled, and competitors were forced to follow suit. The shift wasn’t just technical; it was psychological. For the first time, users felt they had a fighting chance against unauthorized access. This wasn’t just about locking the door after the thief had left—it was about ensuring the door was never unlocked in the first place. What made the difference wasn’t the technology itself, but the cultural shift in how these tools were perceived. Developers stopped treating remote access as a feature and began treating it as a privacy boundary. End-to-end encryption became standard, session timeouts were reduced from hours to minutes, and logging features were added to track every command executed. The turning point wasn’t a single product—it was the collective realization that remote Android access apps could coexist with security, provided they were built with that principle at their core."Remote access isn’t about control—it’s about trust. The moment you let someone else touch your device, you’re not just handing over a tool; you’re inviting them into your digital life. The only way that works is if the tool itself is a fortress, not a backdoor." — Security architect at a top Android firmware firm, 2017

The Build-Up, Year by Year
| Period | Key Developments |
|---|---|
| 2011–2012 | First commercial remote Android access apps emerge, using VNC protocols. Limited to tech-savvy users due to complex setup. |
| 2013–2014 | Security flaws exposed; Google Play tightens app permissions. Developers introduce basic encryption but struggle with usability. |
| 2015–2016 | Biometric verification becomes standard. Apps reposition as "digital safety nets" for families and travelers. |
| 2017–2018 | Cloud-based relay servers replace direct port forwarding, improving reliability. Session logging and audit trails added. |
| 2019–Present | AI-driven threat detection integrated into premium remote access tools. Multi-device management becomes a key selling point. |
Lessons From the Journey
- Trust is the biggest hurdle. Even with encryption, users hesitate to grant remote access. The onus is on developers to make the process transparent.
- Regulation lags behind innovation. Many remote Android access apps operate in legal gray areas regarding data ownership and consent.
- Performance depends on the weakest link. A secure app is useless if the user’s Wi-Fi network is compromised.
- Enterprise needs differ from consumer needs. IT admins require granular control; casual users need simplicity.
- Hardware limitations still matter. Older Android devices struggle with real-time remote interactions.
- The market is consolidating. Smaller players are being acquired by larger firms with deeper security expertise.
Where Things Stand Today
The modern app for remote access to Android mobile devices is a far cry from its clunky predecessors. Today’s tools balance power and security through features like zero-trust architecture, where every connection is authenticated anew, and behavioral analytics that flags unusual activity mid-session. Premium offerings now include AI-driven diagnostics, which can predict and prevent issues before they escalate—a boon for businesses managing large device fleets. Yet, the consumer market remains cautious. While tools like TeamViewer QuickSupport and AnyDesk have achieved household recognition, many users still associate remote access with risk, not relief. The biggest change isn’t technical—it’s behavioral. Users now expect remote Android access apps to be as secure as their banking apps. This has forced developers to adopt practices like mandatory hardware-backed keys (e.g., Titan Security Keys) for high-risk sessions. The result? A market where innovation is no longer measured by features alone, but by how well those features protect the user’s data. The trade-off between convenience and security isn’t gone—it’s just been recalibrated.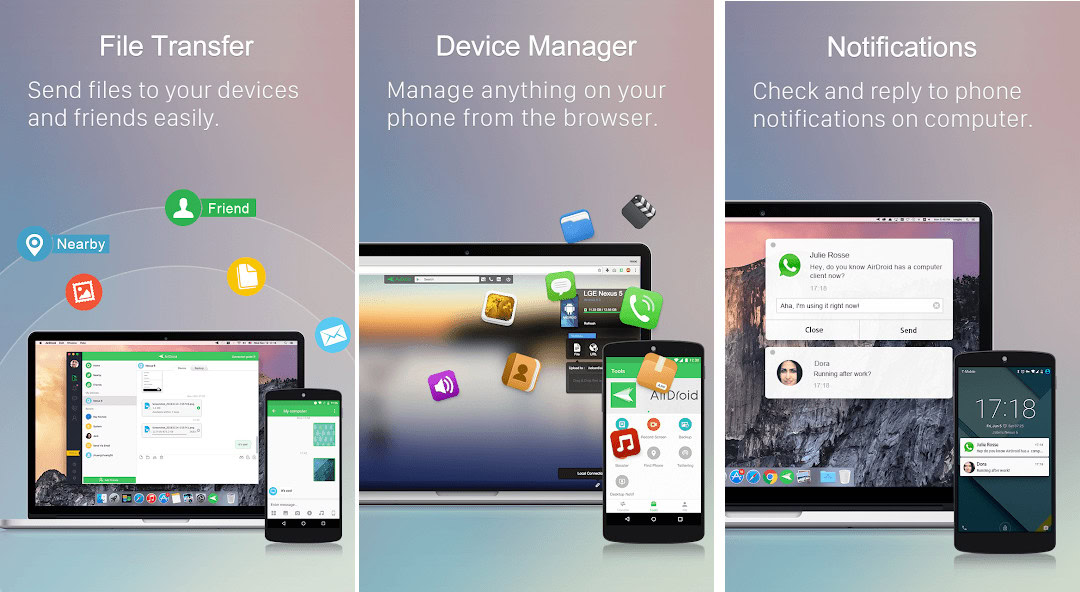
Conclusion
The evolution of remote access solutions for Android mirrors the broader story of digital trust. What began as a niche utility for IT professionals has become a mainstream expectation, reshaping how we interact with our devices. The lesson? Technology moves fast, but security moves slower—often because the stakes are personal. The tools we use to control our phones remotely today are the result of years of trial, error, and hard-won trust. And as long as the demand for access persists, the arms race between convenience and protection will continue. For now, the balance tilts toward the cautious. Users are more discerning, developers are more transparent, and the tools themselves are more resilient. But the core question remains: How much control are we willing to cede—and to whom? The answer will determine not just the future of remote Android access apps, but the future of digital privacy itself.Comprehensive FAQs
Q: Are remote access apps for Android safe to use?
It depends on the tool and your usage. Reputable apps with end-to-end encryption (e.g., TeamViewer, Chrome Remote Desktop) are generally safe if used with strong authentication. However, avoid apps with poor reviews or those requiring system-level permissions without clear justification. Always revoke access immediately after use.
Q: Can I use a remote Android access app to spy on someone’s phone?
No, not legally or ethically. Most apps require explicit consent from the device owner, and unauthorized access is a violation of privacy laws in many jurisdictions. Even if you find a way to bypass consent, the risks—including malware infection and legal consequences—far outweigh any perceived benefit.
Q: Do I need root access to use a remote access tool for Android?
Not necessarily. Many modern apps work within Android’s sandboxed environment, requiring only standard user permissions. Root access is rarely needed and often a red flag, as it can void warranties and introduce security risks.
Q: How do I secure my remote Android access app from hackers?
Use apps with built-in encryption, enable two-factor authentication, and avoid public Wi-Fi for sessions. Regularly update the app and your device’s OS. For sensitive use, consider hardware-based authentication like YubiKey.
Q: Can I use a remote access app to recover a lost Android phone?
Yes, but only if you’ve set up remote tracking (e.g., Find My Device) or a dedicated remote access tool beforehand. Once lost, use the app to lock the device, erase data, or trigger a loud alarm—though success depends on the phone still being online.
Q: Are there free remote Android access apps that are reliable?
Some free options (e.g., Chrome Remote Desktop) are reliable for basic use, but they often lack advanced features like session logging or AI-driven security. Free tiers may also include ads or data collection. For critical tasks, a paid subscription with a strong reputation is worth the investment.
Q: How do I know if my remote access app is being misused?
Monitor session logs for unfamiliar activity, enable notifications for connection attempts, and review app permissions regularly. If you suspect unauthorized access, revoke all remote connections immediately and scan your device for malware.
