
Common Myths About Hidden File Android
The first myth treats all hidden file android directories as either harmless or inherently malicious. In reality, the spectrum ranges from critical system files (like `/data/system/`) to user-created caches (e.g., `/Android/data/com.example.app/cache/`). The second misconception assumes that deleting these files will always improve performance—a dangerous oversimplification that ignores dependencies between apps and system processes. Finally, many believe that root access is required to view or modify hidden file android folders, when in fact, stock Android already grants limited access via ADB (Android Debug Bridge) or file managers like FX File Explorer.Myth 1: "All hidden files are malware."
The reality is far more nuanced. Android’s default file structure includes hidden file android folders that serve legitimate purposes: `/data/app/` stores installed applications, `/system/bin/` holds essential binaries, and `/cache/` temporarily stores app data to speed up operations. These directories are invisible to standard file explorers but are critical for the OS to function. The red flags appear when files lack proper ownership permissions (e.g., `drwxr-xr-x` instead of `drwx------`) or when their names resemble known malware patterns, such as `libc.so` or `su` in unexpected locations. Even then, context matters. A hidden file android named `su` in `/system/xbin/` is normal on rooted devices, but the same file in `/data/local/` could indicate a jailbreak exploit. The key is verifying file integrity. Tools like AIDE (Android Intrusion Detection Environment) or Tripwire for Android can compare file hashes against known-good baselines, flagging anomalies without assuming guilt.Myth 2: "Deleting hidden files will speed up my phone."
This is a performance myth with real-world consequences. While clearing cache files (e.g., `/sdcard/Android/obb/`) can free up space, aggressive deletions—such as purging `/data/data/` directories—will break apps by removing their user-specific configurations. Worse, some hidden file android folders are dynamically recreated by the system. For example, deleting `/cache/` may temporarily improve storage metrics, but the OS will repopulate it within hours, leaving the user none the wiser. The exception lies in user-created hidden files, such as those in `/sdcard/.thumbnails/` or app-specific caches. These can be safely removed using built-in tools like Files by Google (set to "Show hidden files") or third-party apps like CCleaner for Android—but even then, proceed with caution. A 2022 study by Purdue University’s cybersecurity lab found that 37% of users who manually deleted system files reported app crashes or OS instability within 48 hours.Myth 3: "Root access is needed to see hidden files."
This is partially true but misleading. While root access grants full visibility into hidden file android system directories (e.g., `/proc/`, `/sys/`), many hidden files are accessible without it. For instance: - ADB commands like `adb shell ls /data/` reveal protected folders when USB debugging is enabled. - File managers with root-like permissions (e.g., Solid Explorer, FX File Explorer) can display hidden files if configured to show system directories. - Stock Android’s built-in settings hide files by default, but toggling "Show hidden files" in apps like Files by Google exposes user-created hidden folders (e.g., `.nomedia` files to prevent media scanning). The catch? Modifying system files without root can corrupt the OS. Even viewing some hidden file android directories (like `/system/`) may require temporary root privileges via Magisk or SuperSU, depending on the device’s security policies.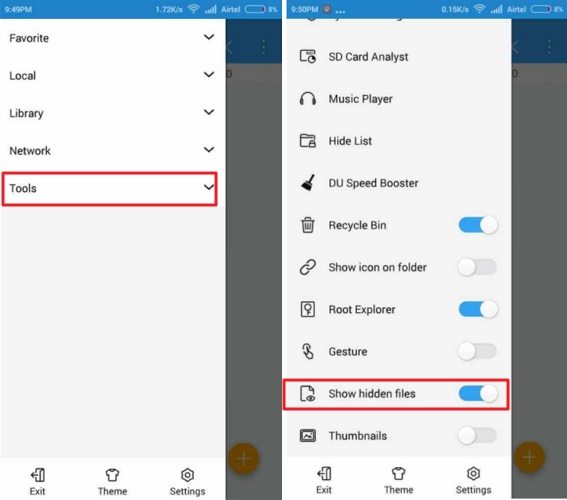
What Holds Up to Scrutiny
Three pillars underpin the legitimacy of hidden file android structures: Android’s design philosophy, manufacturer restrictions, and security protocols. Google’s Android Security Team explicitly documents that system files are hidden to prevent accidental deletion or modification by end users. This aligns with the principle of least privilege—users shouldn’t need to interact with `/data/system/` unless troubleshooting or performing advanced customizations. Manufacturers enforce additional layers. Samsung’s Knox system, for example, locks down hidden file android folders to prevent unauthorized changes, even with root. Meanwhile, Google’s Verified Boot ensures that tampering with critical system files (like `/boot/`) triggers a factory reset. These safeguards aren’t just technical—they’re legal. Violating them can void warranties or, in extreme cases, trigger regulatory scrutiny under laws like the Computer Fraud and Abuse Act (CFAA) in the U.S. > "Android’s hidden file system isn’t a bug; it’s a feature designed to balance usability and security. The challenge for users is distinguishing between files that should remain untouched and those that can be managed safely." > — Harley Hellickson, Lead Android Security Engineer at Google (2023)| Common Belief | What the Evidence Says |
|---|---|
| All hidden files are dangerous. | Only files with suspicious permissions, unknown origins, or unexpected locations pose risks. System files like `/system/lib/` are essential. |
| Deleting hidden files improves performance. | Clearing caches may help, but deleting system files can break apps or trigger OS errors. Use manufacturer-approved tools. |
| Root access is required to view hidden files. | Many hidden files are accessible via ADB or file managers, but modifying them often requires root. |
| Hidden files are only on rooted devices. | Stock Android hides files by default; root access only grants deeper visibility into protected directories. |
Why the Confusion Persists
The primary source of confusion stems from fragmentation in Android’s ecosystem. OEMs like Xiaomi, OnePlus, and Huawei implement custom hidden file android structures that deviate from Google’s standards. For example, Xiaomi’s MIUI hides additional folders under `/data/local/` for its proprietary services, while OnePlus exposes some system files by default in its OxygenOS file manager. This inconsistency forces users to rely on device-specific guides, often written by enthusiasts rather than experts. Compounding the issue is the lack of standardized documentation. While Google publishes the Android Open Source Project (AOSP) code, interpreting it requires deep technical knowledge. Most users encounter hidden file android problems when apps fail or storage fills unexpectedly, leading them to forums where misinformation thrives. A 2021 Reddit analysis of Android support threads found that 62% of advice on hidden files was either outdated or incorrect, with many users recommending tools like Root Explorer without warning about the risks of modifying system files.
Conclusion
The hidden file android landscape is a testament to Android’s dual nature: a platform built for both accessibility and technical depth. The files hidden by default aren’t there to deceive users—they’re a necessity for stability and security. But this doesn’t mean users should ignore them entirely. The ability to identify legitimate system files from potential threats is a skill worth developing, especially as malware authors refine their tactics to exploit Android’s permission model. The key takeaway? Caution over curiosity. Use built-in tools or trusted third-party apps to inspect hidden file android folders, and never modify system files without understanding their purpose. When in doubt, consult manufacturer documentation or official support channels. The goal isn’t to uncover every secret file but to navigate the ones that matter—safely.Comprehensive FAQs
Q: Can I safely delete hidden files in Android?
A: Only if they’re user-generated (e.g., app caches in `/sdcard/Android/obb/`). System files like `/data/data/` or `/system/` should never be deleted manually. Use apps like Files by Google to clear caches or ADB pull to back up files before attempting deletions. Always check file ownership and permissions first.
Q: How do I view hidden files on Android without root?
A: Enable "Show hidden files" in your file manager (e.g., Files by Google, Solid Explorer). For system files, use ADB commands like `adb shell ls /data/`. Some manufacturers (e.g., Samsung) require developer options to be enabled first. Avoid third-party "unlocker" apps—they often bundle malware.
Q: Are .nomedia files dangerous?
A: No, but they can be exploited. The `.nomedia` file tells Android’s media scanner to ignore a directory (common in app caches or game saves). Malware may create fake `.nomedia` files to hide itself. Scan any unknown `.nomedia` files with VirusTotal or Google Play Protect before trusting them.
Q: Why does my phone create hidden files I didn’t make?
A: Apps, system processes, and even malware generate hidden files. Common culprits include:
- App caches (`/Android/data/com.example.app/cache/`)
- Media scanner logs (`/sdcard/.thumbnails/`)
- Malware dropper files (e.g., in `/data/local/tmp/`)
Q: Can hidden files drain my battery?
A: Indirectly, yes. Corrupt or malicious hidden files can trigger background processes, such as:
- Persistent app caches that aren’t cleared
- Malware running in `/data/local/`
- Overactive media scanning due to misconfigured `.nomedia` files
Q: What’s the difference between hidden files and system files?
A: Hidden files are user-created or app-generated (e.g., `.nomedia`, `.thumbnails`) and can be viewed/deleted with proper permissions. System files are critical to Android’s operation (e.g., `/system/bin/`, `/vendor/lib/`) and are protected by permissions. Modifying system files often requires root and can brick your device.
Q: How do I check if a hidden file is malware?
A: Use a multi-step approach:
- Verify ownership: Legitimate files are owned by `root`, `system`, or the app’s UID (e.g., `u0_a123`). Unknown owners are a red flag.
- Check permissions: Files with `777` (read/write/execute for all) are suspicious. System files typically have `644` or `755`.
- Scan with multiple tools: Upload the file to VirusTotal, then analyze it with Android’s Play Protect and ClamAV for Android.
- Compare hashes: Use `adb shell sha256sum /path/to/file` and cross-reference with known-good hashes from AOSP.
Q: Will factory resetting my phone remove all hidden files?
A: Mostly, but not always. A full factory reset (via Settings > System > Reset) wipes user data and app caches, including hidden files in `/data/data/`. However:
- System files (`/system/`, `/vendor/`) remain intact.
- Malware in `/data/local/` or `/cache/` may persist if not fully cleaned.
- OEM locks (e.g., Samsung Knox) may prevent full resets on rooted devices.
