Common Myths About Three-Way Calling
The feature’s dual nature—practical yet prone to abuse—has birthed persistent myths. One of the most enduring is that three-way calling is inherently insecure, a relic of analog-era vulnerabilities. Another claims that only "tech-savvy" users can exploit it, ignoring how easily scammers manipulate basic phone systems. The third, perhaps most dangerous, is that privacy protections have kept pace with its evolution.Myth 1: Three-way calling is only risky on landlines
The assumption that three-way calling is safe on smartphones or VoIP stems from a misunderstanding of how call routing works. While it’s true that modern encryption (like Signal’s end-to-end) adds layers of security, the risk isn’t just about the call itself—it’s about the metadata. Even encrypted calls can leak information through caller ID spoofing or carrier-level tracking. In 2018, a study by the Electronic Frontier Foundation found that 60% of VoIP providers failed to obscure call metadata, leaving users vulnerable to surveillance or targeted ads. The bigger issue is that three-way calling often relies on intermediary servers, which can become honeypots for hackers. For example, older PBX systems (used by small businesses) were notorious for weak authentication. A 2015 FBI alert warned that criminals exploited these systems to eavesdrop on corporate negotiations or even hijack calls to demand ransom. The myth persists because users assume encryption = safety, but the attack surface extends beyond the call’s content.Myth 2: You need technical skills to misuse it
The image of a hacker typing furiously to exploit three-way calling is a Hollywood simplification. In reality, many scams rely on social engineering. A common tactic involves tricking a victim into accepting a three-way call with an accomplice—often posing as a "technical support" agent. The accomplice then impersonates a bank or authority figure, pressuring the victim into transferring money. The FBI’s Internet Crime Complaint Center logged over 35,000 such reports in 2022, with losses estimated in the tens of millions. Even without hacking, three-way calling can be weaponized through caller ID spoofing. Tools like Google Voice or third-party apps let users fake their number, making it easy to pose as someone else during a three-way conversation. A 2020 case in Texas saw a defendant use this method to convince a business owner that his "boss" had approved a fraudulent wire transfer. The key takeaway: the barrier to misuse isn’t technical—it’s awareness.Myth 3: Encrypted apps make three-way calling safe
End-to-end encryption in apps like WhatsApp or Telegram does secure the call’s content, but three-way calling introduces variables that encryption alone can’t fix. For instance, if one participant joins via a vulnerable Wi-Fi network, their device could be compromised before the call even starts. Additionally, metadata—timestamps, duration, and participant lists—often bypass encryption. A 2021 report by Access Now highlighted how law enforcement agencies have successfully subpoenaed this data from providers, even for encrypted calls. The myth overlooks another critical factor: group call dynamics. In a three-way video call, for example, one participant might unknowingly share their screen, exposing sensitive files. Or a malicious actor could record the call using screen-capture software, regardless of encryption. The security isn’t just about the call—it’s about the ecosystem around it.What Holds Up to Scrutiny
At its core, three-way calling is a feature built on two verifiable principles: connection multiplexing (combining multiple audio streams) and session management (handling the handshake between parties). The technology has evolved from analog bridges to modern SIP-based systems, but the fundamental mechanics remain. What’s less discussed is how carriers and apps balance functionality with security. The most scrutinized aspect is caller verification. Traditional phone systems relied on manual confirmation ("Is this John Smith?"), but modern apps use digital certificates or biometric checks. For example, Apple’s FaceTime uses device-level authentication to prevent unauthorized joins. However, even these systems aren’t foolproof—social engineering can bypass them if a participant is tricked into approving an unknown device.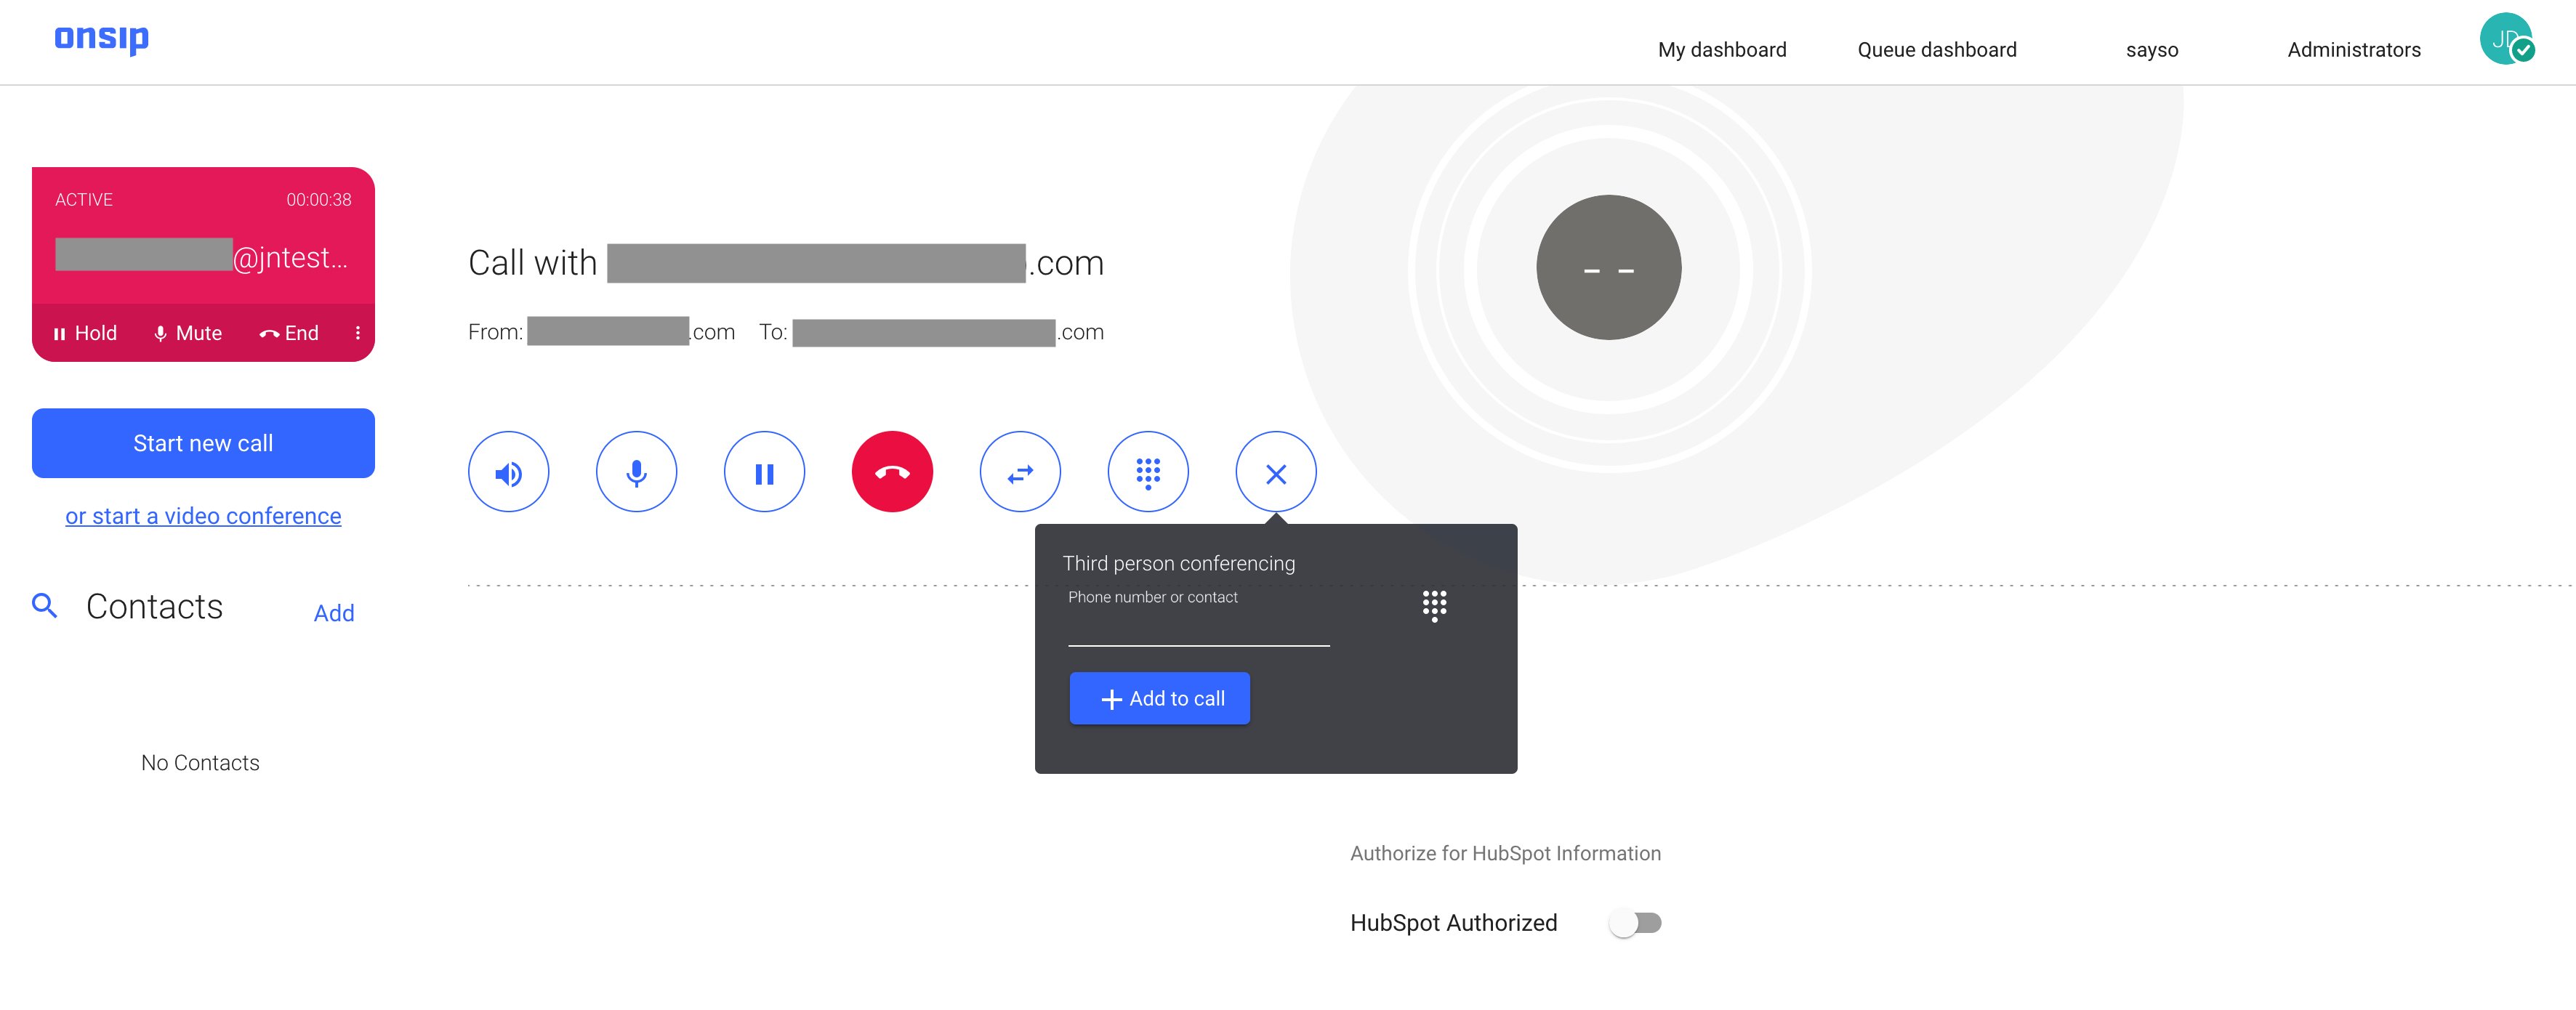
"Three-way calling is like a Swiss Army knife: useful, but only if you know how to use the blade safely. The problem isn’t the feature—it’s the assumptions people make about its limits."
— Dr. Evelyn Carter, Cybersecurity Researcher at MIT
| Common Belief | What the Evidence Says |
|---|---|
| Three-way calling is obsolete. | Usage surged 40% post-pandemic, per Ovum Telecoms reports, as remote teams adopted it for collaboration. |
| Only criminals use it for fraud. | Legitimate businesses (e.g., legal firms) use it for client consultations, but poor security practices increase risks. |
| Encryption makes it untraceable. | Metadata is often logged by carriers, and lawful interception laws (e.g., CALEA in the U.S.) require backdoor access. |
| It’s only for voice. | Modern apps support screen sharing, file transfers, and even simultaneous messaging during calls. |
| Carriers block malicious use. | Most only act after reports; proactive monitoring is rare due to cost and legal constraints. |
Why the Confusion Persists
The gap between perception and reality stems from two factors: asymmetric transparency and platform fragmentation. Carriers and app developers rarely disclose how three-way calling is implemented, leaving users to infer risks based on breaches they hear about. Meanwhile, the feature’s integration across voice, video, and messaging apps creates a moving target for security standards. Another issue is the psychology of convenience. Users prioritize ease of use over security—accepting a three-way call from an unknown number because it’s "just a quick chat." This behavior is reinforced by platforms that bury security settings in menus or use vague warnings ("This call may not be private"). The result? A culture where three-way calling is both a tool and a liability, depending on context.
Conclusion
Three-way calling’s journey—from a corporate novelty to a ubiquitous feature—mirrors broader trends in digital communication: speed over security, functionality over foresight. The technology itself isn’t the problem; it’s the lack of standardized safeguards and user education. As group calls expand into hybrid workplaces and global collaborations, the need for proactive security (not just reactive fixes) becomes clearer. The future may lie in decentralized or zero-trust models, where each participant’s device verifies others before joining. But for now, the onus is on users to treat three-way calling as what it is: a powerful tool with inherent trade-offs. The question isn’t whether it’s safe—it’s how much risk you’re willing to accept.Comprehensive FAQs
Q: Can I be recorded during a three-way call without my knowledge?
A: Legally, it depends on jurisdiction. In the U.S., one-party consent laws mean you can be recorded if any participant consents. However, technically, a malicious actor could use screen-capture software to record your side of the call even if the call itself isn’t recorded. Always assume calls can be monitored unless using end-to-end encrypted apps with verified participants.
Q: Why do some three-way calls drop or have poor audio?
A: This often happens due to network congestion or poor codec support. Traditional VoIP uses G.711 for audio, while modern apps may use Opus or SILK. If participants are on different networks (e.g., one on 4G, another on Wi-Fi), latency and packet loss can degrade quality. Business-grade SIP trunking solutions mitigate this but require proper configuration.
Q: Are there legal risks to using three-way calling for business?
A: Yes. If used to discuss non-public information (e.g., mergers, client data), leaks could violate insider trading laws or GDPR. Some industries (finance, healthcare) mandate secure call monitoring for compliance. Always check sector-specific regulations—e.g., HIPAA in the U.S. requires encrypted calls for patient discussions.
Q: Can I block three-way calls entirely?
A: On most smartphones, there’s no native setting to block three-way calls, but you can reject unknown numbers or use third-party apps like Truecaller to filter suspicious callers. For landlines, some carriers offer call screening features. The trade-off is missing legitimate calls—so weigh convenience against risk.
Q: How do scammers use three-way calling?
A: The most common tactic is "sim swap" fraud, where scammers hijack your number and initiate a three-way call with a target. They then impersonate you (e.g., "Hi Mom, it’s me—can you send money?"). Another method involves caller ID spoofing to fake a trusted contact. Always verify identities via a separate channel (e.g., text) if a three-way call seems suspicious.
Q: What’s the difference between three-way calling and conference calling?
A: Three-way calling typically involves three participants and is often handled by the phone system itself (e.g., pressing a button on a landline). Conference calling, however, can support unlimited participants and is usually managed by a PBX system or app like Zoom. The latter often includes features like muting, screen sharing, and recording—but also higher security risks if misconfigured.
Q: Are there any three-way calling apps with better security?
A: Apps like Signal, Wire, and Session offer end-to-end encryption for group calls, but security depends on how you use them. For example, Signal’s group chats are encrypted, but if you share a call link publicly, anyone with the link can join. ProtonMail’s Voice and Jitsi are also options, but always check for verified participant lists and session expiration features.
