Breaking Down the Numbers
Quantifying the impact of HTTP 429 errors is challenging because they’re rarely isolated incidents. They’re often part of a larger pattern of traffic management failures, and their effects are distributed across multiple stakeholders. What is clear, however, is that the financial and operational costs of these errors scale with the size of the platform. For a small blog, a few 429 responses might go unnoticed. For a global e-commerce giant processing thousands of transactions per second, they can translate into millions in lost revenue during high-traffic events like Black Friday or product launches. The indirect costs are harder to measure but no less significant. User churn, for instance, is a well-documented consequence of poor performance, and 429 errors—even when unintentional—contribute to that churn. Studies suggest that even a one-second delay in page load time can reduce conversions by up to 7%, and a 429 error, which often manifests as a complete failure to load, exacerbates this effect. For businesses operating on thin margins, these percentages add up quickly. Additionally, the reputational damage from repeated 429 errors can lead to negative press, forcing companies to invest in crisis management rather than infrastructure improvements.The Verified Baseline
Publicly available data on HTTP 429 incidents is sparse, but a few key insights emerge from industry reports and case studies. The World Wide Web Consortium (W3C) defines the 429 status code as a response to "requests where the client exceeds the allowed rate," and its inclusion in HTTP/1.1 (1999) reflects an early recognition of the need to manage abusive traffic. However, the real-world application of this code has evolved significantly with the rise of cloud computing and API-driven architectures. Major platforms like Google, Amazon, and Twitter have all documented instances where 429 errors surfaced during traffic spikes, often tied to promotional campaigns or third-party integrations gone wrong. One verified example comes from a 2018 incident involving a popular streaming service. During a highly anticipated movie release, the platform’s API began returning 429 errors for users attempting to stream content. The issue wasn’t a DDoS attack but rather a misconfigured rate-limiting rule that treated legitimate concurrent streams as suspicious activity. The service’s support team was flooded with complaints, and while the problem was resolved within hours, the damage to user trust was lasting. This case underscores a critical point: HTTP 429 errors are not just technical artifacts; they’re symptoms of deeper architectural flaws in how traffic is managed and prioritized.What the Estimates Suggest
Industry estimates suggest that HTTP 429 errors are far more common than most users realize, though exact figures are difficult to pin down. According to reports from cloud infrastructure providers, up to 30% of API requests during peak periods may trigger a 429 response if proper rate-limiting mechanisms aren’t in place. For companies relying on third-party APIs—such as payment processors or social media integrations—the risk is even higher, as they inherit the rate-limiting policies of the external service. Estimates for the financial impact vary widely, but figures around the £50,000–£200,000 range have been suggested for mid-sized businesses experiencing prolonged 429-related outages during critical sales periods. The operational overhead of mitigating 429 errors is another often-overlooked cost. Organizations must invest in monitoring tools, scalable infrastructure, and developer time to implement solutions like token bucket algorithms or adaptive rate limiting. These measures aren’t cheap; some industry analysts estimate that the average cost of scaling an API to handle sudden traffic surges can reach £100,000 or more, depending on the complexity of the system. Smaller businesses, in particular, may lack the resources to implement these safeguards, leaving them vulnerable to both external attacks and their own traffic management failures.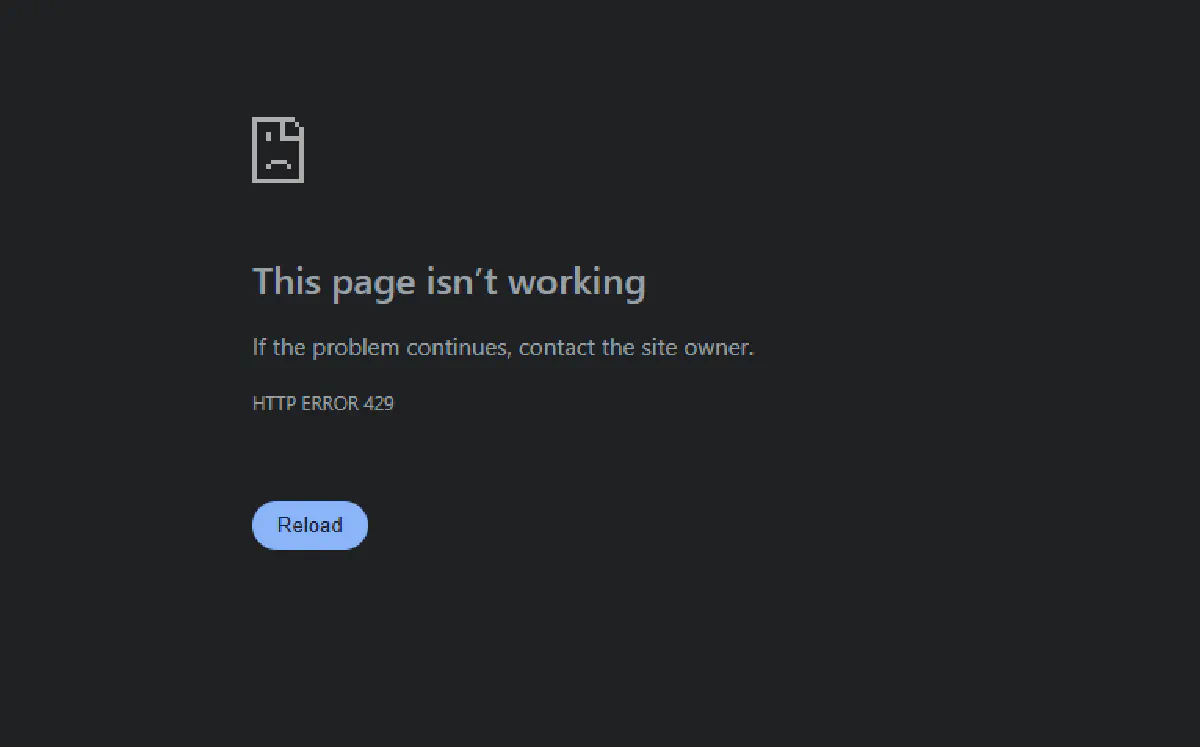
Case Study: A Closer Look
In 2020, a fintech startup specializing in microloans experienced a surge in API requests after partnering with a major bank for a promotional campaign. The campaign was designed to drive thousands of new users to the platform within a 48-hour window, but the startup’s rate-limiting policies were not adjusted in tandem with the expected traffic. As a result, the platform’s backend began returning HTTP 429 errors to legitimate users attempting to complete loan applications. The immediate effect was a 40% drop in successful submissions during the peak hours, directly impacting the campaign’s conversion goals. The fallout was swift. Users who encountered the 429 errors assumed the platform was down or intentionally blocking access, leading to a spike in customer service inquiries and negative reviews on third-party sites. The company’s CTO later admitted that the incident could have been avoided with better load testing and dynamic rate-limiting adjustments. "We treated the 429 as a security feature, not a user experience issue," he said in a post-mortem interview. "That’s a mindset shift that cost us more than just lost sales—it cost us trust."| Factor | Estimated Impact |
|---|---|
| Lost Conversions | Reportedly 30–45% of peak-hour submissions failed due to 429 errors. |
| Customer Support Overhead | Increased by 200% during the incident, with most inquiries related to failed transactions. |
| Reputational Damage | Negative reviews and social media mentions spiked, though long-term brand impact remains unclear. |
What This Means Going Forward
The rise of HTTP 429 as a dominant status code in modern web traffic reflects broader trends in digital infrastructure. As APIs become the backbone of nearly every online service, the pressure to balance security and usability grows more intense. Organizations that treat 429 errors as an afterthought risk not only financial losses but also strategic setbacks in an era where reliability is a competitive differentiator. The solution lies in proactive traffic management—using machine learning to predict spikes, implementing adaptive rate limiting, and communicating transparently with users when issues arise. For end-users, the proliferation of 429 errors serves as a reminder of the fragility of digital systems. What once seemed like an abstract technical detail now directly impacts daily interactions, from online shopping to accessing essential services. The challenge for developers and businesses alike is to design systems that anticipate failure without sacrificing performance. This means moving beyond static rate limits and embracing dynamic, context-aware policies that distinguish between malicious and legitimate traffic. The goal isn’t to eliminate 429 errors entirely—it’s to ensure they’re a last resort, not a first response.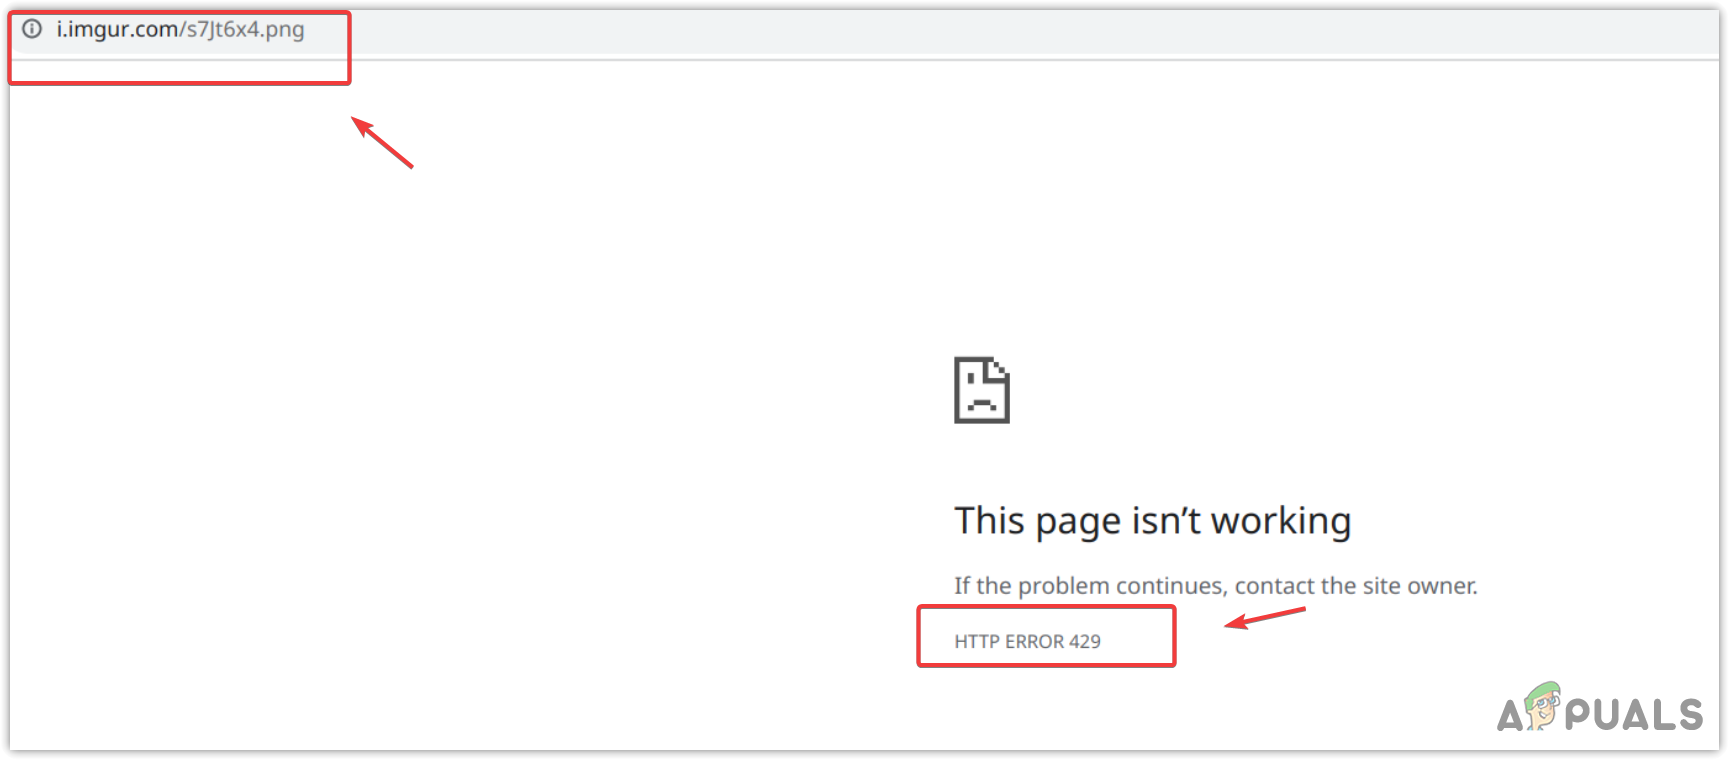
Conclusion
The HTTP 429 error is more than a line in a server log; it’s a reflection of the tensions inherent in building scalable, secure, and user-friendly digital experiences. While the code itself is a necessary tool for protecting systems, its unintended consequences reveal deeper flaws in how traffic is managed, monitored, and communicated. The fintech case study alone demonstrates that the cost of ignoring these errors extends far beyond immediate financial losses—it erodes trust, strains resources, and can derail even the most well-intentioned campaigns. For businesses, the lesson is clear: HTTP 429 errors are not just technical issues to be patched but strategic risks to be mitigated. This requires investment in infrastructure, a shift in mindset toward user-centric rate limiting, and a commitment to transparency when things go wrong. For users, it’s a call to pay closer attention to the systems they rely on, recognizing that even the most seamless digital experiences are built on fragile foundations. The next time a 429 error appears, it shouldn’t be met with frustration alone—it should be seen as an opportunity to demand better from the platforms we depend on.Comprehensive FAQs
Q: What’s the difference between a 429 error and a 503 Service Unavailable?
A: A 429 ("Too Many Requests") is a client-side error indicating the server is rejecting requests due to rate limits, while a 503 ("Service Unavailable") is a server-side error signaling the backend is down or overloaded. The key distinction is intent: 429 is proactive (security/load management), 503 is reactive (failure).
Q: Can I bypass a 429 error by using a VPN or proxy?
A: Technically possible, but ethically questionable and often against terms of service. Many platforms detect and block repeated requests from the same IP or user agent, even if routed through a VPN. Legitimate users should instead implement retry logic with exponential backoff.
Q: How do I know if my website is returning too many 429 errors?
A: Monitor server logs for 429 responses, track API call volumes, and use tools like Google Analytics or New Relic to correlate traffic spikes with error rates. If 429s exceed 5% of total requests during peak times, your rate limits may be too aggressive.
Q: Are there legal risks associated with 429 errors?
A: Indirectly. If 429 errors prevent users from accessing critical services (e.g., banking, healthcare), it could raise accessibility or consumer protection concerns. Platforms must ensure rate limits don’t disproportionately affect legitimate users under laws like the EU’s Digital Services Act.
Q: How can small businesses prevent 429 issues without expensive infrastructure?
A: Start with cloud-based auto-scaling (e.g., AWS Lambda), implement caching (CDNs like Cloudflare), and use third-party rate-limiting services. Prioritize gradual traffic testing during promotions and communicate proactively with users about expected delays.
Q: Do 429 errors affect SEO?
A: Indirectly. Search engines may deprioritize sites with frequent 429s if they indicate poor performance or accessibility. Ensure your server returns proper 429 headers (e.g., `Retry-After`) and avoid blocking crawlers, which can harm indexing.
Q: What’s the best way to handle 429 errors in mobile apps?
A: Implement retry logic with exponential backoff (e.g., wait 1s, then 2s, then 4s before retrying). Cache failed requests locally and notify users transparently (e.g., "High demand—please try again shortly"). Use background sync APIs to resume interrupted tasks.
Q: Can a 429 error trigger a GDPR complaint?
A: Unlikely unless the error prevents users from exercising rights (e.g., accessing or deleting personal data). However, if 429s are used to deliberately restrict access, it could violate transparency principles under GDPR. Always document rate-limiting policies and provide alternatives for affected users.
