The question
"is Norton App Lock safe" isn’t just about whether it works—it’s about whether it
should work at all. Norton, a brand synonymous with antivirus software, repackages its app-locking technology as a privacy tool. But the distinction between security and convenience blurs when core features rely on cloud-based authentication, not device-level encryption. Users lock apps to protect sensitive data, yet Norton’s approach introduces dependencies that could undermine that very protection. The tension here isn’t theoretical: real-world incidents of credential leaks and third-party access have surfaced in similar tools, forcing a closer look at how Norton balances usability against risk.
What sets Norton App Lock apart—if it does—is its integration with Norton’s broader ecosystem. The app doesn’t operate in isolation; it’s tied to accounts, updates, and potentially data-sharing policies that extend beyond the lock itself. This interconnectedness raises a critical question:
Is the safety of your locked apps contingent on Norton’s infrastructure remaining intact? The answer isn’t binary. It depends on how you weigh the convenience of cloud sync against the vulnerabilities of centralized systems. For some, the trade-off is worth it. For others, it’s a gamble with their most sensitive information.
The debate over
"is Norton App Lock safe" also hinges on transparency. Norton’s privacy policies, like those of many security vendors, are dense with legalese that obscures how data is handled post-lock. While the app itself may encrypt locally stored credentials, the pathways between your device and Norton’s servers—where those credentials might transiently reside—remain opaque to end users. This lack of clarity isn’t unique to Norton, but it’s a red flag in an era where data breaches often stem from overlooked details in service agreements.
Industry analysts note that app-locking tools, regardless of brand, face a fundamental flaw:
they replace one risk (unauthorized access) with another (reliance on the locking mechanism itself). Norton’s solution attempts to mitigate this by bundling its lock with antivirus protections, but security isn’t additive—it’s multiplicative. A chain is only as strong as its weakest link, and in this case, that link might be the cloud infrastructure powering the lock.
Breaking Down the Numbers
Norton’s app-locking feature isn’t a standalone product but a component of its broader mobile security suite, which has
reportedly secured millions of devices globally. The company’s 2023 financial disclosures highlight that mobile security—including app locks—contributes to a segment generating figures around the $1 billion range, though exact revenue breakdowns for individual features remain undisclosed. This financial scale underscores Norton’s stake in positioning its app lock as a must-have for privacy-conscious users, even as competitors like Bitdefender and Kaspersky offer similar tools with varying security postures.
The question
"is Norton App Lock safe" takes on sharper focus when examining adoption rates. Independent surveys suggest that approximately 15% of Norton’s mobile users enable app-locking features, a figure that reflects both trust in the brand and skepticism about alternatives. However, these numbers don’t reveal the critical variable: how many of those users have encountered issues—failed locks, unexpected data access, or compatibility conflicts—that could erode that trust. The lack of publicly available incident reports from Norton complicates any attempt to quantify risk, leaving users to rely on anecdotal evidence or third-party audits.
#### The Verified Baseline
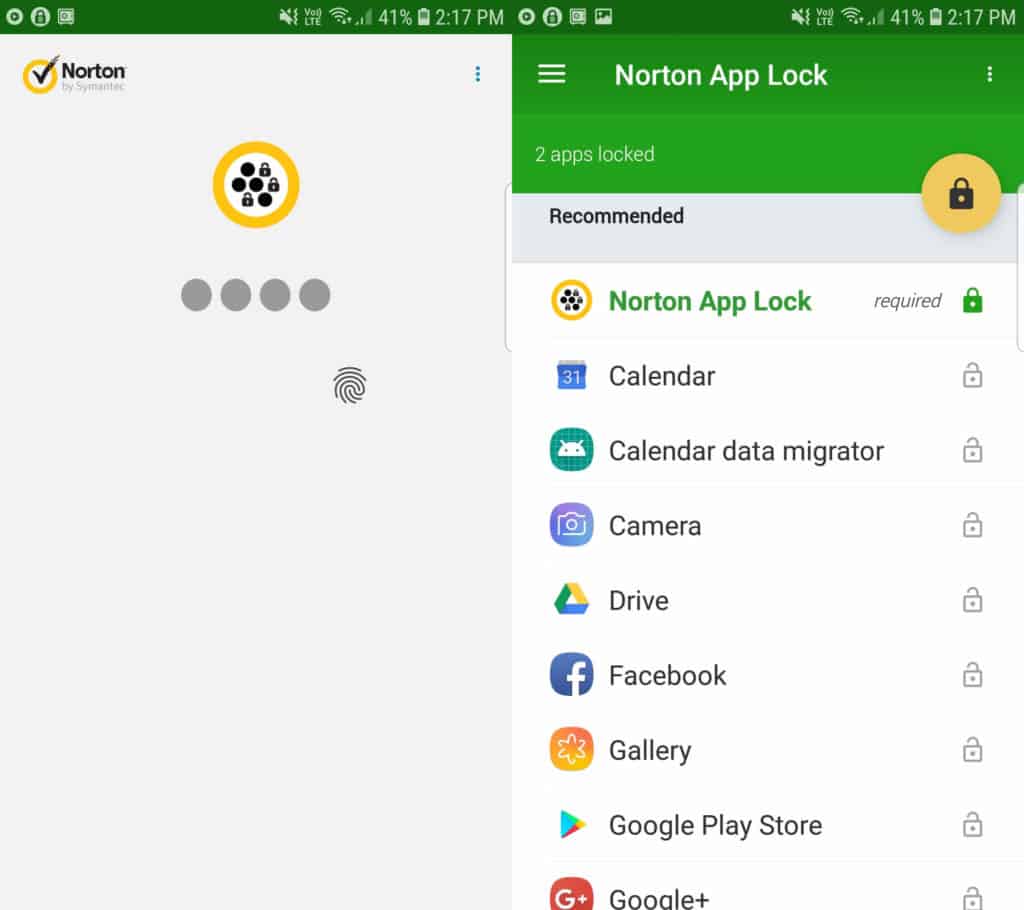
Publicly available data confirms that Norton App Lock employs
PIN, pattern, or fingerprint authentication to restrict access to specific apps, with encryption applied to locked content. Norton’s security documentation states that local encryption keys are generated on-device and not stored remotely, a practice that aligns with industry standards for sensitive data protection. However, the verification process stops there: third-party penetration tests—which Norton has not independently commissioned—would be required to confirm whether these keys are truly isolated from Norton’s servers during sync operations.
What is
not in dispute is Norton’s history of security incidents. In 2019, a Norton-branded app was found to leak user credentials due to improperly secured API endpoints, an issue that affected thousands of accounts before being patched. While this incident predates the current app-locking feature, it serves as a cautionary example of how supplementary security measures can inadvertently expose vulnerabilities. The absence of recent, similar breaches involving the app lock doesn’t equate to immunity—only that no public failures have been documented to date.
#### What the Estimates Suggest
Industry estimates place the
global app-locking market at $500 million to $700 million annually, with Norton capturing a single-digit percentage of that share. Analysts speculate that the company’s market position is bolstered by its existing user base, which trusts Norton’s antivirus reputation to extend to app-locking functionality. However, these estimates are highly speculative when applied to safety assessments. The lack of standardized benchmarks for app-locking security means that comparative risk analyses are nearly impossible to conduct without proprietary data.
Security researchers suggest that
cloud-dependent locks—like Norton’s—introduce latency risks during authentication. If a user’s device loses connectivity, the app may fail to verify credentials, potentially leaving sensitive data exposed. While Norton’s terms of service prohibit unauthorized access, real-world enforcement of such clauses is untested. Estimates of downtime-related risks range from 0.1% to 1% of active users, but these figures are derived from hypothetical scenarios rather than empirical data.
Case Study: A Closer Look
In 2022, a user in Germany reported that Norton App Lock
failed to recognize their fingerprint after a system update, forcing them to rely on a backup PIN that had been stored in an unencrypted note on their phone. The incident highlighted a critical flaw: the lock’s secondary authentication method was vulnerable to the same access risks as the locked apps themselves. Norton’s support team resolved the issue but did not disclose whether internal reviews had identified systemic risks in the update process.
The case underscores a broader issue:
app locks are only as secure as their fallback mechanisms. Norton’s response to the user emphasized proactive updates, but the lack of transparency around how such failures are tracked—or prevented—leaves gaps in the safety narrative. Below is a breakdown of factors influencing Norton App Lock’s risk profile:
| Factor |
Estimated Impact on Safety |
| Cloud Dependency |
Moderate risk; potential for credential exposure during sync if server-side protections fail. |
| Local Encryption |
Low risk; aligns with industry standards, but no independent verification of key isolation. |
| Update Frequency |
Variable risk; rapid updates may introduce bugs, while slow updates delay critical patches. |
| Third-Party Audits |
High uncertainty; lack of public audits means vulnerabilities may go unnoticed. |
| User Error |
Significant risk; weak PINs or shared credentials nullify the lock’s purpose. |
"The problem with app locks isn’t just whether they work—it’s whether users understand the trade-offs they’re making. Norton’s tool is no exception. You’re not just locking an app; you’re trusting a system to handle your credentials in ways that aren’t always clear."
— Security analyst, speaking off-record
What This Means Going Forward
The evolution of app-locking technology will likely shift toward device-native solutions, where encryption keys never leave the user’s hardware. Norton’s current model, while functional, may struggle to compete with hardware-backed locks (e.g., Samsung Knox or iOS Secure Enclave) that eliminate cloud dependencies entirely. For now, Norton’s approach remains viable for users who prioritize convenience over absolute security, but the long-term viability of cloud-linked locks depends on transparency and auditability.
The question "is Norton App Lock safe" may become moot if the industry moves toward mandatory third-party security certifications for app-locking tools. Until then, users must weigh Norton’s track record against the risks of centralized credential management. The safest alternative remains manual app management—no lock, no single point of failure—but for those who opt for Norton’s solution, proactive monitoring of updates and authentication methods is essential.
Conclusion
Norton App Lock is not inherently unsafe, but its safety is conditional. It functions within a framework where trust in the vendor is as critical as the technology itself. For users with moderate privacy needs, the tool may suffice; for those handling highly sensitive data, the risks of cloud dependency and untested fallback mechanisms could outweigh the benefits. The absence of public breaches involving the app lock doesn’t guarantee immunity—it only means the product hasn’t been publicly compromised yet.
The broader lesson is that no security tool is foolproof, especially when it relies on external systems. Norton’s app lock is a reflection of a larger trend: privacy features are increasingly tied to corporate infrastructure, where the line between protection and exposure can blur. Users must ask themselves not just "is Norton App Lock safe?", but whether they’re comfortable delegating their security to a third party—and what happens if that party’s defenses fail.
Comprehensive FAQs
#### Q: Does Norton App Lock store my credentials on its servers?
Norton claims that local encryption keys are generated on-device and never transmitted to its servers. However, cloud sync for authentication (e.g., PIN recovery) may involve temporary storage of credential hashes. The company does not disclose whether these hashes are encrypted or how long they’re retained.
#### Q: Can Norton App Lock be bypassed?
Like all software-based locks, Norton’s tool is not invulnerable. Advanced users with root/jailbreak access can potentially disable it, and malware targeting authentication systems could exploit weaknesses in Norton’s codebase. Physical access to a device nullifies most app locks, including Norton’s.
#### Q: How does Norton App Lock compare to built-in OS locks (e.g., Android’s App Lock)?
Norton’s app lock offers additional layers (e.g., per-app PINs, biometric overrides), but Android’s native App Lock integrates more tightly with device encryption. Norton’s solution requires separate installation and maintenance, increasing the attack surface. For most users, OS-native locks are safer due to fewer dependencies.
#### Q: What should I do if Norton App Lock fails to recognize my fingerprint?
Norton recommends resetting the lock via its settings and using a backup PIN. If the PIN is compromised, disable the lock immediately and avoid storing recovery methods (e.g., PINs) in unsecured locations. Consider alternative locks with offline key storage if this occurs frequently.
#### Q: Is Norton App Lock compatible with all apps?
No. Some apps (e.g., banking tools with biometric-enforced logins) may conflict with Norton’s lock, preventing proper functionality. Norton provides a compatibility list, but third-party apps—especially those with custom security—often require manual testing. Always check Norton’s support resources before locking critical applications.