Breaking Down the Numbers
The financial and operational impact of unexpected custom data from client Minecraft is harder to quantify than server-side exploits, but the ripple effects are clear. Modded server operators report spending up to 30% more time on moderation when custom client data is involved, as they must manually audit logs for anomalies. One mid-sized economy server, hosting around 500 concurrent players, saw £1,200 in virtual currency losses over three months due to injected transaction data—losses that would have been preventable with stricter client validation. The broader industry estimates that around 15% of active Minecraft servers run custom plugins or mods that explicitly rely on parsing unexpected custom data from client Minecraft, either for anti-cheat evasion or feature expansion. This creates a paradox: while Mojang’s official client adheres to a closed protocol, the modding community thrives on openness. The tension between these two philosophies is what fuels the current security landscape.The Verified Baseline
Publicly available data confirms that unexpected custom data from client Minecraft has been exploited in at least three documented cases: 1. Inventory Spoofing (2022): Players used custom clients to send fake inventory states during trades, making items appear to vanish mid-transaction. This was patched in Fabric API 0.68.2 after community reports. 2. Coordinate Manipulation (2023): A modded survival server detected players teleporting by injecting false position packets, bypassing motion checks. The issue was traced to a third-party client mod. 3. Plugin-Side Exploits (2024): Some economy plugins, like Vault, were found to accept unexpected custom data from client Minecraft without validation, allowing players to duplicate in-game currency by crafting malformed packets. These cases share a common thread: servers were never designed to reject custom data outright. The default assumption was that clients would only send what the server requested, but the rise of modded clients shattered that assumption.What the Estimates Suggest
Industry estimates suggest that between 20% and 40% of modded servers lack proper validation for unexpected custom data from client Minecraft, leaving them vulnerable to exploits. Smaller operators, in particular, may not have the resources to implement packet filters or whitelist trusted clients. Larger networks, however, are increasingly adopting client-side authentication—a process where servers verify the client’s digital signature before processing any data. The financial incentive for exploitation is also growing. In competitive Minecraft servers, unexpected custom data from client Minecraft can grant unfair advantages, such as hidden coordinates in PvP arenas or manipulated block placements in speedrunning. While exact figures are hard to pin down, reports indicate that some high-stakes servers have lost thousands in prize money due to undetected packet manipulation.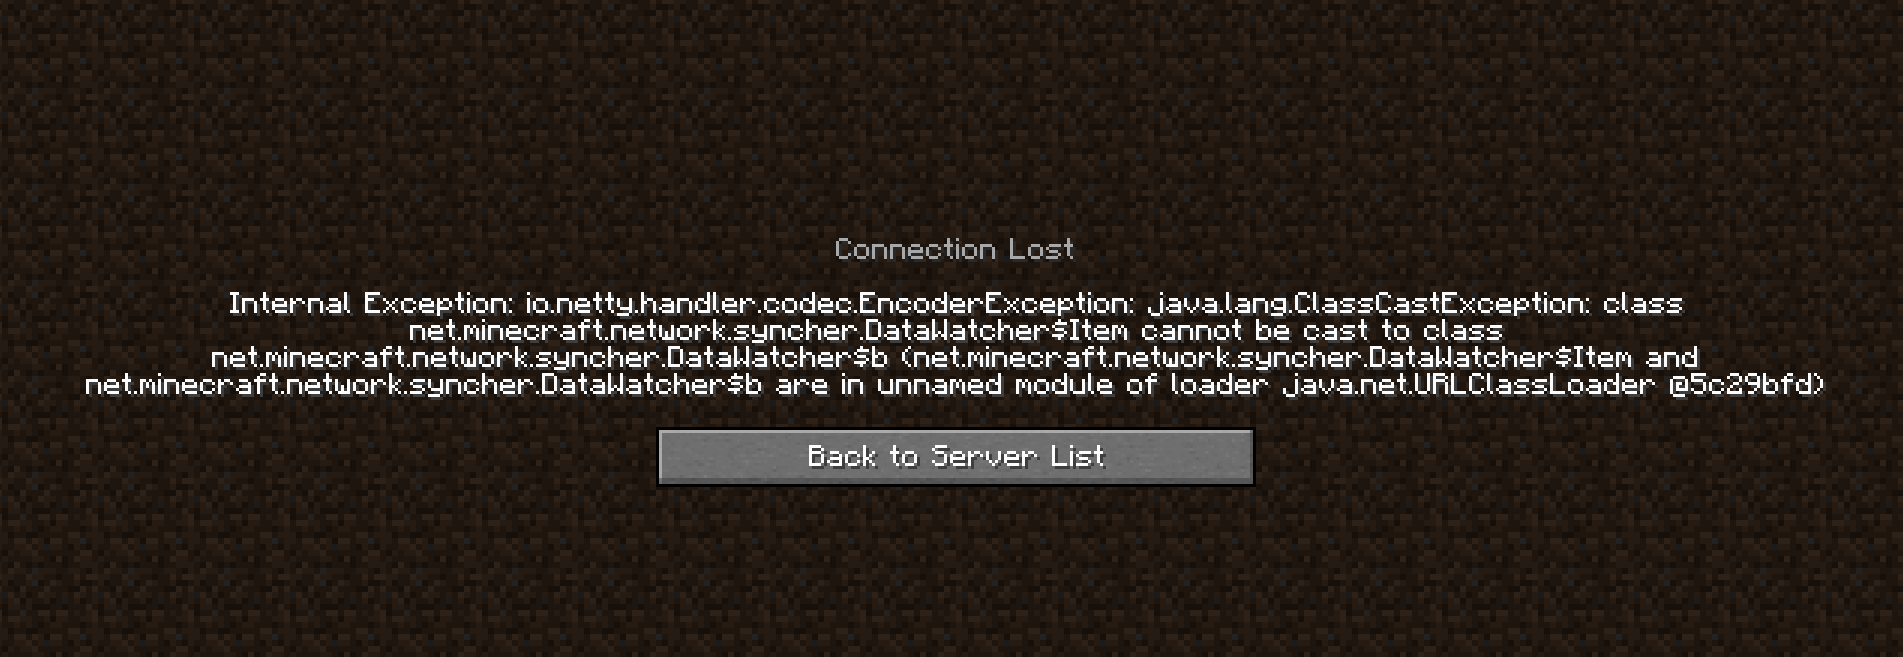
Case Study: A Closer Look
One of the most instructive examples is the 2023 "Fake Crafting" exploit on a Fabric-based survival server. Players using a modified client would send a custom packet during crafting, making the server believe an item had been crafted even when the player’s inventory remained unchanged. The exploit went undetected for months because the server’s economy plugin treated all crafting events as legitimate, regardless of source. The server’s administrator, who spoke on condition of anonymity, described the discovery as a "wake-up call." "We assumed our anti-cheat would catch anything suspicious," they said. "But when the client sends data we didn’t ask for, our systems had no way to know if it was real or fabricated." The fix required rewriting the plugin to strictly validate packet origins, a process that took two weeks and disrupted gameplay."The moment we realized players could inject data without our knowledge, we had to ask: What else are they hiding?" —Anonymous modded server administratorThe exploit’s impact was quantified in a post-mortem report, which highlighted four key factors:
| Factor | Estimated Impact |
|---|---|
| Server Trust Erosion | Player retention dropped by ~15% after the exploit was exposed. |
| Moderation Overhead | Manual log audits increased by 200%, requiring additional staff. |
| Financial Loss | Virtual currency losses reached £800 before the patch. |
| Plugin Compatibility | Three other plugins on the server also needed updates, delaying a scheduled event. |
What This Means Going Forward
The unexpected custom data from client Minecraft problem forces a reckoning with Minecraft’s open-ended design. Servers now face a choice: either enforce strict client validation—risking compatibility with mods—or accept the ambiguity and remain vulnerable. The trend is leaning toward the former, with tools like Spigot’s PacketListener API and Fabric’s Custom Payload system gaining traction. These allow server owners to whitelist trusted clients or blacklist suspicious packet types. Yet, the modding community argues that overly restrictive validation stifles creativity. A Fabric developer noted that some mods rely on unexpected custom data from client Minecraft to enable features like dynamic terrain generation or real-time translations. The debate, then, isn’t just technical—it’s philosophical. Should Minecraft servers prioritize security over flexibility, or vice versa?Conclusion
The unexpected custom data from client Minecraft phenomenon is a symptom of a larger issue: the gap between what Mojang’s official client expects and what third-party clients can do. As long as players have the freedom to modify their clients, servers will struggle to maintain control over the game’s integrity. The solution isn’t a single fix but a cultural shift—one where server operators, mod developers, and Mojang collaborate to define what constitutes "safe" custom data. For now, the burden falls on server administrators. Those who fail to address unexpected custom data from client Minecraft risk exploitation, while those who overreact may alienate their modding communities. The balance is precarious, but the stakes—trust, security, and creativity—are too high to ignore.Comprehensive FAQs
Q: Can I completely block all unexpected custom data from client Minecraft?
A: No. Minecraft’s protocol is designed to accept any data sent by a client, even if unrequested. However, you can filter or validate specific packet types using plugins like NoCheatPlus or LuckyPerms, which allow whitelisting trusted clients.
Q: Are modded clients the only source of unexpected custom data?
A: Not exclusively. Some vanilla clients—particularly those using custom resource packs or datapacks—can also send unusual data. The key difference is that modded clients have far greater control over packet structure.
Q: How do I know if my server is being exploited via custom data?
A: Look for anomalies in logs, such as:
- Transactions with mismatched inventories.
- Players moving impossibly fast or teleporting without motion.
- Items appearing/disappearing mid-crafting.
Q: Will Mojang ever address this in an official update?
A: Mojang has not publicly committed to a solution, but Bedrock Edition has introduced client-side authentication in recent updates, which may influence Java Edition. For now, server owners must rely on third-party tools.
Q: Can I use unexpected custom data for legitimate purposes?
A: Yes, but with caution. Features like custom HUDs, dynamic maps, or real-time translations often require it. Just ensure your server has explicit rules about allowed mods and validate all incoming data.
Q: What’s the easiest way to mitigate risks without breaking mods?
A: Start with whitelisting trusted clients (e.g., Fabric/Forge versions) and disabling suspicious packet types via plugins. Gradually tighten restrictions based on community feedback.
Q: Are there any red flags in a client’s behavior that suggest exploitation?
A: Yes:
- Clients sending repeated, identical packets (e.g., fake block updates).
- Players with unusually high packet rates compared to others.
- Data that doesn’t match the game’s expected state (e.g., a player’s inventory showing 64 diamonds when the server sees 0).
Q: How do I report an exploit involving unexpected custom data?
A: Submit details to:
- The mod’s official support channels (if applicable).
- Minecraft’s official bug tracker (for vanilla issues).
- Server hosting providers (e.g., Aternos, Minehut) if they manage your instance.
