The Short Answers
- Basic hiding (no root): Use built-in features like `.nomedia` files or third-party apps (e.g., Solid Explorer with password protection).
- Encryption first: Files encrypted with Android’s built-in encryption or apps like Cryptomator can’t be read even if hidden.
- Root access unlocks deeper hiding (e.g., mounting partitions as read-only or using
mount -o bindtricks). - Avoid system-level hiding apps—many log your activity or bundle malware. Stick to open-source tools.
- Cloud backups (e.g., Proton Drive) add redundancy but require their own security layers.
- For maximum stealth, combine hiding with app sandboxing (e.g.,
Termuxfor encrypted containers).
Deep Dive: The Full Picture
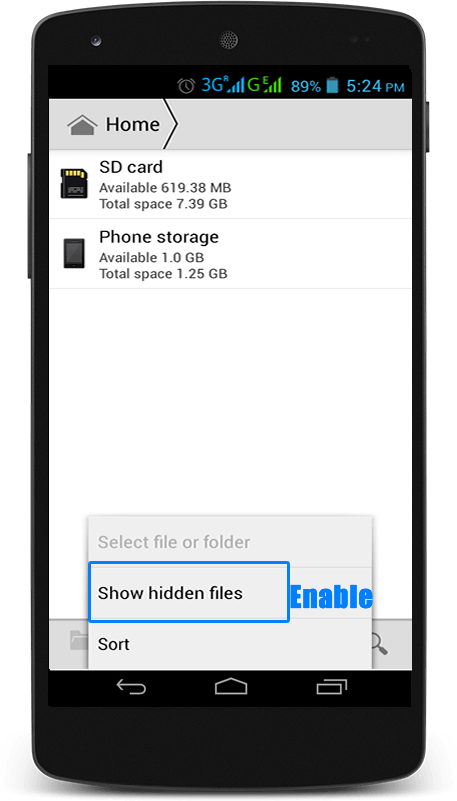
Android’s file system isn’t designed for secrecy. Files live in plaintext unless explicitly encrypted, and even "hidden" folders can be exposed with the right tools. The most robust methods hide files on Android by exploiting gaps in the OS’s default permissions model—gaps that developers rarely document. For example, Android’sMediaStore API ignores files prefixed with a dot (`.`), but this only works for media; other file types (PDFs, databases) remain visible unless further masked.
The real challenge lies in balancing obscurity with usability. A file hidden behind three layers of encryption might be secure, but retrieving it on a daily basis becomes a hassle. The best systems let you toggle visibility dynamically—say, via a password-protected launcher or a dedicated app that only surfaces files when explicitly requested.
The Context You Need
Android’s permission model is a double-edged sword. While it restricts apps from accessing arbitrary files, it also means no single method works universally. A file hidden in the/sdcard/Android/data directory might be invisible to one app but fully accessible to another with the right permissions. Even "hidden" system folders (like /data/data) can be browsed with root access or ADB commands.
The rise of file-hiding apps has created a false sense of security. Many rely on simple renaming tricks (e.g., appending .txt to an APK) or moving files to obscure locations like /mnt/shell/emulated. These methods fail against determined snooping—whether from a tech-savvy roommate or forensic analysis after a device theft.
The Mechanics
At the core, hiding files on Android hinges on three techniques: 1. Obfuscation: Renaming files to mimic system files (e.g.,boot.img for a sensitive document) or using non-standard extensions (e.g., .jpg.vault).
2. Permission-based hiding: Leveraging Android’s MODE_PRIVATE or MODE_WORLD_READABLE flags to restrict access.
3. Encryption + hiding: Combining AES-256 encryption (via apps like K-9 Mail’s attachment encryption) with hidden storage paths.
For non-rooted devices, the most reliable path is app-level encryption. Tools like Cryptomator or VeraCrypt (via Termux) create encrypted containers that appear as empty files to prying eyes. Pair this with a hidden folder (e.g., /.hidden) and you’ve added two layers of defense.
Details That Change the Picture
Not all hiding methods are equal. Hiding files on Android via third-party apps introduces risks: some log your activity, others inject ads or trackers. The safest route is to use open-source tools with minimal permissions—like FX File Explorer’s built-in encryption or Simple Encryption for individual files. A critical oversight is backup files. Even if you hide a document, its temporary or auto-saved versions might linger in/Android/obb or /cache. Always clear these manually or use apps like CCleaner (with caution—some versions bundle bloatware).
"The average user thinks hiding a file is enough. But Android’s file system is a ticking time bomb—permissions change, apps update, and a single misconfigured setting can expose everything. True privacy means assuming the device will be compromised and building layers accordingly." —Security researcher (anonymous, 2023)
| Method | Effectiveness |
|---|---|
Dot-prefixed folders (/.hidden) |
Low (visible via ADB or root) |
| Encrypted containers (Cryptomator) | High (requires password) |
Root-level binding (mount -o bind) |
Very High (but breaks on unroot) |
| App sandboxing (Termux) | Extreme (isolated environment) |
| Cloud sync with zero-knowledge | Moderate (depends on provider) |
Conclusion
Hiding files on Android isn’t about finding a single "best" method—it’s about stacking techniques to create a mosaic of obstacles. Start with encryption, then layer obfuscation, and finally add behavioral controls (e.g., disabling file previews in settings). Remember: the weakest link isn’t the hiding method itself, but the human factor—like reusing passwords or ignoring app permission warnings. For most users, a combination of Cryptomator for encryption and FX File Explorer for hidden folders strikes the right balance. Power users might explore root-level tricks, but the trade-off in usability and device stability often isn’t worth it. The key is adaptability: if one layer fails, the next should still hold.Comprehensive FAQs
Q: Can I hide files without root access?
A: Yes. Use the .nomedia trick for media files or apps like Solid Explorer with password-protected archives. For broader hiding, encrypt files first (e.g., with Cryptomator) and store them in a dot-prefixed folder (/.hidden).
Q: Will hiding files affect my device’s performance?
A: Minimally, unless you’re using resource-heavy encryption tools. Apps like VeraCrypt (via Termux) can slow down I/O operations, but lightweight options (e.g., Simple Encryption) have negligible impact.
Q: Are there risks to using third-party file-hiding apps?
A: Absolutely. Many bundle trackers, request unnecessary permissions, or store your files on their servers. Stick to open-source tools or built-in Android features. If you must use an app, audit its permissions and reviews first.
Q: Can police or forensic tools bypass hidden files?
A: If the device is rooted or accessed via ADB, most hiding methods can be bypassed. Encryption is your last line of defense—without the password, even hidden files remain unreadable. For extreme cases, consider full-disk encryption (Android’s built-in option) or hardware-level solutions like Blackphone.
Q: How do I hide files from cloud backups?
A: Exclude folders from backup in Google Drive settings or use apps like Syncthing with selective sync. For maximum control, encrypt files before uploading and store the key offline.
Q: What’s the most secure way to hide sensitive files long-term?
A: Combine AES-256 encryption (via VeraCrypt or Cryptomator), a hidden folder (/.secure), and a secondary device for key storage. Avoid keeping encrypted files on the same device as the decryption tool.
