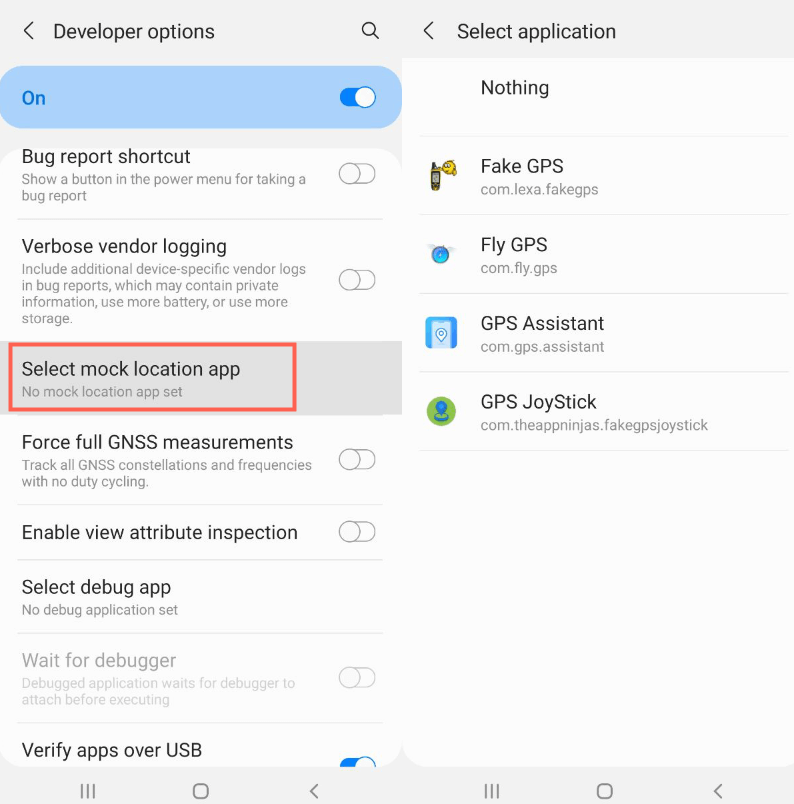
Common Myths About Android Allow Mock Locations
The first misconception is that android allow mock locations is a universal workaround for any app requiring location data. In reality, the feature only affects apps that explicitly request mock location permissions—most consumer apps ignore it entirely. Developers must integrate special APIs to interact with the mock provider, meaning casual users enabling the setting won’t suddenly break navigation apps or fitness trackers. The confusion stems from oversimplifying how Android’s permission model functions: mock locations don’t override system-wide GPS by default. Another persistent myth is that enabling android allow mock locations automatically grants access to all apps, including those without developer privileges. This is incorrect. Only apps with the `ACCESS_MOCK_LOCATION` permission can utilize the feature, and even then, they must request user consent to switch to mock data. Google’s Play Store policies mandate that apps disclose this capability in their privacy policies, yet many users overlook these disclaimers. The result? A false sense of control, as users assume they’re in charge of location spoofing when the app itself dictates the rules. A third myth suggests that android allow mock locations can be used to fool two-factor authentication systems relying on geolocation. While technically possible for apps with mock access, most 2FA systems employ additional layers—such as device fingerprinting or behavioral analysis—to detect anomalies. Banks and services like Google Authenticator typically require physical GPS movement or cellular tower triangulation, making mock locations ineffective as a standalone bypass. The myth persists because security discussions often focus on theoretical vulnerabilities without addressing real-world mitigations.Myth 1: Enabling Mock Locations Bypasses All Location Restrictions
The idea that android allow mock locations acts as a universal override for geofencing or regional content locks is a fundamental misunderstanding. Mock locations only affect apps that explicitly support the feature. For example, a banking app might ignore mock data entirely, while a custom-built navigation tool could use it to simulate a drive. The restriction exists because Android’s security model treats mock locations as an opt-in developer feature, not a system-wide toggle. Users enabling the setting won’t suddenly access Netflix libraries from another country or bypass age-restricted apps—those systems rely on IP or carrier-based checks, not GPS alone. The confusion likely originates from high-profile cases where location spoofing was used to exploit services. For instance, some gaming apps have been caught using mock locations to grant unfair advantages, but these are exceptions requiring deliberate app design. Most apps treat mock locations as a red flag: if an app requests mock permissions without clear justification (e.g., testing), Google may flag it during review. The key takeaway is that android allow mock locations is a tool for developers, not a consumer-facing bypass.Myth 2: Mock Locations Are Completely Safe for Everyday Use
While android allow mock locations is safe for developers testing apps in controlled environments, enabling it on a daily basis introduces unnecessary risks. The primary concern is that malicious apps could abuse the feature to track users without their knowledge. For example, an app with mock permissions might log a user’s real location when they’re not actively using it, then switch to mock data to hide its activity. Android’s permission model doesn’t prevent this—it only requires apps to declare their intent to use mock locations, not to restrict their behavior afterward. Another risk is that enabling mock locations could interfere with legitimate services. Some apps, like ride-sharing platforms, verify location changes in real time to prevent fraud. If a user’s phone suddenly reports jumping from New York to Tokyo, the app might flag the account for review or disable services. The lack of a "whitelist" for trusted apps means users must manually disable mock locations when not in use, a step many overlook. The assumption that mock locations are harmless ignores the broader ecosystem of apps that rely on location integrity.Myth 3: Google Play Blocks All Apps Using Mock Locations
Google’s stance on android allow mock locations is nuanced: the company doesn’t block apps that use the feature outright, but it enforces strict policies around transparency and user consent. Apps must disclose in their privacy policy if they use mock locations, and they cannot use the feature to deceive users or violate terms of service. However, enforcement is reactive—Google reviews apps post-submission, meaning some misuse slips through until reported. This creates a false impression that mock location apps are automatically banned, when in reality, the burden of compliance falls on developers. The myth likely stems from high-profile removals, such as apps caught spoofing locations to manipulate leaderboards or unlock content. Yet many legitimate apps—like those for AR testing or accessibility tools—use mock locations without issue. The distinction lies in intent: Google targets apps that exploit mock locations to gain unfair advantages, not those using them for development or ethical testing. Users must look beyond the feature’s presence and examine whether the app provides clear reasons for its use.
What Holds Up to Scrutiny
At its core, android allow mock locations is a developer tool with a clear purpose: to simulate location data for testing without physical movement. The feature’s implementation is deliberate—Android separates mock locations from real GPS to prevent accidental misuse. When enabled, apps must explicitly request mock data via APIs, and users receive prompts to confirm the switch. This design ensures that mock locations aren’t a passive setting but an active choice, requiring both developer integration and user awareness. The evidence supports that android allow mock locations is effective for its intended use. Developers report using it to test geofenced features, optimize battery usage in location-heavy apps, and debug navigation algorithms. For example, a mapping app might use mock locations to simulate driving through complex urban areas without actually moving. The feature’s limitations—such as requiring manual toggling—reflect Android’s commitment to security, as it prevents apps from silently spoofing locations without user knowledge. > "Mock locations are a double-edged sword: powerful for developers but risky if misused. The key is transparency—apps must be clear about why they need this access, and users must stay informed about what they’re enabling." > — Android Security Team (2023 Policy Update)| Common Belief | What the Evidence Says |
|---|---|
| Mock locations can bypass all location checks. | Only apps with ACCESS_MOCK_LOCATION permission can use them; most apps ignore the setting. |
| Enabling mock locations is safe for everyday use. | Risks include app interference, potential tracking, and service disruptions if location changes appear unnatural. |
| Google automatically blocks apps using mock locations. | Google enforces policies post-submission; compliance depends on app transparency and user consent. |
Why the Confusion Persists
The primary reason for ongoing confusion is Android’s fragmented communication between technical documentation and user-facing guidance. Developer resources explain android allow mock locations in depth, but consumer documentation often glosses over its implications. Users enabling the setting may not realize they’re modifying a developer tool, leading to assumptions about its functionality. Additionally, the feature’s name—mock locations—suggests a broader capability than it actually has, reinforcing the myth that it’s a universal override. Another factor is the lack of real-time feedback when mock locations are active. Unlike GPS spoofing on iOS, which can trigger system alerts, Android’s mock locations operate silently unless an app explicitly notifies the user. This absence of visual cues leaves users unaware of potential issues until they arise, such as when an app behaves unexpectedly. The design prioritizes developer flexibility over user awareness, creating a gap that misinformation fills.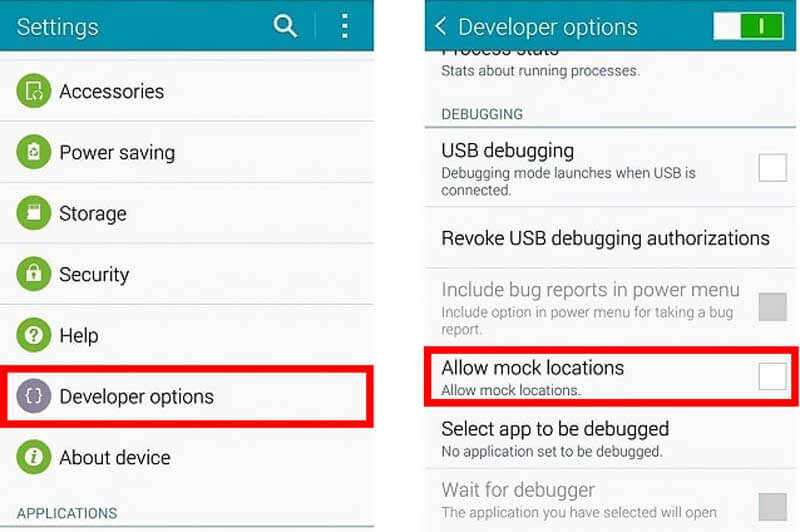
Conclusion
Android allow mock locations remains a double-edged tool: indispensable for developers but fraught with risks for casual users. Its existence highlights a broader tension in mobile platforms—balancing innovation with security while ensuring users understand the trade-offs. The feature’s limitations—requiring explicit app integration and user consent—demonstrate that Android’s designers anticipated misuse, even if the average user doesn’t recognize the safeguards in place. For most people, enabling android allow mock locations is unnecessary and potentially harmful. The setting is best left to developers testing apps in controlled environments, with users disabling it afterward. Those who do enable it should verify that only trusted apps have mock location permissions and monitor for unusual behavior. The key to mitigating risks lies in education: understanding that mock locations are a niche tool, not a consumer feature, and that their misuse can have unintended consequences.Comprehensive FAQs
Q: Can I use android allow mock locations to trick apps like Uber or Google Maps?
No. While android allow mock locations can simulate location data, most major apps—including Uber and Google Maps—ignore mock sources unless explicitly configured to use them. These apps rely on real-time GPS or cellular signals for core functionality, and mock data won’t override those inputs. Attempting to do so may result in account flags or service disruptions.
Q: Will enabling mock locations drain my battery faster?
Not directly. Mock locations themselves don’t consume additional battery, but enabling the feature and using apps that rely on it could indirectly affect battery life. For example, if an app constantly switches between mock and real locations for testing, it may trigger more frequent GPS checks. However, the impact is minimal compared to active GPS usage.
Q: Can I use android allow mock locations to access region-locked content?
Unlikely. While some apps might respect mock locations for minor features, most region-locked services—like streaming platforms or banking apps—use a combination of IP addresses, carrier data, and device fingerprinting to enforce restrictions. Mock locations alone won’t bypass these checks, and attempting to do so could violate terms of service or trigger security reviews.
Q: Do I need root access to enable android allow mock locations?
No. Android allow mock locations is a built-in developer option accessible without root. Users only need to enable Developer Options (via Build Number taps) and toggle the setting. Root access is unnecessary and could void warranties or introduce security risks unrelated to mock locations.
Q: How do I know if an app is using mock locations without my knowledge?
Android doesn’t provide a direct way to audit mock location usage, but you can check an app’s permissions in Settings > Apps > [App Name] > Permissions. Look for Mock Locations under the location-related permissions. Additionally, review the app’s privacy policy for disclosures about mock location use. If an app requests this permission without a clear explanation, proceed with caution.
Q: Can I disable android allow mock locations remotely if my phone is lost?
No. Once enabled, android allow mock locations must be disabled manually through Developer Options. However, you can use Android Device Manager or Find My Device to lock or erase the phone remotely, which would reset all settings—including Developer Options. This is the most effective way to prevent unauthorized mock location use on a lost device.
Q: Are there any legitimate uses for android allow mock locations outside of app development?
Few, but some accessibility tools or custom ROMs use mock locations for specific purposes, such as simulating movement for testing screen readers or navigation aids. Most consumer applications, however, don’t require mock locations. If you encounter an app claiming to need mock permissions for non-developer reasons, investigate further—it may be exploiting the feature.
Q: Will Google notify me if an app abuses mock locations?
Google doesn’t send direct alerts for mock location abuse, but the company may take action against apps violating Play Store policies. Users can report suspicious apps through the Play Store, and Google’s reviews may uncover misuse. Additionally, some security apps monitor for unusual location behavior, though they can’t detect mock usage alone.
Q: Can I use android allow mock locations to test a custom app I’m developing?
Yes, this is the intended use. If you’re developing an app that requires location testing, android allow mock locations is a standard tool. Ensure your app requests the `ACCESS_MOCK_LOCATION` permission and discloses its use in the privacy policy to comply with Google’s guidelines. Always test on a device where mock locations won’t interfere with real-world services.
