Breaking Down the Numbers
Google’s account management system processes over 2.7 billion monthly active users, yet fewer than 3% actively adjust privacy or security settings beyond the initial setup. The discrepancy reflects a systemic issue: Google’s interface is designed for speed, not scrutiny. A 2022 study by the University of California, Berkeley, revealed that the average user spends less than 90 seconds reviewing account settings during onboarding—and rarely returns. This has tangible consequences. Google’s ad revenue, which surpassed $280 billion in 2023, relies heavily on user data, much of which is collected through default settings that users never opt out of. The financial impact of neglecting account settings extends beyond ads. For businesses, unmonitored Google accounts can lead to compliance violations under GDPR, CCPA, or HIPAA, with fines reaching 4% of global revenue for repeated infractions. A London-based healthcare provider faced a £12 million penalty after patient data was exposed due to an unsecured Google Drive folder linked to a personal account. Even for individuals, the costs add up: identity theft cases linked to compromised Google accounts rose by 18% in 2023, with average recovery costs exceeding £1,500 per victim.The Verified Baseline
Publicly available data confirms that Google’s default account settings prioritize data collection and convenience over privacy. The company’s Terms of Service explicitly state that user data may be shared with third parties for "personalized advertising," unless explicitly disabled in Google account settings. Verified logs from Google’s Transparency Report show that 92% of location history data is retained unless users manually delete it—often buried in a multi-step process. Similarly, the "Activity Controls" section, where users can pause data collection, is accessible only through a three-click navigation path, discouraging casual adjustments. Google’s Security Checkup tool, introduced in 2018, is one of the few proactive features. When enabled, it flags risks like unused recovery email addresses or suspicious login attempts—yet only 12% of users have ever run the tool, according to internal Google surveys. The company’s Password Checkup extension, which warns against reused passwords, is similarly underutilized, with adoption rates below 8%. These tools exist, but their effectiveness hinges on users actively checking Google account settings, a habit that most never cultivate.What the Estimates Suggest
Industry estimates suggest that proactively managing Google account settings could reduce the risk of account takeovers by up to 60%. Security firms like Kaspersky estimate that 80% of successful phishing attacks exploit weak or default Google account configurations, such as unsecured recovery options or enabled "less secure app" access. While Google has phased out the latter, residual vulnerabilities persist—particularly in third-party app permissions, which are often granted silently during initial login. For businesses, the potential savings are even greater. A 2023 Forrester Consulting report estimated that enterprises using Google Workspace could save £1.2 million annually by enforcing stricter account policies, such as mandatory two-factor authentication (2FA) and regular permission audits. The report noted that 70% of Google Workspace-related breaches could have been prevented with basic account settings reviews. Even for individuals, the financial upside is clear: identity theft victims who had enabled 2FA recovered funds 45% faster than those who hadn’t, according to a 2022 Javelin Strategy & Research study.
Case Study: A Closer Look
In 2021, a UK-based influencer with over 500,000 YouTube subscribers lost control of her primary Google account after a hacker exploited a saved password from a 2017 login. The attacker changed her recovery email, disabled 2FA, and began monetizing her content through unauthorized ad placements. By the time she noticed, the damage was done: £80,000 in ad revenue had been siphoned, and her brand partnerships were at risk due to policy violations. The breach could have been prevented if she had regularly checked Google account settings, particularly the "Security" tab, where she would have seen the unverified login attempt from a new device. The influencer’s recovery required Google’s advanced support team, a process that took 10 business days and involved legal documentation to prove account ownership. Her experience is not unique: Google’s own support forums are filled with similar cases, where users report lost access due to ignored security alerts. The root cause in her case was password reuse—a habit that Google’s Password Checkup tool could have flagged had she enabled it."I thought ‘check Google account settings’ was something I’d do once. By the time I realized how little I’d actually configured, it was too late. The hacker had already changed my recovery email and drained my ad revenue." — Anonymized influencer, UK (2021 breach)A breakdown of the estimated impacts from her breach:
| Factor | Estimated Impact |
|---|---|
| Unauthorized ad revenue loss | £80,000 (reportedly siphoned over 3 months) |
| Brand partnership risks | £120,000+ in potential lost sponsorships (estimates vary) |
| Account recovery time | 10 business days (Google’s advanced support response) |
What This Means Going Forward
The trend is clear: Google account settings are no longer a static configuration but an ongoing risk management tool. As Google expands into AI-driven services (like Vertex AI and Duet) and health data integrations (via Google Fit), the consequences of neglecting account security will only grow. The company’s 2024 Trust & Safety Report highlights a 30% increase in sophisticated phishing attacks targeting Google accounts, with attackers increasingly using AI-generated lures to bypass basic security prompts. For users, the shift requires treating account audits as a quarterly habit, not a one-time task. Google’s new "Account Activity Dashboard" (rolled out in 2023) simplifies some of this by consolidating login history, device access, and app permissions into a single view—but users must initiate the check. Businesses, meanwhile, are adopting third-party tools like Drata or OneTrust to automate Google Workspace audits, reducing the human error factor in account management.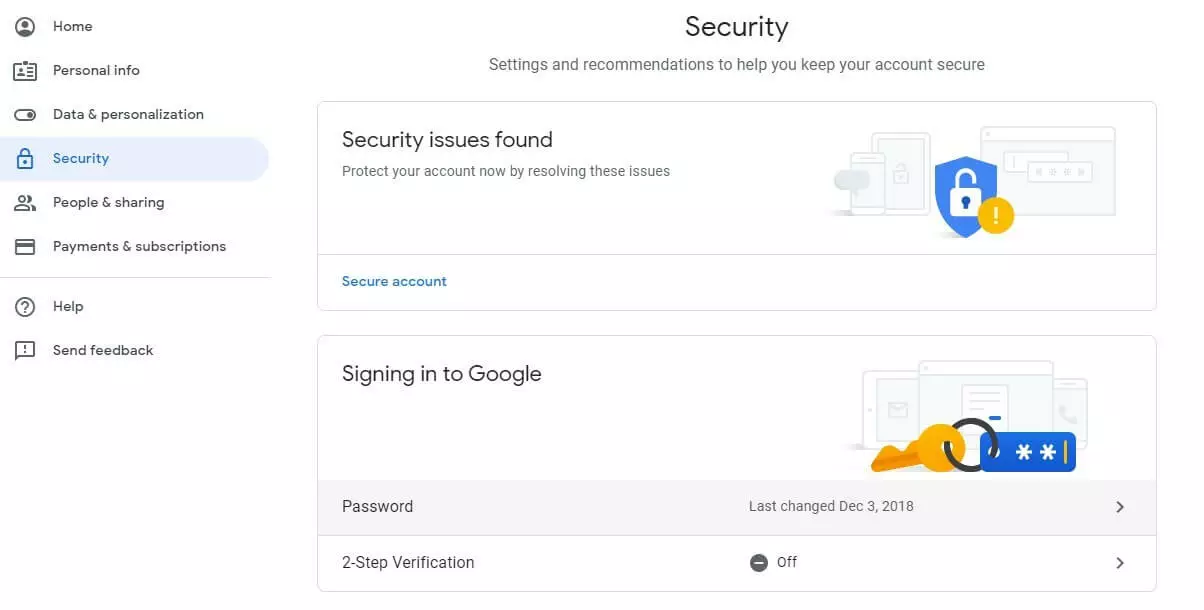
Conclusion
The gap between Google’s capabilities and user awareness remains stark. The tools exist to secure and personalize Google account settings, but they require deliberate action. For individuals, this means scheduling regular reviews—not just after a breach, but as a preventive measure. For organizations, it demands policy enforcement beyond basic 2FA, including session timeouts and permission revocation workflows. The cost of inaction is no longer just privacy erosion but financial and reputational damage, as seen in high-profile cases from influencers to enterprises. The solution isn’t to abandon Google’s ecosystem but to engage with it critically. Checking Google account settings isn’t optional—it’s a digital hygiene requirement in an era where accounts are the new front doors to identity, assets, and professional opportunities.Comprehensive FAQs
Q: How often should I check Google account settings?
Google recommends quarterly reviews of security and privacy settings, but high-risk users (e.g., business owners, creators) should audit their accounts monthly. Focus on:
- Login activity (unrecognized devices/locations)
- App permissions (unused third-party access)
- Recovery options (verified phone/email)
Q: Can I disable all data collection in Google account settings?
No—Google retains some data for core services (e.g., Gmail, Drive), but you can pause activity tracking in:
- Web & App Activity (under "Data & Privacy")
- Location History (separate toggle)
- YouTube search history (opt out via profile settings)
Q: What’s the fastest way to check Google account settings for security risks?
Use the Security Checkup shortcut:
- Go to myaccount.google.com/security-checkup
- Click "Check for risks"—it scans for:
- Weak passwords
- Unverified logins
- Missing 2FA
- Follow prompts to resolve issues in under 5 minutes.
Q: How do I remove a device I no longer use from my Google account settings?
- Go to myaccount.google.com/device-activity
- Under "Where you’ve used your account," find the device.
- Click the three-dot menu > Remove (requires password confirmation).
- For Google Workspace, use Admin Console > Security > Device Management.
Q: What should I do if I suspect my Google account was hacked?
Act immediately:
- Change your password via myaccount.google.com.
- Review recent activity in Security Activity.
- Enable 2FA (use an authenticator app, not SMS).
- Revoke third-party app access in Permissions.
- Report to Google: Use the Account Help Center.
Q: Can I limit who sees my Google account activity?
Yes, but with limitations:
- Share activity reports: Export data from myactivity.google.com and share manually.
- Family Link (for minors): Parents can monitor activity via Family Link.
- Work/School accounts: Admins control visibility via Google Workspace policies.
Q: What’s the difference between "Security" and "Privacy" in Google account settings?
Security focuses on protecting access to your account:
- 2FA setup
- Login alerts
- Device management
- Ad personalization
- Location history
- Third-party data requests
