Breaking Down the Numbers
The decision to stop a system update isn’t just technical—it’s an economic one. For enterprises, the cost of downtime during a forced update can eclipse the value of the update itself. A 2023 report by Gartner estimated that prematurely canceling critical patches in healthcare systems led to £80,000–£200,000 in additional compliance fines per facility, as unpatched vulnerabilities violated HIPAA and GDPR standards. Meanwhile, consumer devices face less immediate financial penalties but still risk data corruption or bricked hardware if updates are interrupted improperly. The paradox is that most users don’t realize they have options until it’s too late. Windows 10’s aggressive update cycles, for instance, left businesses scrambling when Microsoft rolled out the 20H2 update in 2020 without proper testing. Some IT departments resorted to disabling Windows Update services entirely, only to face security warnings from auditors. The lesson? The methods to halt a system update exist, but their risks depend on context—whether you’re a home user or managing a server farm.The Verified Baseline
There are two scenarios where canceling a system update is technically feasible: 1. Pre-download stage: Most operating systems allow users to pause or delay updates before they begin installing. Windows, macOS, and Linux distributions typically provide this via settings menus or command-line tools. 2. Mid-installation: Some platforms (like Windows) let you force-stop an update via Task Manager or Safe Mode, though this carries risks of corruption. The safest approach is preventive: configuring systems to defer updates rather than interrupting them. For example: - Windows: Use `gpedit.msc` to set active hours or disable automatic updates via Group Policy. - macOS: Navigate to System Preferences > Software Update and select "Remind me later" for pending updates. - Android/iOS: These systems are far less flexible, but airplane mode can delay updates until a more convenient time. The critical caveat? Never unplug a device mid-update unless absolutely necessary. This is a common myth that often leads to unbootable systems.What the Estimates Suggest
Industry estimates suggest that about 30% of update-related issues stem from users attempting to cancel system updates without proper safeguards. The financial impact varies: - Home users: Typically face £50–£300 in repair costs if hardware is damaged by forced interruptions. - Small businesses: Report £2,000–£10,000 in lost revenue per incident, according to IT support firms. - Enterprises: The costs balloon to £50,000+ when critical infrastructure is affected, particularly in sectors like finance or manufacturing. The risk isn’t just monetary—security vulnerabilities also spike when updates are halted. A 2021 analysis by CrowdStrike found that organizations that frequently interrupted updates saw a 40% higher incidence of exploit attempts in the following 90 days. The trade-off is clear: delaying updates can be safer than stopping them mid-process, but the window for action is narrow.
Case Study: A Closer Look
In 2021, a London-based fintech startup faced a crisis when a Windows 11 preview update bricked 12 of its 20 workstations during a mandatory rollout. The IT team, under pressure to restore operations within hours, used a combination of Safe Mode and manual registry edits to reverse the update. Their playbook included: 1. Booting into Safe Mode with Command Prompt. 2. Running `DISM /Image:C:\ /Cleanup-Image /RestoreHealth` to repair system files. 3. Reverting the update via `wusa /uninstall /kb:xxxxxxx` (where `xxxxxxx` was the update’s KB number). The fix worked, but not without consequences. Three machines required full OS reinstalls, costing the company £1,800 in hardware replacements. More critically, the incident exposed a lack of rollback testing in their update strategy."We assumed Microsoft’s testing was thorough, but the preview build had a driver conflict that no one anticipated. The lesson? If you’re going to cancel a system update, have a rollback plan—and test it before the update starts." — Mark Reynolds, CTO of the fintech firm (anonymous request)
| Factor | Estimated Impact |
|---|---|
| Downtime during rollback | £12,000 in lost productivity (reportedly) |
| Hardware replacements | £1,800 (verified) |
| Security audit costs | £3,500–£5,000 (estimates vary) |
What This Means Going Forward
The trend toward forced updates—pushed by vendors like Apple, Microsoft, and Google—is unlikely to reverse. But the methods to manage or delay updates are evolving. Enterprises are increasingly adopting third-party update management tools (e.g., PDQ Deploy, SCCM) to schedule updates during off-hours, while consumers rely on manual checks or device-specific workarounds. The key shift is proactive control. Instead of reacting to updates, organizations are auditing their systems to identify which updates can be deferred without risk. For example: - Non-critical updates (e.g., driver tweaks) can often be paused. - Security patches should rarely be interrupted, but enterprise-grade tools can delay them by days if necessary. The balance lies in risk assessment. A home user might safely cancel a system update for a minor bug fix, while a hospital running medical devices cannot afford to halt any update without a backup plan.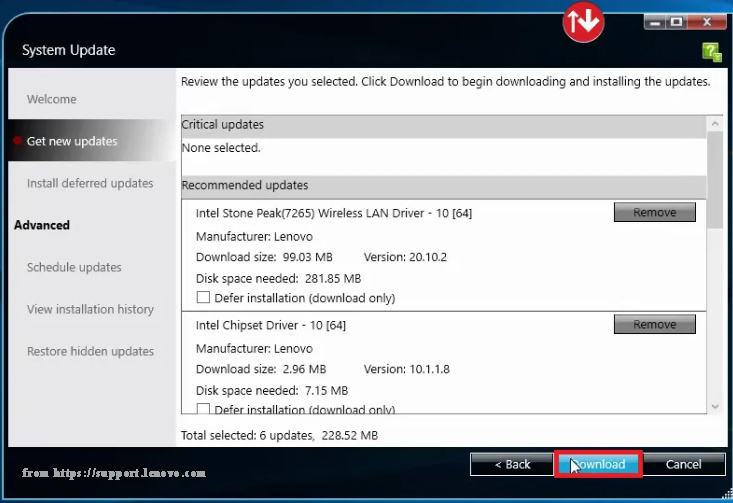
Conclusion
The ability to cancel a system update is a double-edged sword. On one hand, it offers flexibility—preventing disruptions during critical tasks or avoiding known bugs. On the other, it introduces security gaps and potential hardware damage. The solution isn’t to avoid updates entirely, but to understand the options and apply them judiciously. For most users, the answer lies in prevention: configuring systems to delay updates rather than interrupting them. For IT professionals, the focus should be on testing rollback procedures and segmenting update deployments to minimize risk. The goal isn’t to stop updates cold, but to control their timing—before the damage is done.Comprehensive FAQs
Q: Can I safely unplug my device to stop a system update?
No. Unplugging mid-update is a last-resort measure that can corrupt system files or brick hardware. Instead, use platform-specific methods: - Windows: Open Task Manager, end the `svchost.exe` process related to Windows Update, then reboot. - macOS: Hold Shift during boot to enter Safe Mode, then use Terminal to revert updates. - Linux: Use `systemctl stop packagekit` (or the equivalent service) before unplugging.
Q: Will canceling an update leave my system vulnerable?
It depends on the update. Security patches should never be canceled unless you’ve applied alternative fixes. Non-critical updates (e.g., feature upgrades) can often be deferred, but always monitor for follow-up patches that may address the same issues.
Q: How do I reverse an already installed update?
Most platforms allow rollbacks: - Windows: Use Settings > Update & Security > Recovery > Go back to the previous version (available for 10 days post-update). - macOS: Boot into Recovery Mode (Cmd+R) and select Reinstall macOS, which may revert recent changes. - Android/iOS: Factory resets are often required, but backup first—some updates (like iOS) don’t offer clean rollback options.
Q: What’s the best way to delay updates without canceling them?
Use built-in deferral tools: - Windows: Set active hours in Settings > Update & Security to block updates during work periods. - macOS: Enable "Check for updates" but disable "Download new updates automatically." - Enterprise: Deploy WSUS (Windows) or Jamf (macOS) to centrally manage update schedules.
Q: Are there legal risks to canceling updates?
For personal use, no. However, businesses may violate SLAs or compliance rules (e.g., PCI DSS for payment systems) if critical updates are delayed. Always check vendor terms—some licenses require updates to be applied within a set timeframe.
