
6 Things Worth Knowing About Bypassing Captchas
The CAPTCHA arms race isn’t just about breaking codes—it’s about understanding the psychology of automation, the economics of fraud, and the limits of machine learning. These six facts expose the hidden layers of a problem most users never see.1. CAPTCHAs Are Designed to Fail—Eventually
CAPTCHAs were never meant to be unbreakable. Their original architecture assumed that humans would always outperform machines in pattern recognition—a flaw that became apparent within years. Early systems like reCAPTCHA relied on distorted text, which proved trivial for optical character recognition (OCR) tools to crack. By 2014, academic research demonstrated that even simple neural networks could solve 99.8% of Google’s audio CAPTCHAs. The shift to behavioral analysis—tracking mouse movements, typing rhythms, or even pupil dilation—only delayed the inevitable. Today, adversarial machine learning trains models to mimic human-like interactions, making static challenges obsolete. The lesson? CAPTCHAs are a moving target, and their effectiveness hinges on constant evolution. Businesses that treat them as permanent solutions risk complacency. The real vulnerability lies in implementation. Many organizations deploy CAPTCHAs inconsistently—applying them to high-risk actions (like password resets) but ignoring low-risk ones (such as comment forms). This creates exploitable asymmetry: attackers focus on the weakest points, where CAPTCHAs are either absent or easily bypassed. Even when deployed correctly, CAPTCHAs can backfire. A 2021 study found that poorly designed challenges frustrate legitimate users more than they deter bots, driving away organic traffic. The paradox is clear: the harder you make it for humans, the more likely you are to push them toward alternative (often insecure) pathways.2. The Dark Market for CAPTCHA-Solving Services Is Thriving
What was once a niche hacker hobby has become a $1.5 billion industry, according to industry estimates. Dark web marketplaces like 2captcha and Anti-Captcha offer pay-per-solve services, where users submit CAPTCHAs and receive solutions in seconds. Prices vary: simple text CAPTCHAs cost pennies, while complex behavioral challenges can run $5–$10 each. The scale is staggering—some services claim to solve over 10 million CAPTCHAs daily, powering everything from ad fraud to credential harvesting. Legitimate businesses even use these services for internal testing, blurring the ethical line. The supply chain is global and decentralized. CAPTCHA farms in countries like India, the Philippines, and Eastern Europe employ low-wage workers to manually solve challenges, often under false pretenses (e.g., "data entry jobs"). Meanwhile, automated solvers—built using open-source tools like 2Captcha’s API or custom-trained models—eliminate the need for human labor. The result? A self-reinforcing cycle: as demand grows, so does the sophistication of the tools, which in turn makes CAPTCHAs harder to design. The market’s resilience stems from its adaptability—when one type of CAPTCHA is cracked, the sellers pivot to the next. For cybercriminals, the ROI is undeniable: a single automated account takeover can yield hundreds of thousands in stolen funds, with CAPTCHA bypassing as the gatekeeper.3. Machine Learning Has Turned the Tables on CAPTCHA Designers
The most dangerous CAPTCHA bypassers aren’t script kiddies—they’re AI researchers. In 2017, a team from Cornell University trained a model to solve Google’s Invisible reCAPTCHA with 99.8% accuracy by analyzing mouse movement patterns. By 2020, deepfake audio CAPTCHAs (using synthetic voices) were being cracked by voice-cloning algorithms. The arms race has entered a new phase: generative adversarial networks (GANs) now create fake "human" responses that fool even the most advanced behavioral detection. Companies like Cloudflare and Akamai have responded by integrating liveness detection—analyzing micro-expressions or heartbeat patterns—but these too are being reverse-engineered. The turning point came when CAPTCHA designers realized they were fighting their own creations. Many modern challenges are now AI-generated, meaning the same tools used to break them are also used to build them. For example, Google’s reCAPTCHA v3 scores interactions based on risk profiles, but attackers have learned to spoof these profiles by injecting noise into their requests. The irony? Some CAPTCHA-breaking models are trained on publicly available datasets of solved challenges—meaning the more a company deploys CAPTCHAs, the easier they become to crack. The only sustainable edge lies in dynamic, context-aware challenges that adapt in real time—but even those are vulnerable to model poisoning attacks, where attackers feed false data to skew the system.4. Bypassing CAPTCHAs Enables Some of the Web’s Most Lucrative Crimes
CAPTCHA evasion isn’t an abstract technical exercise—it’s the enabler of scalable fraud. The most profitable applications include: - Ad fraud: Fake clicks and impressions, where bots bypass CAPTCHAs to inflate ad spend. Estimates suggest $80 billion in ad fraud annually, with CAPTCHA bypassing as a critical component. - Credential stuffing: Automated attacks on login pages, where stolen credentials are tested against CAPTCHA-protected portals. A single bypass can unlock thousands of accounts in minutes. - Synthetic identity fraud: Creating fake accounts for loans, benefits, or dark web marketplaces. CAPTCHA solvers remove the last hurdle in automation. - Phishing and social engineering: Automated mass phishing campaigns rely on CAPTCHA bypassing to scale. A single compromised CAPTCHA can increase phishing success rates by 300%. The economics are brutal. For cybercriminals, the cost of bypassing a CAPTCHA is often less than the value of the data or access it unlocks. For example, a $1 CAPTCHA solver might grant access to a medical record worth $500 on the dark web. The asymmetry is exploited further by bulletproof hosting providers, who offer CAPTCHA-bypassing tools as part of their services, knowing they’re untouchable by law enforcement. The result? A feedback loop where the more valuable the target, the more resources attackers allocate to cracking its defenses.5. Legitimate Businesses Are the Biggest Unwitting Enablers
Blockquote: "CAPTCHAs are like putting a padlock on a door, then leaving the window open. Companies spend millions on security theater while ignoring the real vulnerabilities." — A former cybersecurity consultant at a Fortune 500 firm, speaking anonymously. The truth is uncomfortable: most CAPTCHA bypassing happens not because of flaws in the technology, but because of poor implementation. Many businesses deploy CAPTCHAs as a checkbox compliance measure—ticking a box for GDPR or PCI DSS without considering the user experience. Others integrate them after an attack, treating them as a band-aid rather than a strategic layer. The consequences are predictable: frustrated users abandon high-friction flows, while attackers exploit the gaps. For example, a 2023 report found that 60% of CAPTCHA deployments were placed on low-risk endpoints (e.g., newsletter signups), where bypassing had minimal impact. Even worse, some companies outsource CAPTCHA solving to third parties without realizing the risks. A 2022 breach at a major e-commerce platform revealed that its internal CAPTCHA testing team had been using dark web solvers—unaware that their credentials were being harvested. The problem isn’t just technical; it’s cultural. Many organizations view CAPTCHAs as a binary defense (either they work or they don’t) rather than a dynamic risk management tool. Until that mindset shifts, bypassing will remain an inevitability—not a glitch.6. The Future of CAPTCHAs Is Already Being Written—And It’s Not What You Think
The death of traditional CAPTCHAs has been predicted for over a decade, yet they persist because nothing better has replaced them. The next generation of authentication isn’t about breaking codes—it’s about continuous verification. Leading-edge systems now use: - Behavioral biometrics: Analyzing typing speed, swipe patterns, or even subconscious micro-gestures (e.g., how a user holds their phone). - Zero-trust architectures: Assuming breach and verifying every action, not just the initial login. - Decentralized identity: Blockchain-based credentials that don’t rely on static challenges. Yet even these aren’t foolproof. In 2023, researchers demonstrated that deepfake behavioral biometrics could mimic human interactions with 92% accuracy. The arms race continues, but the goalposts have moved. Instead of CAPTCHAs, we’re seeing a shift toward context-aware authentication, where risk is assessed dynamically. For example, a user accessing a banking app from an unusual location might face adaptive challenges—but these too can be bypassed with location-spoofing tools. The most intriguing development? CAPTCHAs are becoming obsolete for their original purpose. With passkeys (passwordless authentication) and biometric hardware (like Apple’s Touch ID) gaining traction, the need for text/image-based challenges is diminishing. The question isn’t whether CAPTCHAs will disappear—it’s what will replace them, and whether those systems will be equally vulnerable to bypassing.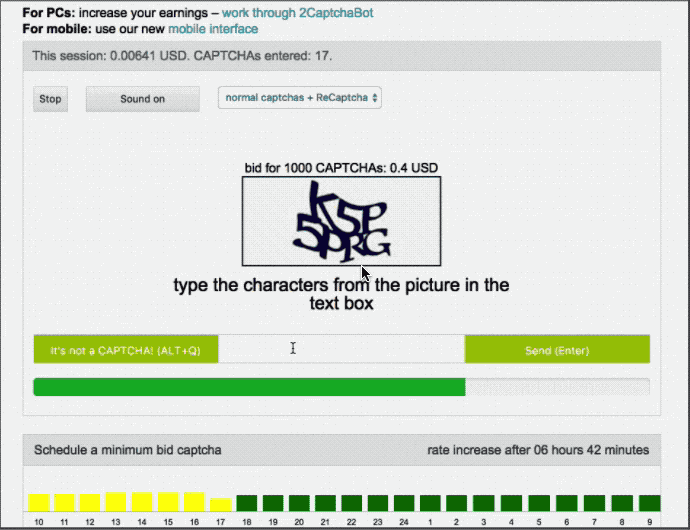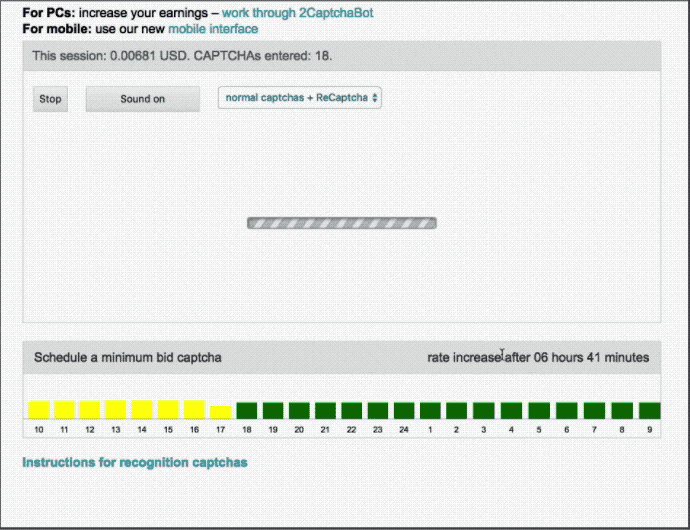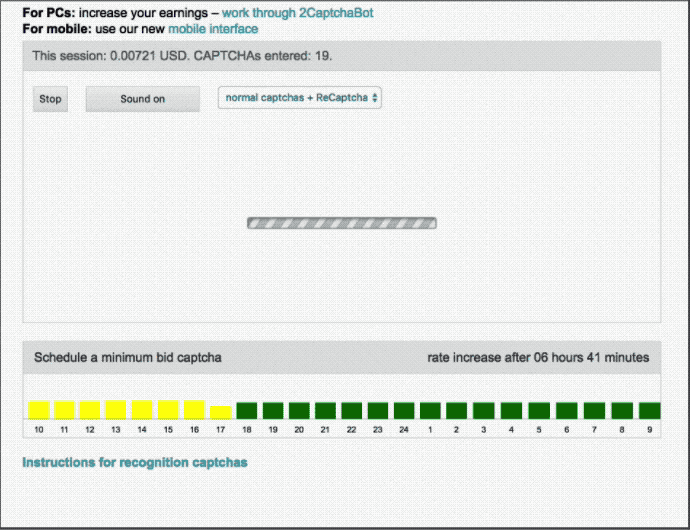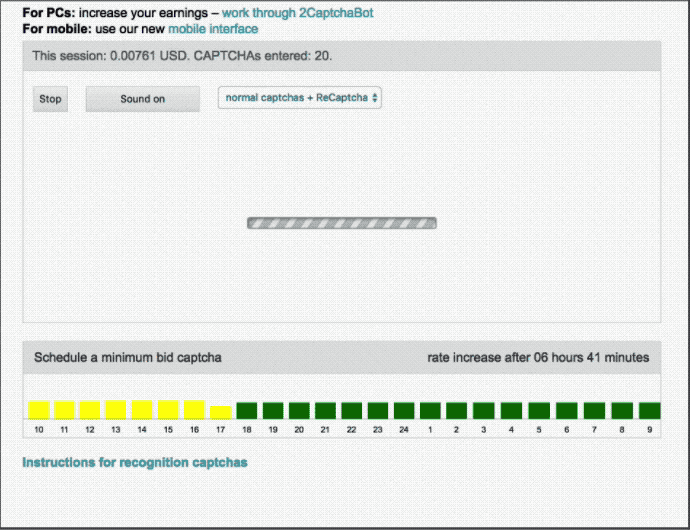
How These Facts Connect
The six insights above reveal a system under strain. CAPTCHAs were designed to solve a problem they couldn’t control: the unpredictability of automation. What started as a simple text puzzle has morphed into a high-stakes game of cat and mouse, where the mice (attackers) now often have the upper hand. The dark market’s growth isn’t just a side effect—it’s a direct consequence of CAPTCHAs being treated as a one-size-fits-all solution. Businesses deploy them without understanding the opportunity cost: frustrated users, compliance risks, and the illusion of security. The real vulnerability isn’t the technology itself, but the human factors surrounding it. CAPTCHAs fail when: 1. They’re overused (leading to user fatigue and workarounds). 2. They’re underused (leaving critical endpoints exposed). 3. They’re outsourced (to untrusted third parties or dark web services). 4. They’re static (rather than adaptive to evolving threats). The connection between these points is clear: CAPTCHAs are a symptom of a larger authentication crisis. They’re not the solution—they’re a temporary barrier in a system that demands continuous evolution. The companies that survive will be those that move beyond CAPTCHAs entirely, embracing multi-layered, context-aware security—while accepting that no system is unbreakable.| Key Insight | Root Cause | Real-World Impact |
|---|---|---|
| CAPTCHAs are designed to fail eventually | Static challenges can’t adapt to AI advancements | Businesses face $10B+ in annual automated attack losses |
| Dark market for CAPTCHA solvers is thriving | High demand + low barrier to entry for attackers | $1.5B industry fuels ad fraud, credential theft, and synthetic identities |
| Machine learning has turned the tables | AI trains on public CAPTCHA datasets, improving evasion | 99.8%+ success rates on modern challenges like reCAPTCHA v3 |
Conclusion
Bypassing captchas isn’t just a technical challenge—it’s a cultural and economic one. The tools to crack them are widely available, the incentives to use them are massive, and the defenses are perpetually one step behind. The irony is that CAPTCHAs, once hailed as a revolutionary security measure, have become a liability—a false sense of security that lulls organizations into complacency. The real question isn’t how to bypass them, but why we’re still relying on them at all. The future of authentication lies in abandoning the CAPTCHA mindset entirely. Instead of asking, "How do we make this harder for bots?" the focus should shift to: "How do we eliminate the need for static challenges?" Solutions like passwordless logins, behavioral AI, and decentralized identity offer paths forward—but they require investment, innovation, and a willingness to discard outdated assumptions. Until then, the arms race will continue, with CAPTCHAs serving as both a shield and a target in an endless cycle of adaptation.Comprehensive FAQs
Q: Are there legal consequences for bypassing CAPTCHAs?
The legality depends on intent and jurisdiction. In the U.S., the Computer Fraud and Abuse Act (CFAA) can prosecute unauthorized access, even if no data is stolen. However, personal use (e.g., bypassing a CAPTCHA to access a public forum) often falls into a gray area. Many countries (like the UK and EU) have stricter laws under cybercrime directives, where CAPTCHA bypassing for fraudulent purposes can lead to fines or imprisonment. The key distinction? Commercial exploitation (e.g., selling CAPTCHA-solving services) is far more likely to face legal action than individual use. Always check local laws—what’s tolerated in one region may be a felony in another.
Q: Can I bypass CAPTCHAs for legitimate purposes, like web scraping?
Technically, yes—but ethically and legally, it’s a minefield. Many websites include terms of service prohibiting automated access, and violating them can lead to IP bans, lawsuits, or DMCA takedowns. For legitimate scraping (e.g., research or journalism), alternatives like official APIs or rate-limited requests are safer. If CAPTCHAs are the only barrier, some developers use delayed automation (mimicking human timing) or proxy rotation to avoid detection. However, aggressive bypassing (e.g., using dark web solvers) risks triggering anti-scraping measures, including legal action under copyright or anti-fraud laws.
Q: What’s the most effective CAPTCHA-bypassing tool available today?
There’s no single "most effective" tool because the landscape shifts constantly. Off-the-shelf solutions include: - 2Captcha/Anti-Captcha APIs: Pay-per-solve services with 90%+ success rates on text/image CAPTCHAs. - Selenium + Python libraries: Open-source tools like selenium-wire or pyppeteer for automated browser interactions. - Custom-trained models: Using TensorFlow/PyTorch to crack behavioral CAPTCHAs (e.g., reCAPTCHA v3). - Dark web marketplaces: Services like Evasion.io or CAPTCHA.TO offer undetectable automation for a fee. For enterprise-grade bypassing, attackers often combine headless browsers, proxy networks, and AI-generated responses. The most dangerous tools aren’t public—they’re custom-built by cybercriminals or state actors.
Q: How do businesses detect CAPTCHA-bypassing attempts?
Modern detection relies on anomaly monitoring rather than static checks. Key methods include: - Behavioral fingerprinting: Analyzing mouse movements, typing speed, or device telemetry (e.g., screen resolution, time zone). - Request analysis: Flagging unusual patterns (e.g., rapid-fire submissions, identical user agents, or bot-like headers). - Honeypot traps: Deploying fake CAPTCHAs to identify automated solvers. - Machine learning models: Training classifiers on known bot behaviors, including CAPTCHA-solving APIs. - Rate limiting: Throttling requests from suspicious IPs or user agents. The most advanced systems (like Cloudflare Bot Management) use real-time risk scoring, where CAPTCHA bypassing triggers automated challenges—like dynamic puzzles or device verification.
Q: Can CAPTCHAs be made truly unbreakable?
No—but they can be made effectively unprofitable to break. The goal isn’t perfection; it’s raising the cost of bypassing higher than the potential gain. Strategies include: - Adaptive challenges: Changing CAPTCHAs based on user behavior (e.g., harder puzzles for new IPs). - Multi-factor layers: Combining CAPTCHAs with biometrics or hardware tokens. - Decoy systems: Deploying fake CAPTCHAs to waste attacker resources. - Economic deterrence: Making bypassing too slow or expensive (e.g., per-CAPTCHA delays). The most secure systems eliminate CAPTCHAs entirely, replacing them with continuous authentication (e.g., background device verification). However, these require user cooperation and high-precision AI—making them rare today.
Q: What’s the biggest misconception about CAPTCHA bypassing?
The biggest myth is that CAPTCHAs are a reliable security measure. In reality: - They frustrate legitimate users more than they deter bots. - They create false confidence—many businesses assume CAPTCHAs = security. - They’re easily bypassed at scale by automated tools. - They don’t stop motivated attackers—only slow them down. The real security comes from layered defenses: rate limiting, device binding, and anomaly detection. CAPTCHAs are a tactic, not a strategy—and treating them as such is the first step toward better security.
Q: Are there any industries where CAPTCHA bypassing is more common?
Yes—certain sectors are high-value targets for CAPTCHA evasion: - FinTech & Banking: Automated account takeovers via credential stuffing. - E-commerce: Ad fraud and fake reviews using CAPTCHA-bypassing bots. - Gambling & Casinos: Synthetic identity fraud to create fake accounts. - Healthcare: Medical record theft by exploiting weak login protections. - Social Media: Fake engagement (likes, follows) to manipulate algorithms. - Government & Utilities: Benefits fraud using automated identity creation. The common thread? High ROI for attackers. Wherever data or access has monetary value, CAPTCHA bypassing becomes a core tactic.
