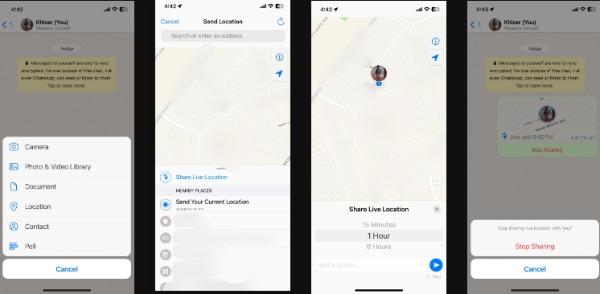
Common Myths About "Send My Location Pin"
 The convenience of sharing precise coordinates has spawned a host of assumptions—some comforting, others dangerously naive. One persistent belief is that only "tech-savvy" users need to worry about location tracking. In reality, the average smartphone user leaves a digital breadcrumb trail with every app permission granted, every social media check-in, and every "send my location pin" request. Another myth treats location data as ephemeral: once shared, it vanishes. Yet metadata from those pins often lingers in databases, sold to advertisers or accessed by law enforcement without a warrant in some jurisdictions.
The most insidious assumption is that sharing your pin is harmless unless you’re doing something illegal. But context matters little to algorithms. A domestic violence survivor sharing her pin with a trusted friend might unknowingly trigger a risk assessment by a landlord or employer reviewing her digital footprint. Meanwhile, businesses and governments increasingly treat location data as a commodity, not a privacy right. The disconnect between public perception and actual data flows explains why scandals—like the 2021 leak of 533 million Facebook users’ precise locations—shock even those who send my location pin daily.
Myth 1: "Only apps like Uber or Google Maps need my exact location"
Most users assume that unless they’re actively using navigation or ride-hailing apps, their location isn’t being harvested. The reality is far broader. Social media platforms, weather apps, and even fitness trackers request location permissions under the guise of "personalization." A 2023 study by the Norwegian Consumer Council found that 11 of the top 20 free Android apps shared location data with third parties without explicit user knowledge. Even when you decline permissions, some apps bypass opt-outs by defaulting to "approximate location" (which can still pinpoint you within 10–50 meters in urban areas). The danger escalates when you send my location pin proactively. A simple text to a friend might trigger a cascade: the recipient’s device logs the timestamp, their cloud backup stores it, and if their account is ever compromised, your coordinates become part of a larger dataset. Law enforcement agencies have subpoenaed location histories from service providers to reconstruct movements in criminal cases—even when the original intent was benign, like splitting a bill after dinner.Myth 2: "I can always revoke location access later"
The idea that location permissions are reversible is a illusion for many users. Apple and Android both allow granular control in settings, but the process is opaque. For instance, revoking an app’s location access might not delete historical data already uploaded to servers. Worse, some apps re-request permissions the next time you open them, forcing you to repeat the denial process. A 2022 investigation by The Markup revealed that even after users revoked permissions, apps like Yelp and Grubhub continued collecting location data via workarounds like IP geolocation. The problem deepens with third-party trackers embedded in ads or analytics tools. Clicking a link in a message that says "send my location pin" might trigger a hidden tracker that logs your coordinates before forwarding them to the intended recipient. This "shadow location sharing" is nearly impossible to detect without specialized tools like Exodus Privacy or network monitoring apps. The assumption that you’re in control is outdated—the system is designed to collect first, ask questions later.Myth 3: "Emergency services can’t misuse my location data"
In crises, the urgency to "send my location pin" overrides skepticism. Yet emergency call centers and dispatch systems often retain location data long after the incident resolves. In the U.S., the 911 location accuracy requirements mandate that calls must include GPS coordinates, but laws vary by state on how that data is stored. Some departments sell anonymized location histories to urban planners or insurers, while others have faced lawsuits for leaking coordinates to third parties. A 2021 report by the Electronic Frontier Foundation found that at least 17 states lack laws prohibiting police from sharing 911 location data with non-emergency agencies. Even in countries with strict privacy laws, exceptions abound. During the 2020 COVID-19 lockdowns, governments in Singapore and Israel used aggregated but precise location data to enforce curfews, raising ethical questions about surveillance under the guise of public safety. The message is clear: when you send my location pin to save a life, you’re also entrusting it to systems that may not prioritize your privacy.What Holds Up to Scrutiny
At its core, the act of sharing your location pin is a trade-off between utility and exposure. The verifiable benefits—faster emergency responses, safer navigation, and social coordination—are undeniable. When a 2019 study in JAMA Network Open analyzed 911 calls with GPS data, response times dropped by 23% in urban areas where coordinates were accurate to within 5 meters. Similarly, ride-sharing apps like Uber and Didi rely on real-time location sharing to match drivers and passengers, reducing wait times and improving safety through driver ratings tied to geofenced incidents. The mechanics behind "send my location pin" are also transparent in their basic form. Most mobile operating systems use A-GPS (Assisted GPS) to triangulate signals from cell towers, satellites, and Wi-Fi networks, providing accuracy within 2–10 meters in ideal conditions. Apps like Google Maps or Apple’s Find My Friends encrypt the data in transit, though the encryption keys are often stored on the recipient’s device—meaning if their phone is hacked, your pin is exposed. The system works as intended when all parties act in good faith."Location data is the new oil—it’s valuable, but once refined, it loses its raw form and becomes something else entirely. The problem isn’t the oil rig; it’s who controls the refinery." — Alastair MacTaggart, founder of Privacy Rights Clearinghouse (2022)

| Common Belief | What the Evidence Says |
|---|---|
| "Sharing my pin is private if I only send it to trusted people." | Recipients’ devices may log the data; screenshots or forwarded messages can leak it. Even encrypted pins can be decrypted if a device is compromised. |
| "Businesses can’t track me if I don’t use their app." | Ad trackers, cookies, and IP geolocation can estimate your location even without explicit permission. Some apps use "background location services" to collect data when closed. |
| "Turning off location services stops all tracking." | Wi-Fi and Bluetooth signals can still approximate your location. Some apps use "device fingerprinting" to correlate online behavior with physical whereabouts. |
| "Governments only access my location data in emergencies." | In the U.S., law enforcement can obtain historical location data with a stored communications warrant, which requires only probable cause—not the immediate threat needed for real-time tracking. |
| "Location pins disappear after I share them." | Most messaging apps (WhatsApp, iMessage, Telegram) retain location data in backups. Some third-party apps sell anonymized location histories to data brokers. |
Why the Confusion Persists
The gap between user awareness and technical reality stems from two factors: design by default and cultural normalization. Tech companies prioritize ease of use over privacy controls, burying settings in nested menus or disabling them by default. When you’re prompted to "send my location pin" with a single tap, the alternative—manually entering coordinates or explaining the risks—feels like overkill. This frictionless sharing masks the underlying infrastructure: databases, algorithms, and third-party vendors processing your data. Culturally, location sharing has evolved from a novelty to a social expectation. In 2015, only 34% of Americans were comfortable sharing their real-time location with others; by 2023, that figure rose to 68%, according to Pew Research. The shift reflects how apps like Snapchat’s "Snap Map" or Pokémon GO gamified geolocation, making it feel like a participatory experience rather than a privacy trade-off. Meanwhile, media narratives often frame location data as a tool for good—helping find missing children or optimize traffic—while downplaying the risks. The result is a perception gap: users see utility but underestimate the long-term consequences.Conclusion
The phrase "send my location pin" has become a reflex, a digital handshake that bridges strangers and loved ones alike. Yet beneath its surface lies a tension between convenience and control. The systems enabling this exchange—GPS, messaging apps, and cloud storage—were not built with privacy as a priority. They were built to collect, correlate, and capitalize on data, with users as the collateral. The solution isn’t to abandon location sharing entirely, but to approach it with intentionality. Before hitting "share," ask: Who will receive this? How will they store it? What happens if their device is lost or hacked? Tools like Signal’s disappearing messages or Firefly’s ephemeral location sharing offer alternatives, but adoption remains low. Regulation is catching up—GDPR’s "right to be forgotten" extends to location data in the EU, and California’s CCPA grants similar protections—but enforcement lags. Ultimately, the power to protect your pin lies in understanding that every "send my location pin" is a choice—and every choice has consequences.Comprehensive FAQs
Q: Can someone track my movements if I only send my location pin once?
A: A single shared pin provides a static point, but if sent repeatedly (e.g., for navigation updates), it creates a trail. Even one-off shares can be cross-referenced with other data—like Wi-Fi networks or cell towers—to estimate movement patterns. Always use apps with end-to-end encryption (e.g., Signal) and set location shares to expire after a set time.
Q: Will my employer or landlord see if I share my pin with a friend?
A: Indirectly, yes. If your messaging app syncs with cloud services (e.g., iCloud, Google Drive), your landlord or employer could access backups during legal proceedings. Use local-only messaging apps (like Session) or encrypt individual location shares to minimize exposure.
Q: Are there apps that let me share my location without giving it to third parties?
A: Yes. Firefly (by Apple) and Google’s "Share Live Location" (with temporary links) allow time-limited sharing without storing data long-term. For Android, Signal’s disappearing messages can include location pins that auto-delete. Avoid apps like Life360, which aggregate data for "family tracking" and sell insights to advertisers.
Q: What’s the most secure way to send my location pin in an emergency?
A: Use a dedicated emergency app like bSafe or Noonlight, which encrypts location data and routes it directly to first responders without third-party storage. If using a standard app, call 911 first, then share your pin via a burner number (e.g., Google Voice) to avoid linking the data to your primary contacts.
Q: Can I fake my location pin to protect my privacy?
A: Yes, but with limitations. Tools like Fake GPS (Android) or iTools (iOS) can spoof your coordinates, but they may trigger SIM card or IMEI-based location checks by carriers or law enforcement. This is risky for emergencies—always use real coordinates when safety is at stake.
Q: How do I check if an app is secretly tracking my location?
A: On Android, go to Settings > Apps > [App Name] > Permissions and revoke location access. On iOS, check Settings > Privacy > Location Services for active trackers. Use Exodus Privacy (Android) or uBlock Origin (browser) to detect hidden trackers. Note: Some apps use background location services even when closed.
Q: What should I do if I think my location pin was misused?
A: Act fast. Freeze your location data by revoking app permissions and reporting the incident to your carrier (they may have logs). File a complaint with the FTC (U.S.) or ICO (UK) if you suspect illegal data sharing. For stalking risks, document the misuse and contact local law enforcement—some jurisdictions treat unauthorized location tracking as a criminal offense.