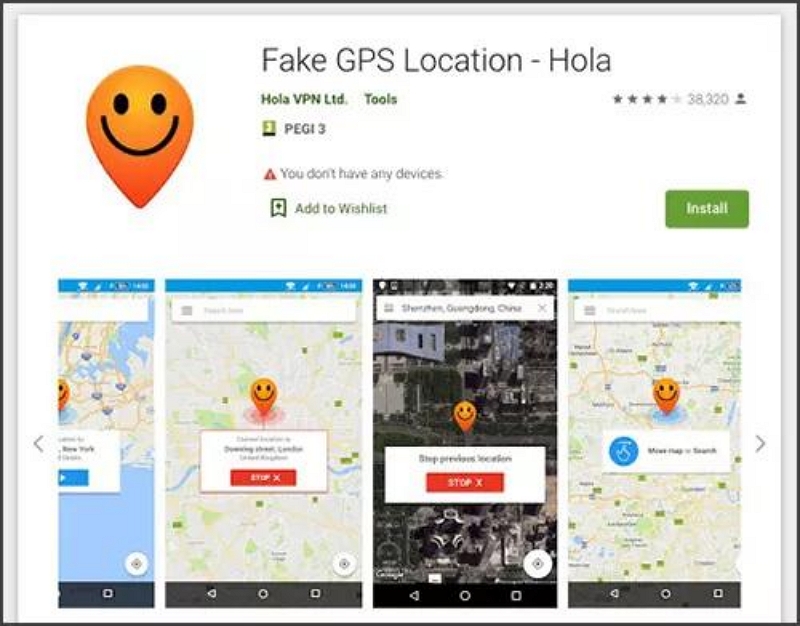
The Short Answers
- Fake GPS enable developer options lets users set custom coordinates, but it’s disabled by default for a reason.
- Enabling it requires unlocking developer settings, then navigating to Mock Locations or Location Settings.
- Common uses include cheating in location-based games (e.g., Pokémon GO) or testing apps—but fraud and stalking are growing concerns.
- Most banks and two-factor authentication systems verify GPS signals; spoofing can trigger account locks or fraud alerts.
- Android 11+ restricts mock locations to apps with special permissions, but jailbroken devices or rooted phones can bypass these limits.
- Legal consequences vary by jurisdiction, but insurance fraud, perjury, or aiding criminal activity can lead to charges.
Deep Dive: The Full Picture
The "fake GPS enable developer options" toggle isn’t just a relic of Android’s early days—it’s a living example of how seemingly benign developer tools can be weaponized. Google’s decision to keep this functionality, even with safeguards, reflects a broader tension: balancing the needs of developers against the risks of misuse. While the feature was introduced to streamline app testing, its real-world applications now range from harmless pranks to high-stakes deception. The lack of a one-size-fits-all solution means users, law enforcement, and tech firms are left navigating a gray area where intent often dictates consequence. What complicates matters is the ecosystem around location data. Apps like ride-sharing services, fitness trackers, and even dating platforms rely on GPS accuracy. When users enable "developer options to fake GPS", they’re not just altering their phone’s output—they’re potentially disrupting services that assume real-time, verifiable location signals. The domino effect can include false emergency alerts, incorrect delivery tracking, or even misrouted law enforcement responses. This isn’t just about cheating in a game; it’s about distorting the digital infrastructure we depend on daily.The Context You Need
The origins of "fake GPS via developer options" trace back to Android’s early iterations, where developers needed a way to simulate locations without physical movement. Google’s initial approach was to allow any app with the `ACCESS_MOCK_LOCATION` permission to override GPS data—a decision that made sense in a controlled testing environment but proved problematic in the wild. By Android 4.4, Google introduced restrictions, requiring users to explicitly enable mock locations in settings. Yet even these measures didn’t account for the rise of location-spoofing apps or the determined user who roots their device to bypass protections entirely. The problem escalated with the popularity of location-based games like Pokémon GO, where players discovered they could "teleport" to rare spawn points by enabling "developer options for fake GPS". What began as a community-driven workaround quickly attracted bad actors. Fraudsters, for instance, have used spoofed GPS to claim insurance payouts for non-existent accidents or to falsify their whereabouts during court proceedings. In one documented case, a defendant in a custody battle allegedly manipulated GPS logs to prove they were at work when they weren’t—a tactic that led to a suppression of evidence in court.The Mechanics
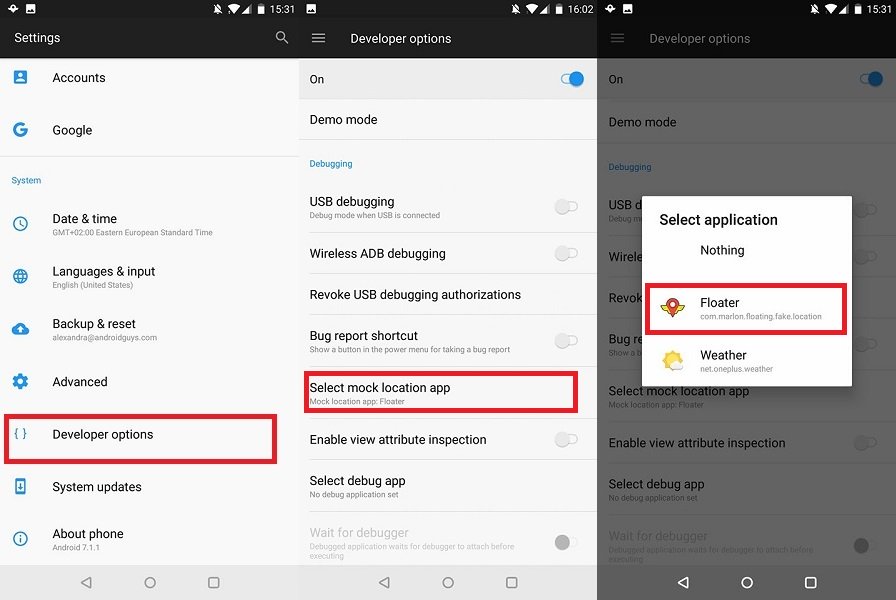
Enabling "fake GPS through developer options" follows a straightforward but deliberate process. First, users must unlock the hidden developer menu by tapping the Build Number entry in About Phone seven times. Once inside, they navigate to Developer Options and toggle Mock Locations to "on." The critical step comes next: selecting an app with the `ACCESS_MOCK_LOCATION` permission to inject custom coordinates. Without this permission, the system blocks the override, but apps like Fake GPS or Xposed Modules can grant it dynamically. The mechanics behind the spoofing itself are deceptively simple. The phone’s GPS chip receives signals from satellites, but when mock locations are active, the system ignores these inputs and instead uses the coordinates fed by the selected app. This works because Android’s location framework treats mock data as a higher-priority source—provided the user has granted the necessary permissions. The catch? This override extends beyond the phone itself. Apps using the Android Location Manager API will receive the fake coordinates, meaning services like Google Maps, banking apps, or even emergency call systems may display incorrect positions.Details That Change the Picture
The most immediate consequence of enabling "developer options to fake GPS" is the erosion of trust in location-based systems. Take ride-sharing apps: if a driver’s GPS is spoofed, passengers might be directed to the wrong location, or worse, the driver could vanish without a trace. Similarly, two-factor authentication systems that rely on GPS verification—such as those used by banks—can become vulnerable. A user enabling fake GPS to bypass security checks risks triggering fraud alerts or permanent account locks, as the system detects an anomaly in their reported location. Beyond individual risks, the broader impact touches on public safety. Emergency services rely on accurate GPS data to dispatch responders. If a user’s phone is set to a fake location during a 911 call, first responders might arrive at the wrong address—or not at all. While rare, documented cases of GPS spoofing in criminal investigations have led to dismissed evidence, as courts increasingly scrutinize the reliability of location data. The legal precedent here is still evolving, but the trend suggests that tampering with GPS—even for seemingly harmless reasons—can have unintended legal repercussions."The moment you enable mock locations, you’re no longer just playing a game—you’re participating in a system where trust is the currency. And once that trust is broken, the consequences aren’t just technical; they’re human." —Security researcher at a major tech firm, speaking off-record
| Scenario | Risk Level |
|---|---|
| Cheating in location-based games (e.g., Pokémon GO) | Low (but violates terms of service) |
| Fraudulent insurance claims or legal proceedings | High (potential legal action) |
| Bypassing GPS-based 2FA for banking | Critical (account lock or fraud) |
| Surveillance or stalking (e.g., faking a victim’s location) | Extreme (criminal liability) |

Conclusion
The "fake GPS enable developer options" feature remains a testament to the unintended consequences of giving users granular control over their devices. What was once a niche tool for developers has become a wildcard in a landscape where location data is increasingly tied to identity, security, and legal accountability. The challenge for tech companies isn’t just to lock down the feature—though Android’s incremental restrictions show progress—but to educate users about the ripple effects of their actions. A gamer spoofing their location for an in-game advantage might not anticipate the moment their bank flags their account for suspicious activity. Similarly, a developer testing an app could accidentally expose sensitive data if their mock locations bleed into production environments. The conversation around "developer options for fake GPS" is no longer confined to tech forums. It’s seeping into courtrooms, insurance disputes, and cybersecurity advisories, forcing a reckoning with how we define "legitimate" use of these tools. As long as the feature exists—and it will, for backward compatibility—users must weigh the convenience against the potential fallout. The question isn’t whether to enable it, but whether the stakes justify the risk in an era where location isn’t just data; it’s proof.Comprehensive FAQs
Q: Can I enable "fake GPS developer options" on iPhone?
No. Apple’s iOS restricts location spoofing at a system level, even in developer mode. Jailbreaking can bypass some protections, but Apple actively blocks mock location APIs in its ecosystem. Android’s more open architecture makes it the primary platform for this feature.
Q: Will enabling fake GPS get my account banned?
It depends on the service. Banks, payment processors, and social media platforms often monitor GPS anomalies for fraud. Enabling "developer options to fake GPS" could trigger account reviews, temporary locks, or permanent bans if the system detects inconsistent location patterns.
Q: Can law enforcement trace if I used fake GPS?
Not directly, but they can cross-reference other data. If your phone’s GPS logs show movement to a fake location while your IP address or Wi-Fi signals place you elsewhere, investigators may suspect tampering. In legal cases, this inconsistency can be used to challenge evidence tied to location data.
Q: Are there any legitimate uses for fake GPS?
Yes, but they’re limited to controlled environments. App developers use it to test location-based features without physical travel. Security researchers may simulate attacks to assess system vulnerabilities. Outside these cases, most uses blur into ethical gray areas.
Q: How do I know if someone is faking their GPS?
Look for red flags: sudden, impossible movements (e.g., teleporting across continents in seconds), or coordinates that don’t match known landmarks. Some apps, like GPS Logger, can record and analyze location histories for inconsistencies. However, advanced spoofing can mimic realistic movement patterns.
Q: Can I jailbreak/root my phone to enable fake GPS if it’s blocked?
Yes, but at significant risk. Rooting bypasses Android’s safety net, exposing you to malware, voiding warranties, and opening backdoors for exploits. Some custom ROMs (like LineageOS) allow mock locations without root, but they require technical expertise and may introduce stability issues.
Q: What happens if I enable fake GPS during a court case?
The consequences vary by jurisdiction, but tampering with location data in legal proceedings can be treated as obstruction of justice or perjury. Courts may dismiss evidence tied to manipulated GPS logs, and prosecutors could pursue charges if the deception aided a crime. Always consult legal counsel before altering location data in high-stakes scenarios.
