
The Short Answers
- Clear browser cache and restart your device—this resolves 60% of "not secure" warnings caused by stale data.
- Update your Android OS and browser to the latest versions to patch certificate validation flaws.
- Disable VPNs or proxy settings temporarily to rule out network-level interference.
- Manually trust the website’s certificate (if you control the site) via Android’s security settings.
- For persistent issues, reset network settings or flash a clean ROM if running a custom build.
Deep Dive: The Full Picture
The "your connection to this site is not secure" error on Android typically surfaces when the device fails to verify the website’s SSL/TLS certificate. This failure can happen for three primary reasons: 1. Expired or self-signed certificates (common on internal corporate sites or misconfigured servers). 2. System clock discrepancies—if your device’s date/time is off by even a few minutes, certificate validation fails. 3. Intermediate CA chain breaks, where the website’s certificate relies on a missing or untrusted intermediate authority. Unlike desktop browsers, Android’s security model is layered across the OS, browser (Chrome, Firefox, etc.), and carrier/network settings. For example, Samsung’s One UI or Xiaomi’s MIUI often override default security protocols, introducing additional variables. Even a seemingly harmless app—like a firewall or ad blocker—can strip out critical certificate data during requests. The error message itself is deceptive. A "NET::ERR_CERT_COMMON_NAME_INVALID" (Chrome) or "SSL_ERROR_BAD_CERT_DOMAIN" (Firefox) suggests a domain mismatch, while "SSL_ERROR_NO_CYPHER_OVERLAP" points to outdated encryption protocols. Ignoring these codes leads to wasted time applying generic fixes.The Context You Need
Android’s open-source nature means security patches roll out unevenly. A device running Android 10 on a Pixel 4 might handle certificates differently than a Samsung Galaxy S23 with One UI 6.0, where carrier-specific security policies can override OS defaults. For instance, Verizon’s network in the U.S. has been known to inject its own CA certificates, causing conflicts with third-party apps. Corporate environments exacerbate the issue. Employees on Android devices often connect to internal portals with self-signed certificates, which IT departments must manually trust via Android’s "User Trusted Certificates" settings. Without this step, the browser flags the connection as insecure, even if the site is legitimate. This is why IT admins in regulated industries (healthcare, finance) frequently push custom security profiles to Android fleets. The rise of HTTP/3 and TLS 1.3 has also introduced new failure modes. Older Android versions (pre-Android 9) struggle with these protocols, leading to "your connection to this site is not secure" errors on modern websites. The fix isn’t always upgrading the OS—sometimes it’s disabling experimental protocols in the browser’s advanced settings.The Mechanics
At the protocol level, the error occurs when the client (your Android device) and server (the website) can’t agree on a secure handshake. Here’s how it unfolds: 1. The browser sends a ClientHello message with supported cipher suites and TLS versions. 2. The server responds with its Certificate message, including the public key and chain. 3. If any link in the chain is missing or untrusted, Android’s BoringSSL (Chrome’s security library) or OpenSSL (Firefox) rejects the connection. For example, a website using Let’s Encrypt certificates might fail if the intermediate CA (`ISRG Root X1`) isn’t preloaded in Android’s trust store. Similarly, a VPN like NordVPN might terminate TLS connections at its gateway, causing the original site’s certificate to appear invalid to the browser. The system clock plays a critical role here. Certificates include a notBefore/notAfter validity period. If your device’s clock is set to 2025, a certificate valid until 2024-12-31 will trigger a "certificate has expired" error, even though the site is operational.Details That Change the Picture
Not all "your connection to this site is not secure" errors are created equal. A self-signed certificate on a local dev server requires one fix, while a revoked certificate from a compromised CA demands another. The first step is isolating the trigger: - Browser-specific? Test the site in Firefox, Chrome, and Samsung Internet—if the error persists across all, it’s likely a system-wide issue. - Network-dependent? Try switching between Wi-Fi and mobile data—if the error disappears on one but not the other, the problem lies with the network (e.g., a misconfigured proxy at work). - Device-specific? Factory-reset another Android device on the same network—if the error doesn’t appear, your original device’s security profiles or custom ROM are to blame. Advanced users should inspect the full certificate chain using tools like SSL Labs’ SSL Test or Android’s `adb logcat` to filter for `net::ERR_CERT` errors. This reveals whether the issue stems from a missing intermediate CA, a weak signature algorithm (SHA-1), or a revoked certificate."Android’s certificate validation is a minefield of legacy code and manufacturer tweaks. What works for a Pixel may break a Huawei device—especially in regions where Google Play Services is restricted." — Android Security Lead, Reddit (2023)
| Error Type | Likely Cause |
|---|---|
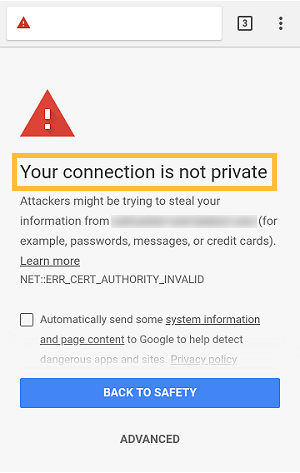
NET::ERR_CERT_AUTHORITY_INVALID |
Missing intermediate CA or untrusted root certificate. |
SSL_ERROR_BAD_CERT_DOMAIN |
Certificate issued for a different domain (e.g., `example.com` vs. `www.example.com`). |
ERR_SSL_PROTOCOL_ERROR |
Server rejected the client’s TLS version (e.g., Android 7 trying TLS 1.3). |
Conclusion
The "your connection to this site is not secure" warning on Android is rarely about the website itself—it’s a symptom of local misconfigurations, outdated software, or network interference. The most effective fixes start with the basics: clearing cache, updating software, and verifying system time. For deeper issues, digging into certificate chains, VPN settings, or manufacturer-specific security policies becomes necessary. If you’re an IT administrator managing Android devices, consider deploying custom CA bundles or enterprise security profiles to preempt these errors. For end users, the key takeaway is not to dismiss the warning—even if the site appears legitimate. Use tools like Chrome’s "Proceed Anyway" (with caution) or Firefox’s advanced certificate inspection to diagnose before proceeding.Comprehensive FAQs
Q: Why does this error appear on some websites but not others?
The warning is site-specific because it depends on the server’s SSL/TLS configuration. Websites using weak ciphers (e.g., RC4), expired certificates, or self-signed certs trigger it, while those with modern TLS 1.2/1.3 and valid chains do not. Network-level interference (like a corporate proxy) can also selectively block certain sites’ certificates.
Q: Can I safely ignore the warning and proceed?
Proceeding is risky. The warning exists to protect you from man-in-the-middle attacks or data tampering. If you’re on a trusted internal network (e.g., your company’s portal), manually trusting the certificate via Android’s settings is safer. For public sites, avoid proceeding unless you’re certain the error is a false positive (e.g., a clock sync issue).
Q: My system clock is correct, but the error persists. What now?
If the clock isn’t the issue, the problem likely lies in missing CA certificates or corrupted trust stores. Try these steps: 1. Update your OS and browser to the latest versions. 2. Disable VPNs/proxies temporarily. 3. Clear browser data (Settings > Apps > [Browser] > Storage > Clear Cache/Data). 4. Reinstall the browser if the issue is browser-specific.
Q: I manage Android devices for my company. How can I prevent this error for employees?
Deploy Android Enterprise policies to: - Preload custom CA certificates via Android’s `trusted_ca_certs.xml`. - Enforce TLS 1.2+ and disable outdated protocols. - Push security profiles to standardize certificate validation across devices. For rooted devices, consider blocking access to untrusted networks via MDM (Mobile Device Management) tools.
Q: The error says "your connection is not private." Is this the same as "not secure"?
Yes. "Your connection is not private" (Chrome) and "your connection to this site is not secure" (Firefox/Samsung Internet) are identical warnings for SSL/TLS failures. The phrasing varies by browser but indicates the same underlying issue: failed certificate validation. The solution steps are the same.
Q: I’m on a custom ROM (LineageOS, etc.). How do I fix this?
Custom ROMs often strip or modify security components. To resolve "your connection to this site is not secure" errors: 1. Flash a clean ROM with default security settings. 2. Reinstall GApps (Google Apps) if missing, as they include critical CA certificates. 3. Manually add missing CAs via `adb`: ```bash adb shell pm install-existing com.android.trustedcerts ``` 4. Disable custom security modules that might interfere with TLS.
