6 Things Worth Knowing About Android Mock Location
The feature’s dual nature—both a testing essential and a potential vector for misuse—makes it a case study in digital trade-offs. Understanding its mechanics, risks, and regulatory landscape is key to grasping why it matters beyond the developer community.1. It’s Built Into Android’s Core Architecture
Android mock location isn’t an afterthought; it’s a deliberate design choice embedded in the Android framework. The `LocationManager` class, part of Android’s core SDK, includes methods like `addTestProvider()` that let developers inject fake location data with metadata such as accuracy and bearing. This isn’t a third-party hack—it’s a sanctioned pathway, documented since early Android versions, that bypasses hardware-level GPS signals entirely. The feature’s persistence across updates reflects its utility. For developers building apps reliant on geolocation—think logistics, weather, or augmented reality—the ability to simulate coordinates without deploying to physical locations saves time and resources. Without it, testing a navigation app’s behavior in a hurricane would require either a hurricane-prone device or a way to replicate the conditions programmatically.2. It’s Heavily Used in Automated Testing
Continuous integration pipelines for Android apps often incorporate android mock location to validate location-based logic. Tools like Espresso and Firebase Test Lab integrate with mock location APIs to verify that an app behaves correctly when the device reports being in Paris, then suddenly in Tokyo. This isn’t just about convenience; it’s about reliability. A single misconfigured location check could cause an app to fail silently in production—something mocking catches early. The practice extends to UI testing. For example, a food delivery app might need to confirm that order suggestions update when the user’s "location" crosses a city boundary. Without mocking, this would require either manual testing across multiple regions or expensive real-world deployments. The trade-off? Developers must ensure their tests account for edge cases where real-world GPS might behave unpredictably—like in urban canyons or underground.3. It’s a Privacy and Security Loophole
Where android mock location excels in testing, it falters in safeguarding user data. Apps with permission to access location data can override it without user consent, creating opportunities for fraud. In 2022, security researchers demonstrated how a malicious app could spoof its location to bypass geofenced restrictions, such as those used in banking apps or regional content locks. The problem isn’t the mocking itself—it’s the lack of transparency when apps use it in production. Google Play’s policies attempt to address this by prohibiting apps that "misrepresent their location" or use mocking to deceive users. However, enforcement relies on user reports, which means many violations likely go unnoticed. The gap between policy and practice highlights a broader issue: android mock location operates in a gray area where technical feasibility outpaces ethical oversight.4. It’s a Regulatory Wildcard
Governments and industry bodies are only beginning to grapple with android mock location’s implications. In the EU, the Digital Services Act (DSA) mandates transparency in how platforms handle user data, but mocking falls into a legal gray zone—neither clearly a privacy violation nor a straightforward tool for fraud. Meanwhile, financial regulators in the UK have flagged location spoofing as a potential risk in anti-money laundering (AML) systems, where geolocation is used to verify transactions. The lack of standardized rules creates a patchwork of compliance. Developers in regions with strict data laws (like GDPR) must treat mock location data as sensitive, while those in less regulated markets may overlook risks entirely. This inconsistency leaves users vulnerable to inconsistent protections, depending on where they live and which apps they use.5. It’s a Double-Edged Sword for App Stores
Platforms like Google Play and Apple’s App Store face a dilemma: android mock location is essential for developers but can enable fraud. Google’s Play Console includes tools to detect suspicious location patterns, but false positives remain a challenge. An app that legitimately tests mock locations during development might get flagged if it accidentally leaves test code in production. The stakes are higher for apps handling sensitive data. For instance, a fitness tracker that spoofs workouts to inflate user stats could mislead advertisers or insurance underwriters. App stores must balance developer needs with user trust, but the lack of clear guidelines leaves them reacting to scandals rather than preventing them.6. It’s Evolving with New Technologies
As Android matures, so does the ecosystem around android mock location. Newer features like Android Emulator’s mock location (via QEMU) allow developers to simulate GPS signals without rooting devices, reducing friction. Meanwhile, machine learning models are being used to detect anomalous location patterns—though these systems themselves rely on mocking for training. The rise of Android’s Location Provider API also introduces granularity. Developers can now mock not just coordinates but also signal strength and satellite data, making simulations more realistic. This evolution reflects a broader trend: as location data becomes more critical, the tools to manipulate it grow more sophisticated—along with the challenges of regulating them.
How These Facts Connect
The interplay between android mock location’s technical utility and its ethical risks reveals a systemic tension in modern app development. On one hand, the feature democratizes testing, reducing barriers for small teams and startups. Without it, location-dependent apps would require prohibitively expensive real-world validation. On the other, its existence creates blind spots in security and compliance, forcing developers to navigate unclear ethical and legal waters. The lack of unified regulations exacerbates the problem. While Google and Apple impose policies, enforcement is reactive, leaving gaps that malicious actors exploit. The result is a fragmented landscape where developers in some regions operate under stricter scrutiny than others, and users have little recourse if their data is compromised. | Aspect | Technical Role | Ethical Risk | Regulatory Status | |--------------------------|---------------------------------------------|--------------------------------------------|-------------------------------------------| | Testing Efficiency | Eliminates need for physical deployments | Potential for test code leaking to prod | No direct restrictions | | Privacy Loophole | Bypasses hardware GPS | Enables fraud, data manipulation | Play Store bans "misrepresentation" | | Automated Validation | Ensures location logic works as intended | Can mask security flaws | No standardized compliance checks | | Fraud Vector | Used by scammers to bypass geofences | Undermines trust in location-based apps | Case-by-case enforcement by platforms | | Regulatory Gray Area | No clear legal definition | Creates inconsistent global protections | EU DSA and AML rules indirectly apply | | Evolving Tech | More realistic simulations via ML | Harder to detect malicious use | No proactive policy frameworks | The table above illustrates how each facet of android mock location intersects with broader challenges in digital trust. The feature’s duality—tool and vulnerability—mirrors larger debates about technology’s role in shaping user behavior and expectations.
Conclusion
Android mock location is more than a developer convenience; it’s a microcosm of the challenges facing digital ecosystems today. Its existence highlights the need for clearer ethical guidelines, stronger enforcement mechanisms, and greater transparency about how apps handle location data. Without these, the balance between innovation and accountability will continue to tip toward the latter’s detriment. The onus isn’t solely on developers or regulators. Users must also demand better safeguards, such as mandatory disclosures when apps use mock locations and independent audits of high-risk applications. As location data becomes increasingly central to digital services, the tools to manipulate it will only grow more powerful—and the stakes for getting it wrong will rise accordingly.Comprehensive FAQs
Q: Can I use android mock location on a non-rooted device?
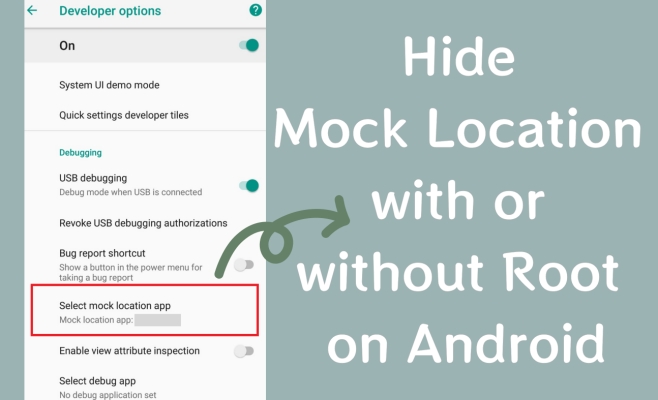
A: Yes, but with limitations. Android’s emulator and tools like am mock-location (part of Android’s platform tools) allow mocking without root access. However, physical devices require enabling developer options and may still trigger security warnings if the mock location deviates drastically from real GPS data.
Q: Are there legal consequences for apps that misuse mock locations?
A: Indirectly. While there’s no specific law targeting android mock location misuse, apps caught deceiving users (e.g., for fraud or ad fraud) can face penalties under existing regulations like the Computer Fraud and Abuse Act (CFAA) in the U.S. or GDPR in the EU. Platforms like Google Play may also ban apps violating their terms.
Q: How do I test if an app is using mock locations?
A: Use tools like adb shell dumpsys location to check active providers. Apps with mock locations will show "mock" in their provider details. Third-party apps like Fake GPS can also help detect spoofing by comparing reported vs. real coordinates.
Q: Can mock locations be detected by servers?
A: Sometimes, but not reliably. Servers can cross-reference IP addresses, Wi-Fi networks, and cell tower data with GPS coordinates to spot inconsistencies. However, determined attackers use VPNs or multiple mock providers to evade detection. No method is foolproof.
Q: Does Apple’s iOS have a similar feature?
A: Yes, but with stricter controls. iOS’s CLLocationManager includes a allowsMockLocation property that must be explicitly enabled in development and disabled in production. Unlike Android, iOS doesn’t allow mocking without developer signing, reducing misuse risks.
Q: What should developers do to avoid policy violations?
A: Remove all mock location code before releasing to production, use static analysis tools to scan for residual test logic, and document location-handling practices. Platforms like Google Play recommend submitting apps with mocking disabled and enabling it only for internal testing.
Q: Are there legitimate use cases beyond app testing?
A: Limited. Some enterprise apps use mock locations for internal simulations (e.g., logistics training), but these are tightly controlled. Most legitimate uses revolve around development—any production use risks violating platform policies or user trust.
